The Cloud Best Build Blueprint: Architecture Secrets for High-Performance Deployments
Table of Contents
- The Complete Overview of Cloud Best Build
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I know if my current cloud architecture qualifies as a cloud best build ?
- Q: Can a cloud best build work for small businesses, or is it only for enterprises?
- Q: What’s the biggest misconception about cloud best build ?
- Q: How do I future-proof my cloud best build against emerging threats?
- Q: Is multi-cloud really necessary for a cloud best build , or is it overkill?
- Q: How can I measure the ROI of a cloud best build ?
The term cloud best build isn’t just corporate jargon—it’s a precision-engineered framework where infrastructure meets business agility. Behind every seamless cloud migration lies a deliberate architecture: the right balance of compute, storage, networking, and automation to handle workloads without overprovisioning or underperformance. This isn’t about chasing the latest hyperscaler feature; it’s about designing for predictable outcomes, where cost, latency, and compliance align under real-world constraints.
The most effective cloud best build strategies share a common thread: they treat cloud as an extension of on-premises systems, not a replacement. Legacy monoliths don’t simply "lift and shift" into the cloud—they’re refactored for microservices, serverless triggers, and hybrid resilience. The difference between a "good" cloud deployment and a best-in-class one often comes down to two factors: observability (knowing when failures will happen before they do) and frictionless scaling (adding capacity without manual intervention). These aren’t optional—they’re table stakes for competitive advantage.
Yet for all its promise, the cloud best build remains misunderstood. Many organizations treat cloud as a "set it and forget it" utility, only to face sticker shock when bills balloon or outages expose gaps in redundancy. The reality? The most robust cloud architectures are antifragile—they don’t just recover from failure; they improve from it. This requires upfront decisions on multi-cloud portability, disaster recovery granularity, and how to bake security into the CI/CD pipeline. The goal isn’t perfection; it’s controlled trade-offs that align with business risk tolerance.
The Complete Overview of Cloud Best Build
The cloud best build refers to the optimized architecture blueprint that maximizes performance, security, and cost-efficiency while minimizing operational overhead. It’s not a one-size-fits-all template but a dynamic framework that adapts to workload patterns—whether that means leveraging Kubernetes for stateful applications or adopting serverless for sporadic tasks. The core principle? Right-sizing resources isn’t about guessing; it’s about data-driven allocation, where monitoring tools like Prometheus or Datadog feed back into auto-scaling policies in real time.What distinguishes a cloud best build from a generic migration? Three pillars: modularity (decoupling components to isolate failures), automation (reducing human error in deployments), and proactive governance (enforcing policies before breaches occur). For example, a financial services firm might deploy a cloud best build with strict IAM segmentation, while a gaming company prioritizes low-latency CDN caching. The architecture isn’t static—it evolves with threat models, regulatory changes, and user behavior. The best builds aren’t built; they’re continuously refined.
Historical Background and Evolution
The concept of cloud best build emerged from the limitations of early cloud adopters, who treated virtual machines as digital servers with the same constraints as physical hardware. By the mid-2010s, organizations realized that cloud’s true value lay in abstraction—separating infrastructure from applications. AWS’s introduction of Lambda in 2014 marked a turning point: for the first time, developers could deploy functions without managing servers, shifting the cloud best build toward event-driven architectures. This wasn’t just a technical shift; it forced a cultural one, where DevOps teams had to rethink how they measured success (e.g., from "uptime" to "time-to-market").The rise of hybrid cloud in the late 2010s added another layer. Enterprises with legacy systems couldn’t rip-and-replace overnight, so the cloud best build had to accommodate interoperability. Tools like Terraform and Ansible became essential for maintaining consistency across on-prem, private cloud, and public cloud environments. Meanwhile, security breaches—like the 2017 AWS S3 outage exposing millions of records—highlighted that a cloud best build isn’t just about performance; it’s about defensive architecture. Today, the most resilient builds incorporate zero-trust principles by default, assuming breach and verifying every request.
Core Mechanisms: How It Works
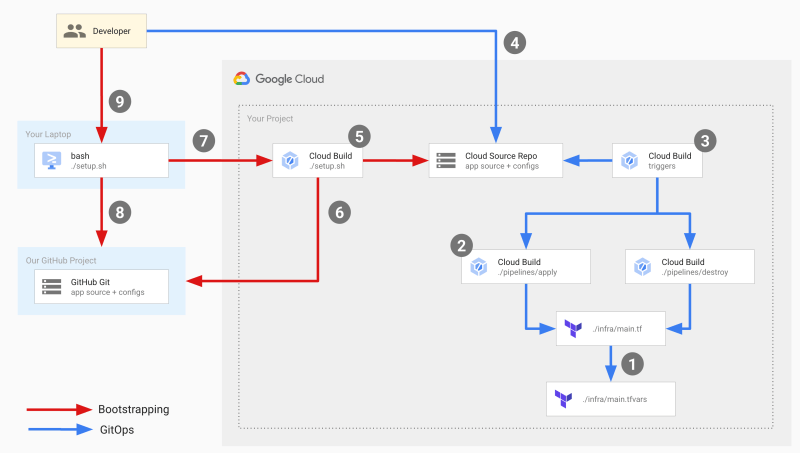
At its foundation, a cloud best build operates on three interconnected layers: infrastructure-as-code (IaC), automated orchestration, and real-time analytics. IaC (via tools like Terraform or Pulumi) ensures that environments are reproducible and version-controlled, eliminating "works on my machine" scenarios. Orchestration platforms like Kubernetes or Nomad handle dynamic workload distribution, while analytics engines (e.g., Grafana) provide visibility into system health. The magic happens when these layers interact: for instance, a sudden traffic spike triggers auto-scaling, which is then logged and analyzed to adjust future capacity forecasts.The cloud best build also relies on policy-as-code, where governance rules (e.g., "no public-facing databases") are enforced via tools like Open Policy Agent (OPA). This shifts security from a post-deployment audit to a first-class citizen in the architecture. For example, a cloud best build for a healthcare provider might include:
Key Benefits and Crucial Impact
The cloud best build delivers measurable advantages beyond cost savings. For startups, it accelerates time-to-market by automating infrastructure provisioning; for enterprises, it reduces downtime by 60–80% through proactive monitoring. The real impact, however, lies in strategic flexibility. A well-architected cloud environment allows companies to pivot quickly—whether that means rerouting traffic during a regional outage or scaling to zero for non-critical workloads. This agility is the difference between reacting to market shifts and leading them.Yet the benefits aren’t uniform. A cloud best build tailored for a SaaS company (with high availability SLAs) will differ sharply from one designed for batch processing (where cost per operation is the priority). The key is aligning the architecture with business outcomes, not just technical metrics. For instance, a retail platform might prioritize edge computing to reduce latency for global users, while a fintech app focuses on immutable audit logs for regulatory compliance.
"Cloud isn’t about moving workloads—it’s about rethinking how those workloads interact with users, data, and each other. The best builds treat cloud as a platform, not just a host." — Martin Casado, former VMware CTO
Major Advantages
- Cost Efficiency: Right-sized resources (e.g., spot instances for fault-tolerant workloads) can cut cloud spend by 30–50% compared to over-provisioned setups. Tools like AWS Cost Explorer help identify underutilized assets.
- Scalability Without Limits: Horizontal scaling via Kubernetes or serverless functions ensures applications handle traffic spikes without manual intervention. Netflix, for example, processes 200M+ requests daily using a cloud best build with auto-scaling groups.
- Disaster Recovery by Design: Multi-region deployments with automated failover (e.g., using AWS Global Accelerator) reduce recovery time objectives (RTO) to minutes, not hours.
- Security as a Feature: Built-in compliance (e.g., HIPAA via AWS Artifact) and runtime protection (like AWS GuardDuty) eliminate the need for bolt-on security tools.
- Developer Productivity: Infrastructure-as-code and CI/CD pipelines (e.g., GitHub Actions + Terraform) allow teams to deploy updates without coordination bottlenecks.
Comparative Analysis
Not all cloud best build approaches are equal. The choice of architecture depends on workload type, budget, and compliance needs. Below is a comparison of key strategies:| Traditional VM-Based Build | Serverless-First Build |
|---|---|
|
|
| Hybrid Cloud Build | Multi-Cloud Build |
|
|

Future Trends and Innovations
The next evolution of cloud best build will be shaped by AI-driven optimization and sustainable infrastructure. Today’s cloud architectures rely on human-defined policies; tomorrow’s will use ML to predict scaling needs before they arise. For example, Google’s Vertex AI already auto-tunes Kubernetes clusters based on workload patterns, reducing waste by 20%. Meanwhile, hyperscalers are introducing carbon-aware computing, where workloads are dynamically routed to regions with renewable energy sources to cut emissions by up to 30%.Another frontier is confidential computing, where data is encrypted in-use (via Intel SGX or AMD SEV), enabling sensitive workloads (e.g., healthcare analytics) to run in shared cloud environments without exposing raw data. This will redefine cloud best build for industries with strict privacy laws. Additionally, the rise of WebAssembly (Wasm) is blurring the line between cloud and edge, allowing serverless functions to run closer to users—reducing latency while maintaining cost efficiency.
Conclusion
The cloud best build isn’t a destination; it’s a continuous process of balancing trade-offs between performance, cost, and security. The most successful architectures today are those that treat cloud as a strategic asset, not just a utility. Whether you’re optimizing for latency, compliance, or scalability, the principles remain: automate everything, monitor proactively, and design for failure. The cloud doesn’t eliminate risk—it redistributes it. The best builds ensure that risk is controlled, not ignored.As organizations mature in their cloud journeys, the focus will shift from "migrating to cloud" to orchestrating cloud-native ecosystems. This means integrating AI/ML for predictive scaling, adopting sustainable practices by default, and ensuring that security is baked into the DNA of the architecture. The cloud best build of 2025 won’t look like today’s—it will be self-healing, self-optimizing, and self-securing.
Comprehensive FAQs
Q: How do I know if my current cloud architecture qualifies as a cloud best build?
A: A cloud best build meets three criteria: (1) Automation (IaC for infrastructure, CI/CD for deployments), (2) Observability (real-time metrics on performance, security, and cost), and (3) Resilience (multi-region failover, chaos engineering tests). Audit your setup against these pillars—tools like AWS Well-Architected Framework or Azure Advisor can help identify gaps.
Q: Can a cloud best build work for small businesses, or is it only for enterprises?
A: Absolutely. A cloud best build scales with need. A startup might use serverless (AWS Lambda) for cost efficiency, while a small e-commerce site could leverage managed databases (like RDS) to avoid DBA overhead. The key is starting with modular components—even a single microservice deployed with auto-scaling is a step toward a best build mindset.
Q: What’s the biggest misconception about cloud best build?
A: Many assume it’s about using the "latest and greatest" cloud tools, but the best builds prioritize stability over novelty. For example, sticking with a proven orchestration tool (like Kubernetes 1.25) over bleeding-edge features often yields better reliability. The goal is predictable performance, not chasing hype.
Q: How do I future-proof my cloud best build against emerging threats?
A: Focus on zero-trust architecture (verify every request, even internally) and immutable infrastructure (no mutable servers). Regularly test for vulnerabilities using tools like OWASP ZAP, and adopt confidential computing for sensitive workloads. Also, monitor cloud provider announcements—features like AWS’s "Nitro Enclaves" for secure workload isolation are game-changers.
Q: Is multi-cloud really necessary for a cloud best build, or is it overkill?
A: Multi-cloud isn’t mandatory, but it reduces lock-in risk. For most organizations, a hybrid approach (e.g., AWS for global reach + Azure for compliance) strikes the right balance. If you’re in a highly regulated industry (e.g., finance), multi-cloud can provide backup options. For others, cloud-agnostic tools (like Terraform) offer portability without full multi-cloud complexity.
Q: How can I measure the ROI of a cloud best build?
A: Track three metrics: (1) Cost per transaction (e.g., $0.05 per API call vs. $0.10), (2) Deployment frequency (e.g., 20 deploys/month vs. 5), and (3) Downtime reduction (e.g., 99.99% uptime vs. 99.9%). Use cloud provider dashboards (AWS Cost Explorer) and APM tools (New Relic) to quantify improvements over time.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.