How Code Analyzer Tools Reshape Modern Software Development
Table of Contents
- The Complete Overview of Code Analyzer Tools
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can code analyzer tools replace manual code reviews?
- Q: How do I choose the right code analyzer for my project?
- Q: What are the most common false positives in code analysis tools ?
- Q: Do code analyzer tools work with legacy codebases?
- Q: How can I integrate code analysis into my CI/CD pipeline?
- Q: Are there open-source alternatives to commercial code analyzer tools ?
Software development has always been a balancing act between speed and precision. The tools developers use to navigate this tension—particularly code analyzer tools—have evolved from simple syntax checkers to sophisticated engines that dissect logic, predict vulnerabilities, and enforce best practices. These tools no longer sit passively in a developer’s toolkit; they actively shape the quality of code before it even reaches production. Their ability to parse millions of lines of code in seconds, flagging everything from performance bottlenecks to security flaws, has made them indispensable in industries where reliability is non-negotiable.
The shift toward automated code analysis tools wasn’t just about fixing bugs faster—it was about redefining what "good code" means. Modern applications demand more than functional correctness; they require resilience against attacks, scalability under load, and maintainability across teams. Code analyzer tools now integrate seamlessly with CI/CD pipelines, shifting left to catch issues early, before they cascade into costly rework. This isn’t just an efficiency play; it’s a strategic advantage for teams competing in a landscape where downtime and vulnerabilities can mean the difference between a thriving product and a failed launch.
Yet, despite their ubiquity, many developers still underutilize these tools—or worse, rely on them blindly without understanding their limitations. The most effective users treat code analysis solutions as collaborative partners, not just automated inspectors. They configure them to align with their team’s coding standards, customize thresholds for false positives, and interpret results with domain expertise. The result? Fewer production fires, cleaner codebases, and a development process that scales with the complexity of modern software.

The Complete Overview of Code Analyzer Tools
Code analyzer tools are the unsung heroes of software engineering, operating behind the scenes to ensure code meets predefined quality benchmarks. At their core, they automate what would otherwise be manual, time-consuming reviews—scanning for syntax errors, logical inconsistencies, and adherence to coding guidelines. But their capabilities extend far beyond basic linting. Advanced code analysis platforms now incorporate static analysis, dynamic analysis, and even machine learning to predict behavioral patterns in code. This evolution has transformed them from reactive bug-finders into proactive quality gatekeepers.
The modern code analyzer ecosystem is fragmented yet interconnected, with tools specializing in specific domains: security scanners like SonarQube, performance profilers like VisualVM, and style enforcers like ESLint. Some operate at the IDE level (e.g., IntelliJ’s built-in analyzers), while others integrate into build systems (e.g., Checkstyle in Maven). The choice of tool often depends on the project’s scale, language, and risk tolerance. For example, a fintech application might prioritize code analysis for security vulnerabilities, while a startup MVP might focus on rapid feedback to accelerate iteration.
Historical Background and Evolution
The origins of code analyzer tools trace back to the 1970s, when early compilers began incorporating basic error-checking mechanisms. Tools like LINT (created for the C programming language in 1979) laid the foundation by flagging undefined variables and potential portability issues. These first-generation analyzers were rudimentary by today’s standards, but they introduced the concept of automated code scrutiny—a radical departure from the ad-hoc debugging methods of the era. By the 1990s, the rise of object-oriented programming and team-based development created demand for more sophisticated code analysis solutions, leading to tools like PC-Lint for C++ and JLint for Java.
The real inflection point came in the 2000s with the adoption of static analysis, which examines code without executing it. Pioneers like Coverity and Fortify Software (acquired by HP) brought enterprise-grade code analyzers to the market, focusing on security and compliance. Meanwhile, open-source projects like PMD and FindBugs democratized access, embedding analysis into the development workflow. The past decade has seen an explosion of cloud-based and AI-driven code analysis tools, such as DeepCode (now CodeGuru) and Snyk, which leverage large datasets to identify patterns that traditional tools miss. Today, the landscape is dominated by a mix of niche specialists and all-in-one platforms, each catering to specific pain points in the software lifecycle.
Core Mechanisms: How It Works
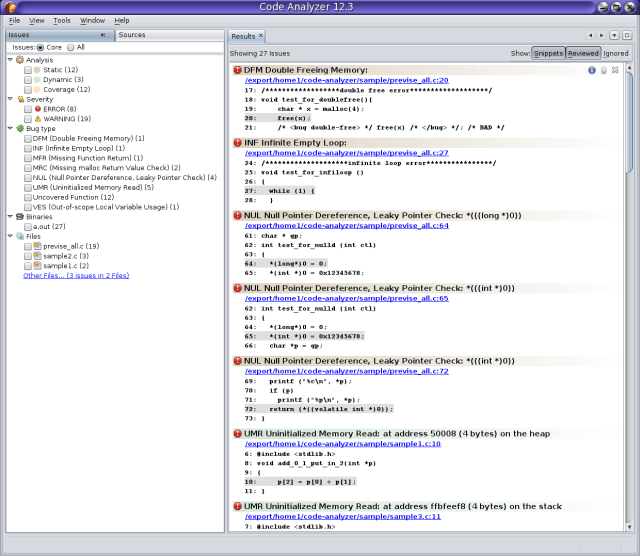
The inner workings of code analyzer tools vary by type, but most share a common pipeline: ingestion, analysis, and reporting. Static analyzers, for instance, parse the Abstract Syntax Tree (AST) of the codebase, applying a series of rules to detect anomalies. These rules can range from simple syntax checks (e.g., missing semicolons) to complex logic evaluations (e.g., detecting null pointer dereferences). Dynamic analyzers, on the other hand, monitor code in runtime, tracking memory usage, thread behavior, and external API interactions. The most advanced code analysis engines combine both approaches, using static analysis to narrow down potential issues and dynamic analysis to validate them under real-world conditions.
Under the hood, these tools rely on a mix of pattern matching, symbolic execution, and data flow analysis. For example, a security-focused code analyzer might use taint analysis to trace how user input propagates through a system, identifying injection vulnerabilities. Performance analyzers often employ profiling techniques to simulate workloads and pinpoint inefficiencies. The output is typically a prioritized list of findings, often categorized by severity (critical, high, medium, low) and accompanied by suggested fixes or references to best practices. Some tools even integrate with version control systems to track how issues evolve across commits, providing historical context for remediation efforts.
Key Benefits and Crucial Impact
The value of code analyzer tools isn’t just in their ability to find bugs—it’s in their capacity to elevate the entire development process. By automating repetitive checks, they free developers to focus on high-level design and innovation. This shift has measurable impacts: teams using code analysis platforms report up to 30% fewer production defects and faster release cycles. The tools also serve as enforcers of consistency, ensuring that codebases adhere to team-specific standards, which is critical for collaboration in distributed teams. Beyond technical merits, they act as a force multiplier for security and compliance, helping organizations meet regulatory requirements without manual audits.
Yet, their influence extends beyond the codebase itself. Code analyzers foster a culture of quality by making feedback immediate and actionable. When a developer receives a real-time alert about a potential memory leak or a security misconfiguration, they’re not just fixing a bug—they’re learning from the tool. This symbiotic relationship between human and machine is what separates reactive debugging from proactive engineering. The tools don’t replace judgment; they sharpen it.
"The most effective code analyzer tools don’t just find problems—they help developers understand why those problems matter and how to avoid them in the future."
Major Advantages
- Early Bug Detection: Catches issues during development, reducing the cost of fixes by up to 100x compared to post-release patches.
- Security Hardening: Identifies vulnerabilities like SQL injection, cross-site scripting (XSS), and buffer overflows before deployment.
- Performance Optimization: Highlights inefficient algorithms, redundant computations, and memory leaks that degrade application speed.
- Compliance Assurance: Ensures adherence to standards like OWASP, HIPAA, and GDPR by flagging non-compliant patterns.
- Knowledge Preservation: Documents codebase quality metrics over time, helping new team members onboard faster.
Comparative Analysis
| Tool | Key Strengths |
|---|---|
| SonarQube | Comprehensive static analysis for 20+ languages; deep security and quality rule sets; integrates with CI/CD. |
| ESLint | Lightweight, JavaScript/TypeScript-focused; highly customizable for team-specific linting rules; IDE plugins available. |
| Checkstyle | Java-centric; enforces coding standards like Google Java Style; plugin-based architecture. |
| DeepCode (AWS CodeGuru) | AI-powered suggestions for code improvements; detects subtle bugs via machine learning; cloud-native. |
Future Trends and Innovations
The next generation of code analyzer tools will blur the line between analysis and synthesis. We’re already seeing early adopters of AI-driven tools that not only detect issues but also generate fixes or suggest alternative implementations. For example, GitHub Copilot’s code completion features are evolving into more robust code analysis assistants, capable of explaining why a particular refactor is risky or how to optimize a query. Meanwhile, the rise of low-code and no-code platforms will demand code analyzers that can evaluate non-traditional workflows, such as drag-and-drop interfaces or serverless functions.
Another frontier is the integration of code analysis tools with DevOps pipelines, where real-time feedback loops will enable continuous compliance and security. Imagine a scenario where every commit triggers an automated review not just for syntax, but for alignment with business goals—such as reducing technical debt or improving accessibility. The tools of tomorrow will also need to adapt to the growing complexity of distributed systems, where issues span microservices, containers, and edge computing. This will require code analyzers that can correlate data across heterogeneous environments, offering a holistic view of system health.
Conclusion
Code analyzer tools have become the backbone of modern software development, bridging the gap between human intent and machine execution. Their evolution reflects broader trends in the industry: the demand for speed without sacrificing quality, the need for security in an era of rampant cyber threats, and the challenge of scaling development across global teams. The most successful organizations treat these tools not as optional luxuries but as essential components of their engineering culture. As the tools themselves grow more intelligent, the onus will shift to developers to leverage them strategically—balancing automation with human insight to build software that is not just functional, but exceptional.
The future of code analysis solutions lies in their ability to anticipate, not just react. Whether through AI-driven predictions, deeper integration with DevOps, or support for emerging paradigms like quantum computing, these tools will continue to redefine what’s possible in software engineering. For developers, the message is clear: mastering code analyzer tools isn’t just about keeping up—it’s about leading the charge.
Comprehensive FAQs
Q: Can code analyzer tools replace manual code reviews?
A: No, they cannot fully replace manual reviews but significantly enhance them. Automated code analyzers excel at catching repetitive or rule-based issues, but human judgment is still required for context-aware decisions, architectural trade-offs, and creative problem-solving. The ideal workflow combines both: tools handle the heavy lifting of consistency checks, while reviewers focus on high-level design and edge cases.
Q: How do I choose the right code analyzer for my project?
A: Selection depends on your tech stack, team size, and priorities. For example:
- Use SonarQube for large-scale, multi-language projects needing deep security and quality analysis.
- Opt for ESLint if you’re working in JavaScript/TypeScript and need lightweight, customizable linting.
- Choose Checkstyle for Java projects adhering to strict coding standards.
- Explore DeepCode if you want AI-driven suggestions for code improvements.
Q: What are the most common false positives in code analysis tools?
A: False positives typically arise from overly broad rules, lack of context, or misconfigured thresholds. Common examples include:
- Flagging null checks in languages where null is explicitly handled (e.g., Kotlin’s nullable types).
- Misinterpreting legacy code patterns as vulnerabilities (e.g., hardcoded credentials in deprecated systems).
- Overzealous security rules that block legitimate use cases (e.g., marking all SQL queries as injection risks).
Q: Do code analyzer tools work with legacy codebases?
A: Yes, but with caveats. Legacy code often lacks documentation or follows outdated patterns, which can trigger excessive false positives. Tools like SonarQube offer "technical debt" tracking to help prioritize refactoring efforts. Start with a subset of critical modules, gradually expanding coverage as the tool learns the codebase’s quirks. Pair analysis with incremental modernization strategies to avoid overwhelming the team.
Q: How can I integrate code analysis into my CI/CD pipeline?
A: Integration typically involves:
- Configuring the tool as a build step (e.g., SonarQube Scanner for Maven/Gradle).
- Setting quality gates to block merges if thresholds are breached (e.g., failing builds on critical vulnerabilities).
- Using plugins to generate reports (e.g., Slack notifications for new issues).
- Leveraging APIs to pull metrics into dashboards (e.g., Jira or Datadog).
Q: Are there open-source alternatives to commercial code analyzer tools?
A: Absolutely. Popular open-source options include:
- PMD: Static analyzer for Java, JavaScript, and more (supports custom rules).
- FindBugs: Java-focused tool for bug detection (now part of SpotBugs).
- Bandit: Security linter for Python.
- PHPStan: Static analyzer for PHP with strict type checking.
- ShellCheck: Linter for shell scripts.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.