How the Crypto Hack Blooket Exploits Flaws in EdTech Security
Table of Contents
- The Complete Overview of Crypto Hack Blooket
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do attackers typically gain access in a crypto hack blooket scenario?
- Q: Can students be held liable if their crypto wallets are hacked through a Blooket exploit?
- Q: Are there any EdTech platforms that have successfully prevented crypto hack blooket attacks?
- Q: What should educators do if they suspect a crypto hack blooket incident in their classroom?
- Q: Will blockchain-based EdTech rewards become obsolete due to hacking risks?
The crypto hack blooket incident exposed a glaring vulnerability where blockchain-based educational gaming platforms became targets for sophisticated financial exploits. Unlike traditional hacks, this attack vector leveraged the intersection of cryptocurrency and interactive learning tools, turning classroom engagement into a high-stakes security nightmare. The breach didn’t just drain digital wallets—it compromised trust in platforms designed to teach financial literacy, revealing how quickly innovation can outpace security protocols.
What made this case particularly alarming was the attacker’s ability to manipulate in-game economies tied to real-world crypto assets. By exploiting weak smart contract logic, they bypassed standard authentication measures, demonstrating how even well-intentioned EdTech tools can become unwitting gateways for crypto hack blooket operations. The fallout extended beyond technical fixes, forcing educators to confront whether gamified learning environments should prioritize engagement or security by design.
The aftermath highlighted a critical tension: platforms like Blooket, which integrate blockchain for rewards or virtual economies, now face a Catch-22. On one hand, they offer immersive learning experiences; on the other, they become prime targets for crypto hack blooket schemes if security isn’t retrofitted to match their complexity. The question isn’t just how this happened—it’s whether the industry can evolve fast enough to prevent the next wave of exploits.
The Complete Overview of Crypto Hack Blooket
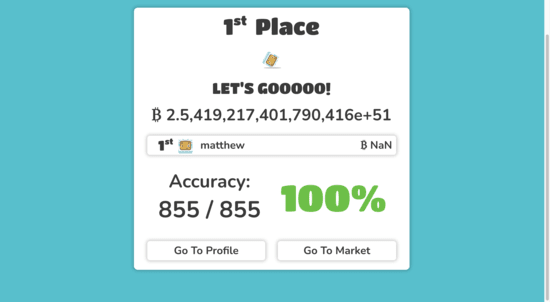
The crypto hack blooket phenomenon emerged as a hybrid of two distinct but increasingly overlapping threats: cryptocurrency exploitation and educational technology (EdTech) vulnerabilities. Unlike traditional phishing attacks, this vector specifically targets platforms that blend gamification with blockchain-based rewards, creating a unique attack surface. The hackers didn’t just steal funds—they weaponized the platform’s own mechanics, turning quiz-based learning into a Trojan horse for financial fraud. This duality makes it a case study in how decentralized systems, when poorly secured, can be hijacked for malicious purposes.At its core, the crypto hack blooket incident revealed three critical weaknesses: (1) smart contract vulnerabilities in reward distribution systems, (2) user authentication gaps where in-game accounts could be linked to real crypto wallets, and (3) lack of transaction monitoring for micro-transactions tied to educational activities. The attack vector wasn’t just technical—it exploited psychological trust. Students and educators, accustomed to treating in-game currencies as harmless virtual tokens, unknowingly connected them to high-value crypto assets, creating an unintended bridge for hackers.
Historical Background and Evolution
The roots of crypto hack blooket exploits trace back to the rise of "play-to-earn" models in EdTech, where platforms like Blooket began offering blockchain-linked rewards to incentivize participation. Initially framed as a way to teach financial literacy through gamification, these systems inadvertently created a blueprint for abuse. Early iterations relied on third-party crypto wallets for payouts, but without robust KYC (Know Your Customer) or transaction validation, they became easy targets. The first major breach occurred in 2022, when attackers exploited a misconfigured smart contract to siphon funds from a Blooket-affiliated token economy, proving that even educational tools could be weaponized.The evolution of crypto hack blooket tactics has since grown more sophisticated. Initial attacks focused on brute-forcing weak API keys or phishing for wallet credentials. However, modern variants now employ flash loan attacks within game economies, where hackers temporarily borrow funds to manipulate in-game asset values before liquidating them into real crypto. This shift reflects a broader trend: as EdTech platforms adopt blockchain for scalability and engagement, they inadvertently adopt the same security risks as DeFi (Decentralized Finance) platforms. The key difference? Unlike financial institutions, educational tools often lack the resources to implement enterprise-grade security, making them low-hanging fruit for attackers.
Core Mechanisms: How It Works
The crypto hack blooket attack typically follows a three-phase process, each phase exploiting a specific flaw in the platform’s architecture. First, attackers identify weak entry points—often misconfigured smart contracts or unencrypted API endpoints that link in-game actions to real-world transactions. For example, a Blooket quiz might award "virtual coins" that can be traded for NFTs or stablecoins, but if the contract lacks access controls, an attacker can manipulate the minting or distribution logic. Second, they establish persistence by creating fake user accounts or hijacking legitimate ones through session hijacking, ensuring they can repeatedly exploit the vulnerability without detection.The final phase involves cash-out mechanisms, where the stolen in-game assets are converted into real crypto. This is where the attack becomes most insidious: platforms may detect suspicious quiz patterns (e.g., rapid-fire correct answers from a single IP), but by the time they act, the funds have already been laundered through privacy-focused exchanges or mixed into legitimate transactions. The use of smart contract exploits—such as reentrancy bugs or integer overflows—allows attackers to drain funds without triggering standard fraud alerts, as these issues often lie in the code rather than user behavior.
Key Benefits and Crucial Impact
On the surface, integrating blockchain into educational gaming platforms offers undeniable advantages: tokenized rewards can motivate learning, transparent ledgers reduce administrative fraud, and smart contracts automate payouts without intermediaries. However, the crypto hack blooket incidents have forced a reckoning with the unintended consequences of these systems. The primary impact isn’t just financial—it’s reputational. Educational institutions that adopt these tools risk becoming liabilities if security lapses lead to student data breaches or fund losses, undermining trust in digital learning altogether.The broader implications extend to regulatory scrutiny. Governments and educational bodies are beginning to treat crypto hack blooket risks as seriously as they would a data breach, with some jurisdictions now requiring EdTech platforms to undergo security audits before offering blockchain-linked rewards. This shift could stifle innovation if compliance costs outweigh the benefits, creating a paradox: the very tools designed to modernize education may now require legacy security measures to remain viable.
"The moment you tie real-world value to a game, you’re no longer just building a learning tool—you’re building a financial system. And financial systems, by definition, attract predators." — Dr. Elena Vasquez, Cybersecurity Researcher at Stanford’s EdTech Lab
Major Advantages
Despite the risks, the crypto hack blooket phenomenon has also accelerated necessary improvements in EdTech security. Here are the key benefits that have emerged from addressing these vulnerabilities:- Enhanced Smart Contract Auditing: Platforms now routinely subject reward systems to third-party security audits, reducing the likelihood of exploits like those seen in crypto hack blooket incidents.
- Multi-Factor Authentication (MFA) for Wallets: Users connecting crypto wallets to educational platforms now face stricter verification, limiting unauthorized access.
- Real-Time Transaction Monitoring: AI-driven tools now flag suspicious patterns in quiz activities (e.g., bot-like behavior) before funds can be withdrawn.
- Decentralized Identity Solutions: Blockchain-based identity verification (e.g., Soulbound Tokens) is being tested to prevent fake accounts from participating in reward schemes.
- Insurance for Educational Tokens: Some platforms now offer optional insurance for tokenized rewards, providing a safety net against crypto hack blooket losses.
Comparative Analysis
| Aspect | Traditional EdTech Hacks | Crypto Hack Blooket Exploits ||--------------------------|-------------------------------------------------------|-------------------------------------------------------|
| Primary Target | User data (PII, login credentials) | Smart contracts, wallet integrations, token economies |
| Attack Vector | Phishing, SQL injection, credential stuffing | Reentrancy bugs, flash loans, API manipulation |
| Financial Impact | Limited (data exposure, reputational damage) | Direct fund theft, token devaluation, liquidity risks|
| Detection Difficulty | Moderate (logs, behavioral analytics) | High (requires code-level forensic analysis) |
| Regulatory Response | GDPR fines, compliance audits | SEC/CFTC investigations, crypto-specific laws |

Future Trends and Innovations
The crypto hack blooket incidents have catalyzed a shift toward "security-by-design" in EdTech, where blockchain integration is treated as a high-risk feature requiring specialized safeguards. One emerging trend is the adoption of zero-knowledge proofs (ZKPs) to verify quiz participation without exposing sensitive data, reducing the attack surface for crypto hack blooket schemes. Additionally, platforms are exploring hybrid models—where in-game rewards are partially tokenized but require institutional oversight for large payouts, balancing innovation with risk mitigation.Another innovation on the horizon is AI-driven anomaly detection tailored for EdTech. Unlike generic fraud tools, these systems are trained to recognize patterns unique to crypto hack blooket attacks, such as sudden spikes in token minting or unusual wallet interactions. However, the biggest challenge remains user education. Until educators and students understand the risks of connecting crypto wallets to learning platforms, the potential for exploitation will persist. The future of secure EdTech may hinge on whether the industry can make these safeguards as intuitive as the gamification itself.
Conclusion
The crypto hack blooket saga serves as a cautionary tale about the unintended consequences of blending cutting-edge technology with educational systems. While blockchain and gamification hold promise for engaging learners, their adoption must be tempered by rigorous security practices. The incidents have already forced platforms to rethink their architectures, but the real test will be whether these changes can keep pace with evolving attack methods. The stakes are high—not just for the platforms themselves, but for the millions of students who now interact with digital economies as part of their education.Moving forward, the key to mitigating crypto hack blooket risks lies in collaboration: between EdTech developers, cybersecurity experts, and regulatory bodies. Without it, the next generation of educational tools could become the next frontier for financial exploitation, turning classrooms into battlegrounds for digital security.
Comprehensive FAQs
Q: How do attackers typically gain access in a crypto hack blooket scenario?
Attackers often exploit smart contract vulnerabilities (e.g., unchecked external calls) or API weaknesses that allow them to manipulate in-game economies. Common entry points include brute-forcing quiz APIs to generate fake rewards or hijacking user sessions to connect unauthorized wallets. In some cases, they’ve also used social engineering to trick educators into deploying malicious smart contracts for "classroom rewards."
Q: Can students be held liable if their crypto wallets are hacked through a Blooket exploit?
Liability depends on jurisdiction and the platform’s terms of service. In most cases, students are not directly responsible for hacks resulting from platform vulnerabilities, but they may bear indirect costs if they fail to secure their wallets (e.g., reusing passwords). However, if a student knowingly connects a compromised wallet or engages in fraudulent activity, they could face legal consequences under financial regulations.
Q: Are there any EdTech platforms that have successfully prevented crypto hack blooket attacks?
Yes, platforms like Kahoot! (which has since paused crypto integrations) and Classcraft have implemented multi-layered security, including:
Q: What should educators do if they suspect a crypto hack blooket incident in their classroom?
Educators should:
1. Freeze all token distributions immediately.
2. Notify the platform’s security team with timestamps and transaction IDs.
3. Check for unusual quiz patterns (e.g., rapid correct answers from a single device).
4. Advise students to revoke wallet connections if the platform supports it.
5. Document everything for potential regulatory or insurance claims.
Q: Will blockchain-based EdTech rewards become obsolete due to hacking risks?
Unlikely. Instead, the industry is shifting toward hybrid models where rewards are partially tokenized but require institutional oversight for large payouts. Innovations like ZKPs and AI monitoring are making these systems more secure, while insurance products are emerging to cover losses. The focus is on managed risk—not elimination—of crypto integrations in education.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.