How Crypto.com API Keys Power Smart Trading & Automation
Table of Contents
- The Complete Overview of Crypto.com API Keys
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I generate a new crypto.com api key ?
- Q: Can I revoke a crypto.com api key without losing access?
- Q: Are crypto.com api keys compatible with third-party trading bots?
- Q: What happens if my crypto.com api key is compromised?
- Q: Do crypto.com api keys support multi-signature authentication?
- Q: Can I use a crypto.com api key for both trading and withdrawals?
- Q: Are there rate limits for crypto.com api keys ?
Crypto.com’s API keys are the backbone of modern cryptocurrency trading, development, and automation. Unlike traditional exchanges where API access is an afterthought, Crypto.com designed its crypto.com api keys with enterprise-grade security and granular permissions—allowing users to interact with the platform programmatically without exposing sensitive credentials. Whether you’re building a trading bot, integrating payment systems, or accessing market data, these keys act as the digital gateway between your application and Crypto.com’s infrastructure.
The platform’s approach to crypto.com api keys stands out in an industry where security breaches and misconfigured permissions remain persistent risks. Unlike competitors that treat API access as a secondary feature, Crypto.com embeds multi-layered authentication, rate-limiting, and IP whitelisting directly into its crypto.com api keys system. This isn’t just about functionality; it’s about control. Developers and traders can restrict access to specific endpoints, enforce two-factor authentication (2FA) at the key level, and even set expiration dates—features that turn a simple API key into a fortified access token.
For institutions and high-volume traders, the stakes are even higher. A single exposed crypto.com api key can lead to unauthorized trades, fund drainage, or data leaks. Crypto.com mitigates this by offering dedicated support for institutional clients, including custom API key policies and real-time monitoring. Meanwhile, retail users benefit from a balance of accessibility and security, with options to generate read-only keys for analytics or full-access keys for trading—all while maintaining audit trails for every transaction.
The Complete Overview of Crypto.com API Keys
Crypto.com’s crypto.com api keys serve as the primary interface between third-party applications and the exchange’s backend systems. These keys are not static credentials but dynamically managed tokens that can be revoked, restricted, or reassigned without disrupting service. Unlike traditional password-based authentication, crypto.com api keys leverage OAuth 2.0 principles, allowing users to delegate specific permissions (e.g., trading, withdrawals, or account balance checks) without sharing their primary login details. This modularity is critical for developers building multi-functional applications, as it enables fine-grained access control—preventing a single compromised key from granting full system access.The platform’s API ecosystem is divided into two primary tiers: the Public API (for market data, price feeds, and blockchain information) and the Private API (requiring crypto.com api keys for authenticated actions like trades or withdrawals). Public endpoints are rate-limited but freely accessible, while private endpoints enforce stricter quotas and require key-based authentication. This segmentation ensures that even if a crypto.com api key is exposed, an attacker cannot bypass the platform’s rate limits or access sensitive operations without additional credentials.
Historical Background and Evolution
Crypto.com’s approach to crypto.com api keys evolved in response to early 2010s security failures where exchanges suffered from mass withdrawals due to stolen API keys. Recognizing the need for a more robust system, the platform adopted a zero-trust architecture, where every API request is authenticated, logged, and subject to real-time risk assessment. Early versions of the API relied on basic API secret pairs (public/private keys), but these were quickly phased out in favor of more secure OAuth 2.0 tokens—similar to those used by major cloud providers like AWS or Google.A turning point came in 2020, when Crypto.com introduced IP whitelisting and key expiration features for institutional clients. These updates allowed enterprises to lock down crypto.com api keys to specific server IPs and enforce automatic deactivation after a set period. For retail users, the platform simplified key management by integrating API key generation directly into the mobile app and web dashboard, reducing the friction of manual configuration. Today, the system supports over 100 endpoints, covering everything from spot trading to staking automation, reflecting Crypto.com’s growth from a niche exchange to a global financial infrastructure provider.
Core Mechanisms: How It Works
At its core, a crypto.com api key functions as a cryptographic identifier paired with a secret signature. When an application makes a request to Crypto.com’s API, it signs the request using the private key, and the platform verifies the signature against the stored public key. This process ensures that only authorized applications can execute actions on behalf of the user. Additionally, Crypto.com’s API enforces HMAC-SHA256 for request signing, a standard in enterprise-grade security that prevents replay attacks and man-in-the-middle exploits.Beyond basic authentication, crypto.com api keys integrate with the platform’s Two-Factor Authentication (2FA) system. This means that even if a key is compromised, an attacker would still need the user’s 2FA code to execute sensitive operations like withdrawals. For high-risk actions (e.g., large transfers), Crypto.com may require additional manual approvals, adding another layer of defense. The system also maintains detailed logs of all API activity, allowing users to audit their crypto.com api keys for suspicious behavior—such as unauthorized trades or data access attempts.
Key Benefits and Crucial Impact
The adoption of crypto.com api keys has redefined how traders, developers, and institutions interact with cryptocurrency platforms. For automated trading firms, these keys eliminate the need for manual intervention, enabling high-frequency strategies that react to market conditions in real time. Meanwhile, developers leverage crypto.com api keys to build custom dashboards, payment processors, and analytics tools—extending the platform’s functionality beyond its native interface. The result is a symbiotic relationship where Crypto.com’s infrastructure becomes a programmable resource, rather than a static exchange.Security remains the most compelling advantage. Unlike traditional exchanges where API keys are often treated as secondary credentials, Crypto.com treats crypto.com api keys with the same rigor as login passwords. Features like temporary key generation, permission-based restrictions, and real-time monitoring ensure that even in the event of a breach, the damage is contained. This level of security is particularly critical for institutional clients, who often face regulatory scrutiny over their API access policies.
"The difference between a secure API key and a vulnerability is often just one misconfigured permission. Crypto.com’s system flips that script by making security the default, not an afterthought." — Alex M., Head of Security at a Top Crypto Fund
Major Advantages
- Granular Permissions: Assign read-only, trade-only, or withdrawal-specific access to crypto.com api keys, reducing attack surfaces.
- Multi-Layered Authentication: Combine API keys with 2FA and IP restrictions for defense-in-depth security.
- Real-Time Monitoring: Crypto.com’s dashboard tracks API activity, alerting users to unusual patterns or unauthorized access.
- Scalability: Institutional-grade rate limits and quotas prevent API abuse, even for high-volume applications.
- Seamless Integration: SDKs and libraries for Python, JavaScript, and Java simplify crypto.com api keys implementation in custom projects.
Comparative Analysis
| Feature | Crypto.com API Keys | Competitor APIs |
|---|---|---|
| Permission Granularity | Endpoint-level restrictions (e.g., disable withdrawals while allowing trades). | Often limited to read/write or full access. |
| Security Model | OAuth 2.0 + HMAC-SHA256 + 2FA integration. | Basic API secret pairs or outdated HMAC-SHA1. |
| Key Expiration | Customizable expiration dates for temporary keys. | Rarely supported; keys often permanent. |
| Institutional Support | Dedicated API policies, IP whitelisting, and compliance tools. | Generic solutions with limited customization. |

Future Trends and Innovations
The next phase of crypto.com api keys will likely focus on zero-trust architecture, where every API request—even from whitelisted IPs—is dynamically authenticated using short-lived tokens. This approach, already adopted by cloud providers, would further reduce the risk of credential theft. Additionally, Crypto.com may introduce blockchain-anchored API keys, where key permissions are stored on-chain, enabling immutable audit trails and cross-platform compatibility.For developers, expect deeper integration with smart contract platforms (e.g., Ethereum, Solana), allowing crypto.com api keys to interact directly with DeFi protocols. This would bridge the gap between traditional exchanges and decentralized finance, offering a unified API for both centralized and decentralized operations. Meanwhile, AI-driven anomaly detection could automatically revoke compromised crypto.com api keys before damage occurs, turning security from a reactive measure into a predictive one.
Conclusion
Crypto.com’s crypto.com api keys represent more than just a technical feature—they embody the platform’s commitment to security, scalability, and developer-friendly design. By treating API access as a first-class citizen, Crypto.com has set a new standard for how exchanges should handle programmable interactions. For traders, the ability to automate strategies with secure crypto.com api keys is a game-changer. For developers, the granular controls and robust security make integration seamless. And for institutions, the compliance-ready framework ensures adherence to regulatory demands without sacrificing functionality.As the cryptocurrency ecosystem matures, the role of crypto.com api keys will only expand. From powering institutional-grade trading bots to enabling cross-chain DeFi integrations, these keys are the silent enablers of the next generation of financial innovation. The key takeaway? In an industry where security breaches are inevitable, Crypto.com’s approach to crypto.com api keys turns a potential liability into a competitive advantage.
Comprehensive FAQs
Q: How do I generate a new crypto.com api key?
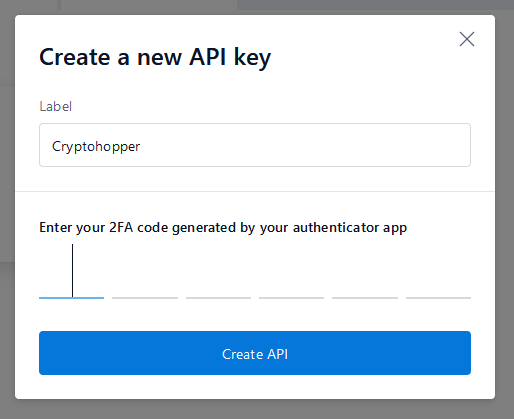
A: Navigate to the "API" section in your Crypto.com account dashboard. Click "Create API Key," select the permissions (e.g., trading, withdrawals), and optionally set an expiration date. Confirm with 2FA for security.
Q: Can I revoke a crypto.com api key without losing access?
A: Yes. In the API management dashboard, locate the key and select "Revoke." This immediately deactivates the key while preserving your account access. Always generate a new key if revoking an active one in use by an application.
Q: Are crypto.com api keys compatible with third-party trading bots?
A: Absolutely. Crypto.com provides official SDKs for Python, JavaScript, and Java, along with REST API documentation. Popular bots like 3Commas or Hummingbot support Crypto.com’s API endpoints, but ensure your bot’s rate limits align with Crypto.com’s quotas.
Q: What happens if my crypto.com api key is compromised?
A: Immediately revoke the key and rotate it. Enable 2FA on your account, check recent API activity for unauthorized actions, and contact Crypto.com’s support if large transactions occurred. For added security, use IP whitelisting to restrict key usage to trusted servers.
Q: Do crypto.com api keys support multi-signature authentication?
A: Not natively, but you can simulate multi-signature logic by generating separate keys for different functions (e.g., one for trades, another for withdrawals) and requiring manual approval for high-risk actions. Institutional clients may request custom solutions via Crypto.com’s enterprise support.
Q: Can I use a crypto.com api key for both trading and withdrawals?
A: Yes, but it’s a security risk. Instead, generate a dedicated key for withdrawals with only the necessary permissions. This limits potential damage if the key is exposed. Always follow the principle of least privilege when assigning API permissions.
Q: Are there rate limits for crypto.com api keys?
A: Yes. Public endpoints have lower limits (e.g., 10 requests/second), while private endpoints vary by account tier. Institutional clients receive higher quotas. Check Crypto.com’s API documentation for exact limits and adjust your application’s request frequency accordingly.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.