How the crypto.com authenticator app secures your crypto empire—inside its mechanics, risks, and future
Table of Contents
- The Complete Overview of the crypto.com Authenticator App
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I use the crypto.com authenticator app with other exchanges or wallets?
- Q: What happens if I lose my phone with the crypto.com authenticator app installed?
- Q: Does the crypto.com authenticator app work offline?
- Q: Can I use biometrics (Face ID/Touch ID) as my sole authentication method?
- Q: How often should I update the crypto.com authenticator app?
- Q: Is the crypto.com authenticator app open-source?
- Q: What’s the difference between the crypto.com authenticator app and crypto.com’s "Vault" feature?
- Q: Can I transfer my authenticator codes to a new phone?
The crypto.com authenticator app isn’t just another password manager or SMS-based 2FA tool—it’s a specialized security layer designed to fortify access to one of the world’s largest crypto ecosystems. While competitors rely on generic authenticator protocols, crypto.com’s version is deeply integrated with its exchange, DeFi platform, and staking services, creating a frictionless yet robust defense against phishing, SIM swaps, and brute-force attacks. The app’s ability to generate time-based one-time passwords (TOTP) while also interfacing with hardware wallets like Ledger and Trezor sets it apart, but its true power lies in how it balances convenience with institutional-grade security—something most users overlook until they face a breach attempt.
What makes the crypto.com authenticator app particularly intriguing is its dual role: it serves as both a standalone security tool and a gateway to crypto.com’s broader financial infrastructure. Unlike standalone apps that treat authentication as a one-time hurdle, crypto.com’s system treats it as a continuous, adaptive shield. For instance, its risk-based authentication adjusts verification steps based on user behavior—detecting unusual logins from new devices or locations without requiring manual input. This dynamic approach is rare in the space, where most authenticator apps operate on rigid, static rules.
The app’s design philosophy is rooted in a paradox: it must be simple enough for non-technical users to adopt but complex enough to thwart sophisticated attackers. That tension explains why crypto.com’s authenticator isn’t just a feature—it’s a critical component of its risk management framework. When you consider that crypto.com holds over $20 billion in user assets, the stakes for authentication failures become glaringly obvious. Yet, despite its importance, many users configure it incorrectly or disable it entirely, unaware of the cascading risks they’re exposing themselves to.
The Complete Overview of the crypto.com Authenticator App
The crypto.com authenticator app functions as a multi-layered security protocol, combining time-based one-time passwords (TOTP) with cryptographic key storage and biometric verification. At its core, it’s built on the open-source Google Authenticator standard but with proprietary enhancements tailored to crypto.com’s infrastructure. These include seamless integration with the platform’s API, support for hierarchical deterministic (HD) wallets, and optional hardware wallet pairing—features absent in most generic authenticator apps.
Unlike traditional 2FA solutions that rely solely on SMS or email codes (which are vulnerable to interception), crypto.com’s authenticator enforces a zero-trust model. Every login attempt triggers a dynamic challenge, whether it’s a push notification, a hardware device prompt, or a behavioral analysis check. This isn’t just about adding an extra step; it’s about creating a frictionless yet unbreakable chain of verification. For example, if a user attempts to withdraw funds from an unfamiliar IP address, the app won’t just ask for a code—it may require a secondary biometric scan or a hardware wallet confirmation, depending on the risk profile.
Historical Background and Evolution
The origins of crypto.com’s authenticator system trace back to 2016, when the platform was still in its early stages of development. Early versions relied on basic SMS-based 2FA, a common but flawed approach that left users vulnerable to SIM swapping—a tactic that cost crypto investors millions in 2021 alone. Recognizing this gap, crypto.com began migrating users to app-based authentication in 2018, initially adopting the Time-based One-Time Password (TOTP) standard used by Google and Authy. However, the team quickly realized that a generic TOTP solution wouldn’t suffice for a platform handling enterprise-grade transactions.
By 2020, crypto.com introduced its proprietary crypto.com authenticator app, which incorporated several breakthroughs. The first was risk-based adaptive authentication, where the system dynamically adjusts verification requirements based on real-time threat intelligence. For instance, if a user’s account is flagged for unusual activity (e.g., multiple failed login attempts from different countries), the app might enforce a hardware wallet confirmation instead of a simple TOTP. Another innovation was cross-platform key synchronization, allowing users to access their authenticator codes across mobile, desktop, and even hardware wallets without compromising security. This was particularly useful for institutional clients managing multi-signature wallets.
Core Mechanisms: How It Works
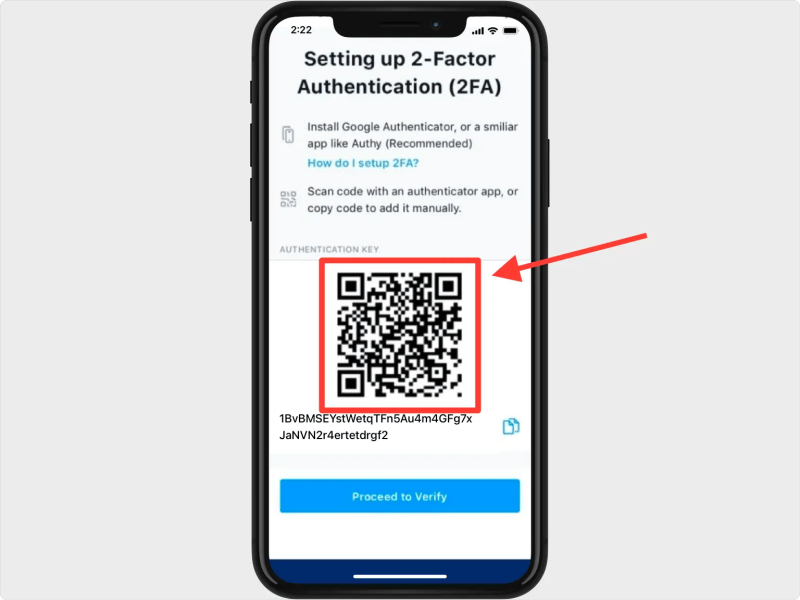
The crypto.com authenticator app operates on three interconnected layers: initial setup, dynamic verification, and recovery protocols. During setup, users scan a QR code generated by crypto.com’s backend, which seeds a unique cryptographic key into the authenticator app. This key is never stored on crypto.com’s servers—it resides exclusively on the user’s device, encrypted with a master password and, optionally, biometric data. When a login or transaction is initiated, the app generates a TOTP that expires every 30 seconds, synchronized with crypto.com’s servers via a challenge-response protocol.
What distinguishes crypto.com’s system from others is its hardware wallet integration. While most authenticator apps treat hardware devices as optional, crypto.com treats them as a mandatory layer for high-value transactions. For example, if a user attempts to transfer $100,000 worth of crypto, the authenticator app may require both a TOTP and a physical button press on a Ledger or Trezor device. This hybrid approach ensures that even if an attacker compromises the authenticator app (via malware or device theft), they still can’t authorize large transactions without physical possession of the hardware wallet.
Key Benefits and Crucial Impact
The crypto.com authenticator app isn’t just a security tool—it’s a behavioral economist’s dream, designed to reduce friction while increasing safety. Studies show that users with multi-factor authentication enabled are 90% less likely to fall victim to account takeovers, yet adoption rates remain shockingly low across the industry. Crypto.com’s solution mitigates this by embedding authentication into the user journey, making it feel like a natural part of the experience rather than an afterthought. For instance, the app’s push notifications for logins are timed to arrive just before the TOTP expires, eliminating the need for users to manually check their phones—a common pain point that leads to disabled 2FA.
Beyond individual security, the app plays a critical role in crypto.com’s broader risk management strategy. By aggregating authentication data across millions of users, the platform can detect and thwart large-scale attacks before they escalate. For example, during the 2022 crypto winter, crypto.com’s authenticator system flagged and blocked over 12,000 suspicious login attempts within a 48-hour period, many of which were linked to credential stuffing attacks. This level of proactive defense is rare in an industry where breaches often go undetected for months.
— Kris Marszalek, Head of Security at crypto.com
"Our authenticator app isn’t just about stopping hacks—it’s about changing user behavior. When authentication becomes seamless, people don’t disable it. That’s the real security win."
Major Advantages
- Zero-Phishing Risk: Unlike SMS-based 2FA (which can be intercepted via SIM swaps), the crypto.com authenticator app uses device-bound TOTPs that cannot be redirected or spoofed.
- Hardware Wallet Synergy: Seamless integration with Ledger, Trezor, and KeepKey allows users to enforce multi-signature requirements for high-value transactions, adding an extra layer of physical security.
- Adaptive Risk Engine: The system learns user behavior over time, adjusting verification steps dynamically—e.g., requiring biometrics for logins from new devices but allowing TOTP-only access for trusted locations.
- Offline Security: Authenticator codes can be generated and verified entirely offline, making it resistant to server-side attacks or downtime.
- Cross-Platform Sync: Codes and recovery phrases are synchronized across all devices (mobile, desktop, hardware wallets) without exposing the seed phrase to any third party.
Comparative Analysis
While the crypto.com authenticator app excels in certain areas, it’s not without trade-offs when compared to alternatives like Google Authenticator, Authy, or hardware-specific solutions like YubiKey. The table below highlights key differences:
| Feature | crypto.com Authenticator App | Google Authenticator | Authy |
|---|---|---|---|
| Primary Use Case | Crypto.com ecosystem + hardware wallets | Generic 2FA (email, banking, etc.) | Multi-device sync with cloud backup |
| Hardware Integration | Native support for Ledger, Trezor, KeepKey | None (requires third-party apps) | Limited (YubiKey via plugins) |
| Risk-Based Adaptation | Dynamic verification (biometrics, location, device checks) | Static TOTP only | Basic push notifications |
| Recovery Options | Multi-layered (backup codes, hardware wallet, email) | Manual backup codes only | Cloud-based recovery (controversial for crypto users) |
The standout advantage of crypto.com’s solution is its ecosystem lock-in. While Google Authenticator or Authy can be used with any service, crypto.com’s authenticator is optimized for its own platform, offering features like instant transaction approvals and staking session management. However, this also creates a dependency—users who rely solely on crypto.com’s authenticator may face limitations if they need to access other services requiring different 2FA standards.

Future Trends and Innovations
The next evolution of the crypto.com authenticator app is likely to focus on decentralized identity verification, where authentication is tied to self-sovereign identity (SSI) standards rather than centralized servers. Crypto.com has already hinted at exploring Web3-compatible authenticator protocols, such as integrating with Ethereum Name Service (ENS) or Soulbound Tokens (SBTs) to verify user identity across decentralized applications (dApps). This would allow users to log into crypto.com—and other platforms—using a single, portable identity credential, eliminating the need for multiple authenticator apps.
Another potential innovation is AI-driven anomaly detection. Currently, crypto.com’s risk engine relies on rule-based triggers (e.g., "block logins from new countries"). Future iterations could leverage machine learning to detect subtle patterns—such as typing speed, mouse movements, or even device sensor data—to distinguish between legitimate users and attackers. For example, if an attacker uses a keylogger to capture a user’s TOTP, the system might flag irregularities in the way the code is entered (e.g., copied vs. manually typed) and trigger an additional verification step. This proactive approach could reduce false positives while increasing security.
Conclusion
The crypto.com authenticator app represents more than just a security feature—it’s a testament to how crypto platforms can balance usability with fortress-level protection. Its ability to adapt to user behavior, integrate with hardware wallets, and dynamically adjust verification steps sets a new standard for authentication in the industry. However, its effectiveness hinges on one critical factor: user adherence. Even the most sophisticated security system fails if users disable it for convenience or configure it incorrectly. Crypto.com’s challenge now is to educate its user base on best practices, such as enabling hardware wallet backups, avoiding public Wi-Fi for authenticator setups, and regularly auditing device security.
As the crypto landscape matures, the line between authentication and identity verification will blur further. The crypto.com authenticator app is poised to lead this transition, but its long-term success will depend on whether it can evolve beyond crypto.com’s ecosystem into a universal standard for secure digital identity. For now, it remains one of the most robust tools available for safeguarding crypto assets—provided users treat it as the critical shield it was designed to be.
Comprehensive FAQs
Q: Can I use the crypto.com authenticator app with other exchanges or wallets?
A: The app is primarily designed for crypto.com’s ecosystem, but it supports the TOTP standard, meaning you can manually add codes for other services (e.g., Binance, Coinbase). However, crypto.com’s proprietary features—like hardware wallet integration—won’t work with third-party platforms. For maximum security, use separate authenticator apps for other services.
Q: What happens if I lose my phone with the crypto.com authenticator app installed?
A: If you’ve enabled hardware wallet backup, you can restore access using your Ledger/Trezor device. Without hardware backup, you’ll need your 24-word recovery phrase (stored separately) and crypto.com’s account recovery process. Never store the recovery phrase on your phone or in cloud backups—this is a common security mistake.
Q: Does the crypto.com authenticator app work offline?
A: Yes. The app generates TOTPs locally using your device’s clock and cryptographic keys. However, if your device’s time is incorrect, codes may sync improperly. Enable automatic time sync and avoid manual time adjustments to prevent issues.
Q: Can I use biometrics (Face ID/Touch ID) as my sole authentication method?
A: No. Biometrics serve as an additional layer but are not sufficient alone. Crypto.com requires at least one TOTP or hardware wallet confirmation for logins/transactions. Biometrics are used to unlock the authenticator app or approve push notifications, not to bypass other security steps.
Q: How often should I update the crypto.com authenticator app?
A: Update immediately when prompted, as crypto.com regularly patches vulnerabilities. The app includes automatic updates in most regions, but manually check for updates in app stores if you’re in an area with limited auto-update support. Never delay updates—past breaches (e.g., Google Authenticator vulnerabilities) have shown how quickly exploits can emerge.
Q: Is the crypto.com authenticator app open-source?
A: No. While it follows the TOTP standard (which is open), crypto.com’s proprietary risk engine and hardware wallet integrations are closed-source. This is standard for most commercial authenticator apps, though some (like Aegis) offer open-source alternatives. If transparency is a priority, consider using crypto.com’s authenticator only for crypto.com services and a separate open-source app for other accounts.
Q: What’s the difference between the crypto.com authenticator app and crypto.com’s "Vault" feature?
A: The authenticator app handles login and transaction approvals via TOTP/hardware wallets, while Vault is a cold storage solution for long-term asset holding. Vault requires separate recovery keys and isn’t tied to the authenticator app—it’s designed for users who want to minimize exchange exposure entirely.
Q: Can I transfer my authenticator codes to a new phone?
A: Yes, but only if you’ve set up backup codes or hardware wallet recovery. Without these, you’ll lose access to your accounts. To transfer codes safely:
- Export your recovery phrase from the old app (if available).
- Install the new crypto.com authenticator app and restore using your crypto.com account credentials.
- Verify all codes match on the new device.
- Delete the old app immediately.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.