How Cybersecurity Testing Shields Modern Systems
Table of Contents
- The Complete Overview of Cybersecurity Testing
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How often should cybersecurity testing be conducted?
- Q: What’s the difference between a penetration test and a vulnerability scan?
- Q: Can AI replace human cybersecurity testers?
- Q: How do I choose a cybersecurity testing provider?
- Q: What are the most common mistakes in cybersecurity testing?
Cybersecurity testing isn’t just a technical exercise—it’s a strategic imperative. Organizations that treat it as an afterthought risk catastrophic breaches, financial losses, and reputational collapse. The stakes are higher than ever: ransomware attacks surged 93% in 2023 alone, and the average cost of a data breach now exceeds $4.45 million. Yet, many companies still rely on outdated audits or superficial scans, leaving critical gaps in their defenses.
The reality is that cybersecurity testing must evolve alongside threats. Static assessments no longer suffice when adversaries deploy zero-day exploits and AI-powered phishing campaigns. The most resilient systems combine automated scans with manual penetration tests, red-team exercises, and continuous monitoring—each serving a distinct purpose in the broader security posture.
What separates effective cybersecurity testing from a checkbox exercise? It’s the fusion of technology and human expertise. Tools can identify vulnerabilities, but only skilled analysts can exploit them realistically, simulate targeted attacks, and uncover flaws in system logic. The difference between a false positive and a genuine threat often hinges on this nuance.
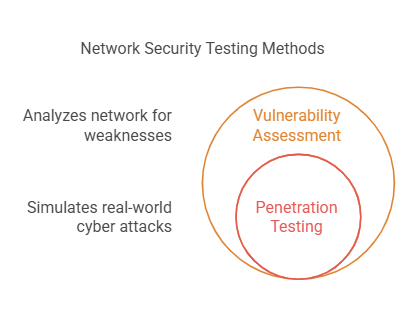
The Complete Overview of Cybersecurity Testing
Cybersecurity testing encompasses a spectrum of methodologies designed to identify, exploit, and remediate vulnerabilities before malicious actors do. At its core, it’s about simulating real-world attacks to stress-test defenses, from network perimeters to application layers. The discipline spans structured frameworks like NIST’s Risk Management Framework (RMF) and ISO 27001, but its execution varies—ranging from automated vulnerability scans to full-scope penetration tests conducted by ethical hackers.The goal isn’t just compliance; it’s resilience. A well-structured cybersecurity testing program forces organizations to confront uncomfortable truths: Are their firewalls configured correctly? Do developers inadvertently embed hardcoded credentials in code? Can an attacker pivot laterally once inside the network? These questions don’t have binary answers—they demand iterative testing, prioritization, and remediation based on risk severity.
Historical Background and Evolution
The origins of cybersecurity testing trace back to the 1970s, when early computer networks faced rudimentary threats like buffer overflows and password-cracking tools. The first documented penetration test was conducted by the U.S. Department of Defense in 1983, a response to growing concerns about military systems being compromised by hackers. By the 1990s, as the internet commercialized, so did cybercrime—leading to the rise of ethical hacking as a formal discipline.The turn of the millennium brought regulatory mandates, most notably the Sarbanes-Oxley Act (2002) and the EU’s General Data Protection Regulation (GDPR) in 2018. These laws didn’t just impose fines for breaches; they mandated cybersecurity testing as a prerequisite for compliance. Meanwhile, the cybersecurity industry professionalized: certifications like CEH (Certified Ethical Hacker) and OSCP (Offensive Security Certified Professional) emerged to standardize skills. Today, cybersecurity testing is a $12 billion market, driven by ransomware, supply-chain attacks, and the proliferation of IoT devices—each introducing new attack surfaces.
Core Mechanisms: How It Works
At its foundation, cybersecurity testing relies on two complementary approaches: active and passive assessments. Active testing—such as penetration testing or red-teaming—simulates attacks by exploiting vulnerabilities in live environments. Passive methods, like static code analysis or log reviews, analyze systems without direct interaction. The choice depends on risk tolerance: active tests reveal exploitable flaws but may disrupt production; passive tests are safer but can miss runtime vulnerabilities.The process begins with reconnaissance, where testers map the target’s digital footprint using tools like Shodan or Maltego. Next comes vulnerability scanning (e.g., Nessus, OpenVAS) to identify known weaknesses, followed by exploitation—where ethical hackers leverage frameworks like Metasploit to demonstrate real-world impact. The final phase, reporting, translates technical findings into actionable remediation steps, often tied to business risk (e.g., "This SQL injection flaw could lead to customer data theft, costing $X in fines and reputational damage").
Key Benefits and Crucial Impact
The primary value of cybersecurity testing lies in its ability to prevent breaches rather than react to them. Traditional incident response is reactive; proactive testing shifts the advantage to defenders. Organizations that integrate cybersecurity testing into their SDLC (Software Development Lifecycle) reduce breach costs by up to 60%, according to IBM’s 2023 Cost of a Data Breach Report. Beyond cost savings, it mitigates legal exposure, customer trust erosion, and operational downtime—factors that can sink a business faster than a single attack.Yet, the benefits extend beyond risk mitigation. Cybersecurity testing also serves as a competitive differentiator. In industries like finance and healthcare, where compliance is non-negotiable, third-party audits and certifications (e.g., SOC 2, HIPAA) hinge on rigorous testing. Even in less regulated sectors, clients increasingly demand proof of security—making cybersecurity testing a market entry requirement.
"The best cybersecurity isn’t a product; it’s a process. And the only way to validate that process is through relentless, adversarial testing." — Bruce Schneier, Security Technologist
Major Advantages
- Early Detection of Zero-Days: Automated scans and manual penetration tests uncover unknown vulnerabilities before exploit code is leaked on dark web forums.
- Compliance Alignment: Frameworks like PCI DSS and NIST 800-53 require cybersecurity testing—failure to comply can result in legal action or contract termination.
- Reduced Attack Surface: Continuous testing identifies misconfigurations (e.g., open RDP ports, default credentials) that attackers exploit within minutes of exposure.
- Improved Incident Response: By simulating breaches, teams practice containment strategies, reducing mean time to detect (MTTD) and recover (MTTR).
- Enhanced Stakeholder Trust: Publicly disclosing cybersecurity testing results (e.g., bug bounty programs) signals transparency and attracts security-conscious partners.
Comparative Analysis
| Method | Use Case |
|---|---|
| Penetration Testing | Simulates targeted attacks to validate defenses (e.g., phishing, network intrusion). Best for high-risk assets like payment systems. |
| Vulnerability Scanning | Automated detection of known flaws (CVE databases). Ideal for regular compliance checks or large-scale infrastructure. |
| Red-Teaming | Adversary-emulation exercises with no scope restrictions. Used by governments and critical infrastructure to test resilience. |
| Static Application Security Testing (SAST) | Analyzes code for vulnerabilities (e.g., OWASP Top 10) without execution. Integrated into CI/CD pipelines. |

Future Trends and Innovations
The next frontier in cybersecurity testing is automation combined with AI. Tools like Darktrace’s Antigena use machine learning to detect anomalies in real time, while platforms like Burp Suite now incorporate generative AI to craft sophisticated attack payloads. However, automation risks creating a "false sense of security"—testers must still validate AI-generated findings manually.Another shift is toward continuous cybersecurity testing. Traditional annual audits are obsolete in cloud-native environments where assets scale dynamically. Solutions like Prisma Cloud and Aqua Security embed testing into DevOps workflows, ensuring vulnerabilities are caught before deployment. Meanwhile, quantum computing poses a long-term threat: post-quantum cryptography testing will soon become essential to future-proof encryption.
Conclusion
Cybersecurity testing is no longer optional—it’s the difference between a secure organization and one that’s merely hoping for the best. The landscape demands agility: threats evolve daily, and static defenses fail. The most effective programs blend automated efficiency with human ingenuity, balancing speed with depth.For leaders, the message is clear: invest in cybersecurity testing as a core function, not an IT project. Prioritize red-teaming over compliance checkboxes, and treat vulnerabilities as strategic risks—not just technical debts. The cost of inaction is measured in breaches, not budgets.
Comprehensive FAQs
Q: How often should cybersecurity testing be conducted?
A: Frequency depends on risk exposure. Critical systems (e.g., payment processors) require quarterly penetration tests, while less sensitive environments may suffice with biannual scans. Regulatory standards (e.g., PCI DSS) often mandate annual testing, but continuous monitoring is ideal for high-risk sectors.
Q: What’s the difference between a penetration test and a vulnerability scan?
A: Vulnerability scans identify known flaws (e.g., outdated software) via automated tools. Penetration tests actively exploit those flaws to assess real-world impact—like a hacker’s playbook. Scans are broad; tests are deep and targeted.
Q: Can AI replace human cybersecurity testers?
A: No. AI excels at pattern recognition (e.g., detecting brute-force attacks) but lacks contextual judgment. Ethical hackers interpret business risk, simulate social engineering, and think like adversaries—skills AI cannot replicate. The future lies in hybrid models where AI augments human expertise.
Q: How do I choose a cybersecurity testing provider?
A: Look for certifications (e.g., CREST, OSCP), experience in your industry, and a methodology aligned with your goals (e.g., NIST, MITRE ATT&CK). Avoid providers that promise "guaranteed" security—testing reveals flaws, not fixes. Demand detailed reports and remediation guidance.
Q: What are the most common mistakes in cybersecurity testing?
A: Over-reliance on automation (missing manual exploits), testing without business context (e.g., ignoring low-severity flaws that could escalate), and treating testing as a one-time event. Scope creep (e.g., skipping cloud environments) and poor communication between testers and stakeholders also undermine effectiveness.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.