Unlocking DNS Mastery: The Definitive Guide to BIND Configuration PDFs
Table of Contents
- The Complete Overview of DNS and BIND Configuration PDFs
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Where can I find official ISC documentation for BIND?
- Q: How do I troubleshoot a BIND server that’s not responding to queries?
- Q: Can BIND 9 handle IPv6-only networks?
- Q: What’s the difference between a master and slave zone in BIND?
- Q: How do I enable DNSSEC in BIND?
- Q: Are there performance benchmarks for tuning BIND’s cache?
The Domain Name System (DNS) remains the invisible backbone of the internet, translating human-readable domain names into machine-readable IP addresses with near-instantaneous precision. At its core, BIND (Berkeley Internet Name Domain)—the most widely deployed DNS software—operates as the authoritative interpreter of this system, yet its configuration often exists as an underexplored black box for administrators. While countless technical manuals and online tutorials cover BIND, few resources consolidate its foundational principles into a single, actionable dns and bind pdf reference that bridges theory with practical deployment.
The challenge lies in balancing BIND’s complexity with its necessity. A misconfigured DNS server can cripple a domain’s availability, while optimized settings can enhance performance by orders of magnitude. This gap is where dns and bind pdf guides become indispensable—not as static textbooks, but as dynamic tools that adapt to evolving threats, scalability demands, and emerging protocols. Whether you’re troubleshooting recursive resolution delays or securing a zone against cache poisoning, the right BIND configuration PDF serves as both a troubleshooting manual and a strategic blueprint.
For system architects and DevOps engineers, the stakes are higher than ever. With the rise of DNS-over-HTTPS (DoH) and encrypted DNS queries, traditional dns and bind pdf resources must evolve to address modern security paradigms. Meanwhile, legacy systems still rely on BIND’s time-tested reliability, making cross-version compatibility a critical consideration. The following analysis dissects BIND’s inner workings, its historical significance, and how dns and bind pdf documentation can transform administrative workflows—from initial setup to advanced optimization.

The Complete Overview of DNS and BIND Configuration PDFs
The term "dns and bind pdf" encompasses more than just configuration files—it represents a synthesis of DNS theory, BIND’s implementation quirks, and real-world deployment strategies. At its heart, BIND (named after its origins at the University of California, Berkeley) is a suite of tools that implements the DNS protocol stack, including recursive resolvers, authoritative servers, and caching mechanisms. While modern alternatives like PowerDNS or Windows Server DNS exist, BIND’s dominance—powering over 50% of the internet’s authoritative name servers—stems from its open-source flexibility, extensive feature set, and backward compatibility.A well-structured BIND configuration PDF acts as a bridge between theoretical DNS standards (RFCs 1034–1035, 2181, 8499) and practical deployment. It typically includes:
The absence of such a resource often forces administrators to piece together fragmented documentation, leading to inefficiencies. A comprehensive dns and bind pdf should also address edge cases—such as handling IPv6 transitions or integrating with modern CDNs—while remaining accessible to both beginners and seasoned sysadmins.
Historical Background and Evolution
BIND’s origins trace back to 1983, when Paul Vixie and others at Berkeley developed it as a replacement for the original DNS implementation (4.3BSD Net-2). Early versions of BIND (pre-4.9) were monolithic, with limited support for modern features like dynamic updates or DNSSEC. The transition to BIND 8 in 1999 marked a turning point, introducing modular design and IPv6 compatibility, though its rigid architecture led to performance bottlenecks.The release of BIND 9 in 2000 revolutionized DNS administration by adopting a view-based system (supporting multiple configurations per instance) and native DNSSEC integration. This version also standardized the dns and bind pdf documentation format, with ISC (Internet Systems Consortium) publishing official guides that became industry benchmarks. Modern BIND (versions 9.16+) reflects this evolution, offering features like:
Historically, dns and bind pdf resources have mirrored these milestones. Early guides focused on static zone files and basic recursion, while contemporary PDFs emphasize security (e.g., mitigating Kaminsky attacks via `dnssec-lookaside`) and hybrid cloud deployments.
Core Mechanisms: How It Works
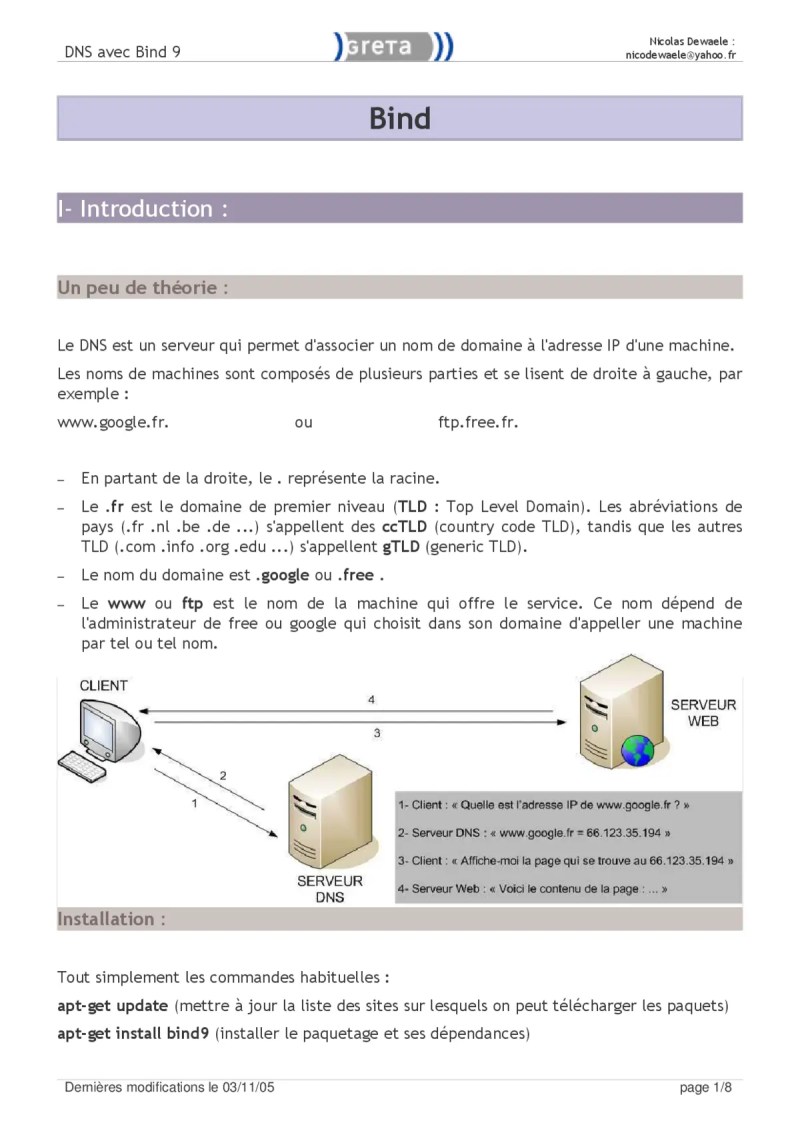
Under the hood, BIND operates as a stateful DNS server that processes queries through a pipeline of modules: resolver, cache, zone loader, and response generator. When a client queries `example.com`, BIND follows this workflow:1. Query Reception: The resolver checks its cache. If absent, it initiates a recursive lookup (unless configured as authoritative-only).
2. Zone Resolution: For authoritative servers, BIND loads the zone file (e.g., `example.com.zone`) and validates records against serial numbers.
3. Response Construction: Responses include SOA (Start of Authority) records, TTLs, and optional EDNS extensions (e.g., DNSSEC signatures).
A critical aspect often overlooked in dns and bind pdf guides is BIND’s named.conf hierarchy:
Misconfigurations here—such as incorrect `allow-query` ACLs or misaligned TTLs—can trigger cascading failures. Advanced BIND configuration PDFs dedicate sections to debugging these layers using tools like `named-checkconf` and `dig +trace`.
Key Benefits and Crucial Impact
The adoption of dns and bind pdf resources isn’t merely about troubleshooting; it’s a strategic investment in network reliability. For enterprises, a single misconfigured DNS server can propagate latency across global applications, while for ISPs, BIND’s caching efficiency directly impacts user experience. The open-source nature of BIND further reduces licensing costs, making it a cornerstone of cost-effective infrastructure.Beyond performance, dns and bind pdf guides address critical security vectors. For instance:
"DNS is the internet’s phone book, and BIND is the librarian—without it, the system collapses into chaos. A well-documented BIND configuration PDF isn’t just a manual; it’s a firewall against operational blind spots." — Paul Vixie, ISC Founder
Major Advantages
- Unified Documentation: Consolidates scattered RFCs, ISC manuals, and community wiki entries into a single dns and bind pdf reference, reducing context-switching.
- Version-Specific Guidance: Clarifies differences between BIND 9.11 (legacy) and 9.18 (modern), including deprecated directives (e.g., `allow-transfer` → `transfer`).
- Security Checklists: Provides pre-flight audits for DNSSEC, RPZ, and query logging, aligning with NIST SP 800-81 guidelines.
- Performance Benchmarks: Includes real-world examples of tuning `max-cache-size` or enabling `dnssec-validation auto`.
- Integration Templates: Offers YAML/JSON snippets for automating BIND deployments via Ansible or Terraform, bridging the gap between configuration files and IaC tools.
Comparative Analysis
| Feature | BIND (ISC) | PowerDNS | Windows DNS Server |
|---|---|---|---|
| Open-Source License | ISC License (permissive) | GPLv2 (with commercial options) | Proprietary (Windows Server) |
| DNSSEC Support | Native (since BIND 9) | Optional (via Lua scripts) | Limited (requires third-party tools) |
| Dynamic Updates | Full (TSIG, incremental zones) | Partial (requires API calls) | Basic (via DHCP integration) |
| Query Logging | Flexible (`query-log`, `syslog`) | Customizable (via Lua) | Basic (Event Viewer) |
Future Trends and Innovations
The next frontier for dns and bind pdf documentation lies in addressing privacy-preserving DNS and AI-driven resolution. With DoH adoption rising (e.g., Cloudflare’s 1.1.1.1), future BIND configuration PDFs must include:Additionally, BIND’s role in edge computing will grow as organizations deploy DNS servers closer to users. dns and bind pdf guides will need to cover:
Conclusion
The relationship between dns and bind pdf resources and modern network operations is symbiotic: as DNS protocols evolve, so too must the documentation that supports them. Whether you’re migrating from BIND 9.10 to 9.18 or implementing DNSSEC for the first time, a well-curated BIND configuration PDF serves as both a safety net and a performance multiplier.For administrators, the key takeaway is to treat dns and bind pdf guides not as static references but as living documents—updated alongside BIND’s release notes and RFC amendments. The internet’s reliability depends on it.
Comprehensive FAQs
Q: Where can I find official ISC documentation for BIND?
A: The ISC BIND documentation includes the BIND 9 Administrator Reference Manual, available as a downloadable PDF. For version-specific guides, check the doc/ directory in BIND’s source tarball or the ISC FTP archive.
Q: How do I troubleshoot a BIND server that’s not responding to queries?
A: Start with these steps:
- Verify BIND is running:
systemctl status named(Linux) orsc query named(Windows). - Check logs:
journalctl -u named(Linux) orEvent Viewer → Windows Logs → Application. - Test zone loading:
named-checkzone example.com db.example.com. - Inspect
named.conffor syntax errors:named-checkconf. - Use
dig @localhost example.comto test locally.
Q: Can BIND 9 handle IPv6-only networks?
A: Yes, but requires explicit configuration. In named.conf, ensure:
options {

    listen-on-v6 { any; };

    listen-on { none; }; // Disable IPv4

};
dig +short example.com AAAA. For hybrid setups, use listen-on { any; }; listen-on-v6 { any; };.
Q: What’s the difference between a master and slave zone in BIND?
A: A master zone is the primary source of truth, stored in a local file (e.g., db.example.com). A slave zone replicates data via NOTIFY messages from the master. Configure slaves in named.conf:
zone "example.com" {

    type slave;

    file "slaves/example.com.zone";

    masters { 192.0.2.1; };

};
slaves/ directory and proper allow-transfer ACLs on the master.
Q: How do I enable DNSSEC in BIND?
A: DNSSEC requires three steps:
- Generate keys:
dnssec-keygen -a RSASHA256 -b 2048 -n ZONE example.com(createsKexample.com.+001+28020.keyand.signed). - Sign the zone:
dnssec-signzone -o example.com -3 example.com db.example.com Kexample.com.+001+28020.key. - Update
named.conf:zone "example.com" {
type master;
file "db.example.com.signed";
inline-signing yes;
};
options { dnssec-enable yes; dnssec-validation yes; };
dnssec-verify -v db.example.com.signed. For public zones, publish DS records to the parent zone.
Q: Are there performance benchmarks for tuning BIND’s cache?
A: Yes. Key parameters in named.conf include:
options {

    max-cache-size 2G;       // Default: 512MB

    max-cache-ttl 1h;        // Override TTLs for caching

    min-cache-ttl 30m;       // Prevents excessive cache churn

    recursion no;           // Disable if authoritative-only

};
named -g -d 1 (foreground mode) and tools like dnsperf. For high-traffic resolvers, monitor rndc stats to adjust max-recursion-depth.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.