How to Generate a Random Number in Java: Deep Dive into Methods, Use Cases, and Performance
Table of Contents
- The Complete Overview of Getting a Random Number in Java
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I use `Math.random()` for cryptographic purposes?
- Q: Why is `ThreadLocalRandom` faster than `Random`?
- Q: How do I generate a random integer in a specific range?
- Q: What’s the difference between `SecureRandom.getInstanceStrong()` and default `SecureRandom`?
- Q: How can I ensure reproducibility in tests using randomness?
- Q: Are there performance penalties for using `SecureRandom` in high-frequency loops?
- Q: Can I implement my own PRNG in Java?
Java’s built-in tools for getting a random number in Java are foundational for simulations, cryptography, and game development. Unlike pseudorandom number generators (PRNGs) in other languages, Java offers a spectrum of approaches—from lightweight utility methods to cryptographically secure algorithms. The choice often hinges on whether you need speed, reproducibility, or security. For instance, a game might prioritize performance, while a blockchain application demands unpredictability. Even simple tasks like shuffling a deck of cards or generating test data rely on these mechanisms, yet most developers overlook the nuances between `Math.random()` and `SecureRandom`.
The Java platform’s randomness capabilities have evolved alongside its core libraries. Early versions relied on `Math.random()`, a quick but limited solution, while modern applications demand stronger guarantees. Today, the `Random` class and its successors—like `ThreadLocalRandom` and `SecureRandom`—address scalability and security concerns. Understanding these distinctions isn’t just academic; it directly impacts thread safety, predictability, and even legal compliance in fields like gambling or encryption.
The Complete Overview of Getting a Random Number in Java
Java’s approach to random number generation is layered, reflecting its dual role as a general-purpose and enterprise-grade language. At its core, the platform provides three primary pathways: the static `Math.random()` method, the `Random` class (and its thread-local variant), and cryptographic-grade generators via `SecureRandom`. Each serves distinct use cases, from lightweight simulations to high-stakes security applications. The trade-offs—speed versus security, reproducibility versus entropy—are rarely discussed in beginner tutorials, yet they define the reliability of systems built on these primitives.For developers working with getting a random number in Java, the choice of method isn’t just about syntax but about the implications of seeding, periodicity, and thread safety. For example, `Math.random()` uses a 48-bit seed derived from `System.nanoTime()`, making it unsuitable for cryptographic purposes but adequate for unit tests or algorithmic challenges. Meanwhile, `SecureRandom` leverages platform-specific entropy sources (e.g., `/dev/urandom` on Linux), ensuring compliance with standards like FIPS 140-2. The distinction matters: a poorly seeded PRNG can expose vulnerabilities in password systems or financial simulations.
Historical Background and Evolution
The origins of Java’s randomness tools trace back to the language’s design philosophy: simplicity for developers, robustness for deployments. The `Math.random()` method, introduced in Java 1.0 (1996), was a direct port from C’s `rand()`, using a linear congruential generator (LCG) with a modest 48-bit state. While adequate for early applets and basic simulations, its predictability made it ill-suited for security-sensitive applications. By Java 1.1, the `Random` class emerged, offering a more flexible API with customizable seeds and better statistical properties—though still not cryptographically secure.The turning point came with Java 1.2 (1998), when `SecureRandom` was introduced to address cryptographic needs. Backed by the Java Cryptography Architecture (JCA), it integrated with operating system entropy pools, providing true randomness for key generation and digital signatures. Subsequent versions refined these tools: Java 7’s `ThreadLocalRandom` optimized multi-threaded performance by eliminating synchronization overhead, while Java 8 added support for algorithm-specific backends (e.g., SHA1PRNG, NativePRNG). This evolution mirrors broader trends in computing, where randomness shifted from a convenience feature to a critical security primitive.
Core Mechanisms: How It Works
Under the hood, getting a random number in Java relies on mathematical algorithms and system interactions. The `Math.random()` method, for instance, uses an LCG with the formula:`(seed 0x5DEECE66DL + 0xBL) >>> 43`
This produces a double between `[0.0, 1.0)`, which can be scaled to other ranges. The seed is initialized via `System.nanoTime()`, but subsequent calls reuse the same seed unless explicitly reset—a design choice that simplifies debugging but limits use cases.
In contrast, the `Random` class employs a more sophisticated algorithm: a Mersenne Twister (MT19937) with a 19937-bit state, offering a period of ~2¹⁹⁹³⁷. This ensures longer sequences without repetition, critical for simulations like Monte Carlo methods. The `SecureRandom` class, however, bypasses algorithmic randomness entirely, instead querying OS-level entropy sources (e.g., hardware random number generators or `/dev/random`). This makes it suitable for cryptographic operations but slower due to I/O overhead.
Key Benefits and Crucial Impact
The ability to generate random numbers in Java underpins entire industries. In gaming, procedural content generation relies on PRNGs to create unique worlds; in finance, risk modeling uses randomness to simulate market volatility. Even everyday tasks—like password hashing or session token generation—depend on these mechanisms. The impact extends beyond functionality: poorly implemented randomness can lead to security flaws, such as predictable session IDs or exploitable game cheats.Java’s ecosystem addresses these needs with precision. For developers prioritizing performance, `ThreadLocalRandom` reduces contention in multi-threaded environments by avoiding shared state. For security-critical applications, `SecureRandom` provides auditability and compliance. The language’s design ensures that even novice programmers can generate randomness without introducing subtle bugs—yet advanced users can fine-tune generators for specific workloads.
"Randomness is the last refuge of the incompetent programmer." — Adapted from a quote by Donald Knuth, emphasizing that poor randomness design often stems from misunderstanding the underlying mechanisms.
Major Advantages
- Performance Optimization: `ThreadLocalRandom` in Java 7+ reduces lock contention, making it ideal for high-throughput systems like HFT (high-frequency trading) or real-time analytics.
- Cryptographic Security: `SecureRandom` meets NIST and FIPS standards, ensuring suitability for TLS handshakes, blockchain hashing, or password storage.
- Reproducibility: The `Random` class’s seedable nature allows deterministic testing, critical for debugging or regression testing in CI/CD pipelines.
- Algorithm Diversity: Java supports multiple PRNGs (e.g., `SplittableRandom` for parallel streams), enabling developers to choose based on statistical properties.
- Backward Compatibility: Legacy code relying on `Math.random()` continues to function, though with caveats about predictability.
Comparative Analysis
| Method | Use Case & Trade-offs |
|---|---|
Math.random() |
Lightweight, non-cryptographic. Fast but predictable; avoids thread safety issues. Suitable for unit tests, simple simulations. |
Random class |
High-quality PRNG (Mersenne Twister). Thread-safe but slower than `ThreadLocalRandom`. Best for general-purpose randomness where security isn’t critical. |
ThreadLocalRandom |
Optimized for multi-threaded apps. Faster than `Random` but lacks cryptographic guarantees. Ideal for parallel algorithms or high-frequency loops. |
SecureRandom |
Cryptographically secure. Slower due to entropy gathering. Required for passwords, tokens, or any security-sensitive operation. |
Future Trends and Innovations
The future of random number generation in Java is shaped by two forces: performance demands and security requirements. As quantum computing looms, cryptographic algorithms like `SecureRandom` may need post-quantum upgrades (e.g., lattice-based PRNGs). Meanwhile, hardware advancements—such as Intel’s RDSEED instruction—could further accelerate entropy collection, reducing `SecureRandom`’s I/O bottleneck.Java’s modularity suggests that future versions may introduce algorithm-specific `Random` subclasses (e.g., PCG or XorShift) via the `java.util.random` package, giving developers finer control. For now, the focus remains on balancing speed and security: `ThreadLocalRandom` for performance-critical paths, `SecureRandom` for security, and `Math.random()` only where simplicity outweighs risks.
Conclusion
Java’s tools for generating random numbers are a testament to the language’s adaptability, offering solutions for every scenario from trivial to critical. The key takeaway is context: `Math.random()` suffices for a script generating test data, but `SecureRandom` is non-negotiable for a payment system’s tokenization. Ignoring these distinctions can lead to vulnerabilities or inefficiencies—yet understanding them empowers developers to write robust, high-performance code.As Java continues to evolve, the interplay between randomness, security, and performance will remain a focal point. For now, the ecosystem provides everything needed to handle getting a random number in Java—whether for a simple game or a mission-critical application. The challenge lies in choosing wisely.
Comprehensive FAQs
Q: Can I use `Math.random()` for cryptographic purposes?
A: No. `Math.random()` is not cryptographically secure; it uses a predictable algorithm and a non-cryptographic seed. For security, always use `SecureRandom`. Even `Random` is insufficient—only `SecureRandom` meets NIST standards.
Q: Why is `ThreadLocalRandom` faster than `Random`?
A: `ThreadLocalRandom` eliminates synchronization overhead by maintaining a separate instance per thread. The `Random` class uses a single `AtomicLong` seed, which requires locks under contention, slowing down multi-threaded applications.
Q: How do I generate a random integer in a specific range?
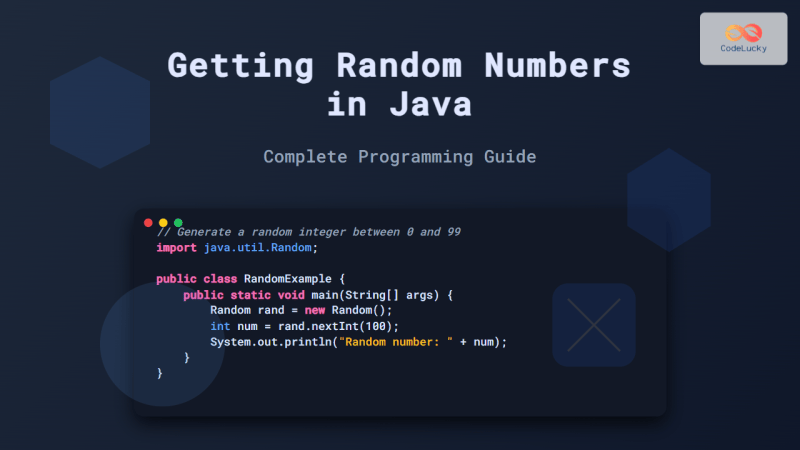
A: Use `nextInt(bound)` for `[0, bound)` or `nextInt(min, max + 1)` for `[min, max]`. Example:
```java
Random rand = new Random();
int num = rand.nextInt(100); // 0–99
int bounded = rand.nextInt(50, 101); // 50–100 (Java 17+)
```
For `Math.random()`, scale the result: `(int)(Math.random() range)`.
Q: What’s the difference between `SecureRandom.getInstanceStrong()` and default `SecureRandom`?
A: `getInstanceStrong()` selects an implementation with the highest available entropy source (e.g., hardware RNG). The default may fall back to a weaker algorithm if the OS doesn’t provide sufficient entropy. Use `getInstanceStrong()` for maximum security.
Q: How can I ensure reproducibility in tests using randomness?
A: Seed the `Random` instance with a fixed value:
```java
Random rand = new Random(42L); // Always produces the same sequence
```
For `SecureRandom`, avoid seeding—it’s designed to be unpredictable. Instead, mock it in tests or use a deterministic PRNG like `SplittableRandom` with a fixed seed.
Q: Are there performance penalties for using `SecureRandom` in high-frequency loops?
A: Yes. `SecureRandom` is I/O-bound when querying OS entropy sources. For performance-critical loops, use `ThreadLocalRandom` and only call `SecureRandom` for initialization (e.g., generating a single key). Alternatives like `SplittableRandom` offer a middle ground with better parallelism.
Q: Can I implement my own PRNG in Java?
A: Yes, but exercise caution. Java’s built-in generators are rigorously tested. Custom PRNGs must pass statistical tests (e.g., Dieharder) and avoid pitfalls like short periods or bias. For most cases, prefer existing implementations unless you have a specific requirement.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.