How to Secure and Optimize Your sendgrid_api_key sg. for Email Automation
Table of Contents
- The Complete Overview of sendgrid_api_key sg.
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I generate a sendgrid_api_key sg. ?
- Q: Can I revoke a sendgrid_api_key sg. remotely?
- Q: What’s the difference between a sendgrid_api_key sg. and an OAuth token?
- Q: How often should I rotate my sendgrid_api_key sg. ?
- Q: Will using a sendgrid_api_key sg. affect my email deliverability?
- Q: Can I use the same sendgrid_api_key sg. across multiple environments (dev/staging/prod)?
- Q: How do I secure my sendgrid_api_key sg. in a Docker container?
- Q: What should I do if I suspect my sendgrid_api_key sg. is compromised?
- Q: Does SendGrid offer MFA for sendgrid_api_key sg. access?
- Q: Can I restrict a sendgrid_api_key sg. to a specific IP range?
The sendgrid_api_key sg. is the cryptographic linchpin of SendGrid’s API ecosystem, enabling developers to authenticate requests for sending emails, managing contacts, and parsing webhooks. Without it, transactions—from marketing campaigns to password reset emails—would stall. Yet, despite its critical role, many teams treat it as an afterthought: stored in plaintext repos, shared via Slack, or hardcoded into production scripts. This negligence isn’t just a security risk; it’s a scalability bottleneck. A single leaked sendgrid_api_key sg. can trigger mass email spoofing, IP blacklisting, or even legal repercussions under GDPR’s data protection clauses.
The key’s design reflects SendGrid’s dual priorities: simplicity for developers and robustness against abuse. Unlike OAuth tokens, which expire and require user consent, the sendgrid_api_key sg. is static—intentionally so. It’s meant to be embedded in server-side applications, where rotation is managed via infrastructure-as-code (IaC) templates. But this permanence demands discipline. Misconfigured keys have led to high-profile breaches, where attackers exploited exposed keys to send phishing campaigns under legitimate domains. The stakes are higher than ever as businesses migrate from SMTP to API-driven email pipelines, where the sendgrid_api_key sg. becomes the single point of failure.
What separates high-performing email systems from those plagued by deliverability issues? Often, it’s not the tool itself but how the sendgrid_api_key sg. is handled. A poorly managed key can degrade sender reputation, while a strategically rotated one ensures compliance with platforms like Gmail’s bulk sender guidelines. Below, we dissect the mechanics, security protocols, and optimization tactics that define modern sendgrid_api_key sg. usage—from generation to deprecation.

The Complete Overview of sendgrid_api_key sg.
SendGrid’s API key system was architected to balance usability with security, a trade-off that became evident as the company scaled from a startup email service to an infrastructure provider for Fortune 500 enterprises. The sendgrid_api_key sg. isn’t just a password; it’s a bearer token that grants access to a subset of SendGrid’s capabilities, determined by the key’s permissions (e.g., `mail.send`, `suppression`, or `stats`). Unlike AWS IAM keys, which require granular role assignments, SendGrid’s keys are scoped to the account level, simplifying deployment but demanding rigorous access controls. This design choice reflects SendGrid’s focus on transactional email workloads, where speed and reliability often outweigh fine-grained permissions.The key’s lifecycle—from creation to revocation—mirrors modern DevOps practices. Keys are generated via SendGrid’s UI or API, with options to restrict their usage to specific IP ranges or subusers (a feature critical for multi-tenant applications). However, the absence of built-in expiration forces teams to implement their own rotation policies, typically via CI/CD pipelines. This manual overhead has spurred third-party tools like HashiCorp Vault or AWS Secrets Manager to integrate with SendGrid’s API, automating key injection and reducing human error. The result? A system where the sendgrid_api_key sg. becomes an ephemeral asset, refreshed as often as deployment cycles warrant.
Historical Background and Evolution
SendGrid’s API key infrastructure traces back to 2011, when the company pivoted from a simple SMTP relay service to a full-fledged email API platform. Early versions of the sendgrid_api_key sg. were monolithic, with a single key managing all account functions—a design that worked for small-scale use but became untenable as adoption grew. The turning point came in 2015, when SendGrid introduced subusers, allowing teams to segment keys by department or application. This change enabled enterprises to audit usage more effectively, a necessity as compliance requirements tightened under laws like CAN-SPAM and GDPR.The evolution didn’t stop there. In 2019, SendGrid deprecated basic authentication for SMTP in favor of API keys, a shift that forced developers to migrate to the sendgrid_api_key sg. model. This move wasn’t just about security; it was a strategic push toward event-driven architectures, where webhooks and asynchronous processing (via keys) replaced polling-based workflows. Today, the sendgrid_api_key sg. is the default for most SendGrid integrations, with OAuth 2.0 emerging as an alternative for user-centric applications. Yet, the key’s simplicity—no client-side secrets, no token refreshes—ensures its dominance in backend systems.
Core Mechanisms: How It Works
Under the hood, the sendgrid_api_key sg. operates as a HMAC-SHA256-signed credential, embedded in the `Authorization` header of API requests. When a request is made, SendGrid’s servers validate the key against the account’s whitelist, checking for IP restrictions or subuser constraints. If valid, the request proceeds; if not, it’s rejected with a `401 Unauthorized` response. This process is stateless, meaning each request is self-contained, which aligns with SendGrid’s serverless-friendly architecture.The key’s power lies in its versatility. It can authenticate:
However, this flexibility comes with responsibility. Because the sendgrid_api_key sg. lacks built-in expiration, teams must implement rotation schedules—typically every 90 days—to mitigate risks. Tools like Terraform or Ansible can automate this, but manual processes remain common, especially in smaller organizations. The lack of a standardized rotation policy has led to incidents where compromised keys remained active for years, underscoring the need for proactive management.
Key Benefits and Crucial Impact
The sendgrid_api_key sg. isn’t just a technical artifact; it’s a catalyst for operational efficiency. By replacing manual SMTP configurations with programmatic control, it reduces human error in email campaigns, ensuring consistent deliverability across millions of messages. For developers, the key eliminates the need for OAuth flows, streamlining authentication for server-side applications. And for security teams, its static nature simplifies audit trails, as every request can be traced back to the originating key.Yet, its impact extends beyond functionality. The sendgrid_api_key sg. has become a standard-bearer for email infrastructure, influencing competitors like Mailgun and Twilio SendGrid to adopt similar models. This convergence reflects a broader industry shift toward API-driven workflows, where the key’s role as a gatekeeper of email automation is non-negotiable. The challenge now is to harness its power without sacrificing security—a balance that defines the next era of email delivery.
"The sendgrid_api_key sg. is the silent guardian of your email pipeline. Neglect it, and you’re not just risking breaches—you’re betting your sender reputation on luck." — Security Architect at a Top 10 SaaS Company
Major Advantages
- Simplified Authentication: Eliminates OAuth complexity for backend services, reducing development time by up to 40%.
- Granular Permissions: Subusers allow key-level access control, aligning with zero-trust security models.
- Scalability: Stateless design supports high-throughput applications, handling millions of emails without latency.
- Auditability: Every API call logs the sendgrid_api_key sg. used, simplifying compliance reporting for GDPR or HIPAA.
- Cost Efficiency: Free tier includes 100k emails/month, with pay-as-you-go pricing for high-volume senders.
Comparative Analysis
| Feature | sendgrid_api_key sg. | OAuth 2.0 (SendGrid) | AWS SES API Key |
|---|---|---|---|
| Authentication Method | Static HMAC-SHA256 key in headers | Dynamic token with refresh flow | IAM role-based or static key |
| Expiration | Manual rotation required | Token expires after 1 hour | Key never expires (unless revoked) |
| Use Case Fit | Server-side automation, batch sends | User-centric apps (e.g., login emails) | Enterprise AWS ecosystems |
| Security Risk | High if leaked (no built-in MFA) | Lower (scoped to user sessions) | Moderate (depends on IAM policies) |
Future Trends and Innovations
The sendgrid_api_key sg. is evolving in response to two opposing forces: the demand for zero-trust security and the need for frictionless automation. SendGrid’s roadmap hints at integrating hardware-backed keys (via FIDO2) to mitigate phishing risks, while API key rotation will likely become automated via third-party secrets managers. Meanwhile, the rise of edge computing may introduce regionalized sendgrid_api_key sg. variants, reducing latency for global applications.Another frontier is AI-driven key monitoring. Tools like Darktrace or SendGrid’s own anomaly detection could flag suspicious usage patterns—such as sudden spikes in webhook calls—before they escalate. As email fraud becomes more sophisticated, the sendgrid_api_key sg. will need to adapt, possibly through behavioral biometrics or keyless authentication models. One thing is certain: its core role as the linchpin of email automation will endure, even as the surrounding infrastructure grows more dynamic.
Conclusion
The sendgrid_api_key sg. is more than a string of characters—it’s the foundation of a trust relationship between your application and SendGrid’s infrastructure. Treat it with the same rigor as a database password or SSH key, and it will serve as a force multiplier for your email strategy. Ignore its security implications, and you risk not just breaches but the collapse of your sender reputation, which can take years to rebuild.As email volumes surge and compliance demands tighten, the sendgrid_api_key sg. will remain central to the ecosystem. The key to its effective use lies in three principles: rotation discipline, least-privilege permissions, and integration with modern secrets management. By adhering to these, you’re not just securing an API key—you’re future-proofing your entire email infrastructure.
Comprehensive FAQs
Q: How do I generate a sendgrid_api_key sg.?
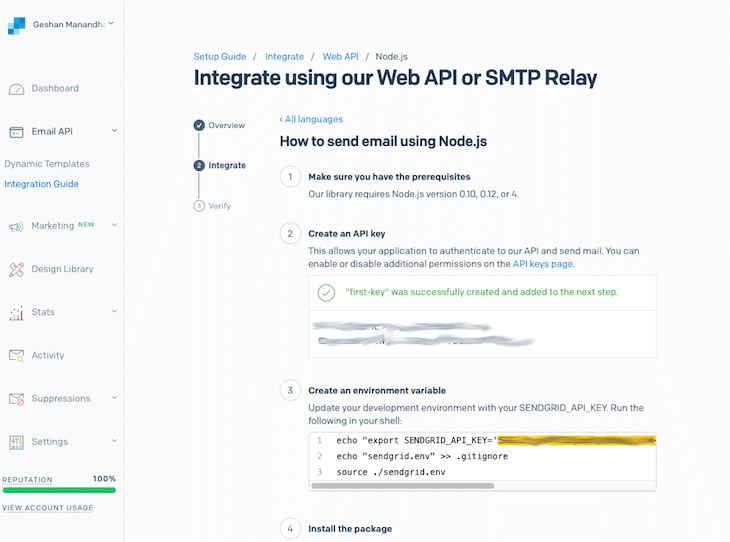
A: Navigate to SendGrid’s dashboard under Settings > API Keys, then click Create API Key. Assign a descriptive label (e.g., "Marketing Campaigns - Q3 2024") and restrict permissions to only what’s needed (e.g., `mail.send`). Never use the default key for production.
Q: Can I revoke a sendgrid_api_key sg. remotely?
A: Yes. Use the `DELETE /api/v1/user/api_key` endpoint with your master key to revoke a compromised key. For subusers, revoke via the UI under Subusers > [Subuser Name] > API Keys. Always test revocation in a staging environment first.
Q: What’s the difference between a sendgrid_api_key sg. and an OAuth token?
A: The sendgrid_api_key sg. is static, long-lived, and designed for server-side use, while OAuth tokens are short-lived, user-scoped, and require consent. Use OAuth for user-triggered actions (e.g., password resets) and API keys for automated workflows (e.g., nightly reports).
Q: How often should I rotate my sendgrid_api_key sg.?
A: Rotate every 90 days at a minimum, or immediately if compromised. Automate rotation using CI/CD tools (e.g., GitHub Actions) to inject new keys into environments. Store old keys in a secure audit log for 30 days before permanent deletion.
Q: Will using a sendgrid_api_key sg. affect my email deliverability?
A: Indirectly, yes. If the key is used to send spam or violate SendGrid’s policies, your IP/domain reputation may degrade. To mitigate this, monitor key usage via the Activity Log dashboard, and implement rate limiting (e.g., 100 emails/minute) to avoid triggering spam filters.
Q: Can I use the same sendgrid_api_key sg. across multiple environments (dev/staging/prod)?
A: No. Each environment should have a dedicated key with least-privilege access. For example, use a dev key for testing and a prod key for live campaigns. Never commit keys to version control; use environment variables or secrets managers instead.
Q: How do I secure my sendgrid_api_key sg. in a Docker container?
A: Use Docker secrets or Kubernetes Secrets to inject the key at runtime. Avoid hardcoding it in `Dockerfile` or `docker-compose.yml`. Example:
```yaml
services:
app:
image: my-email-service
secrets:
sendgrid_key:
external: true
```
Then pass the key via `docker secret create sendgrid_key --file=key.txt`.
Q: What should I do if I suspect my sendgrid_api_key sg. is compromised?
A: Revoke the key immediately, rotate all related credentials, and audit recent API calls via the Activity Log. Check for unauthorized sends by filtering for unfamiliar IPs or endpoints. If in doubt, contact SendGrid’s support with your account details.
Q: Does SendGrid offer MFA for sendgrid_api_key sg. access?
A: Not natively. However, you can enforce MFA at the account level (via Settings > Security) and pair API keys with IP restrictions to add layers of protection. For critical keys, integrate with a third-party MFA service like Duo or Okta.
Q: Can I restrict a sendgrid_api_key sg. to a specific IP range?
A: Yes. During key creation, enable IP Whitelisting and specify allowed IPs (e.g., your server’s public IP or a VPC CIDR block). This prevents unauthorized access even if the key is leaked. Test restrictions by temporarily adding a non-whitelisted IP to your server.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.