Fixing Sideloadly Cannot Be Opened Because Developer Can’t Be Verified – Expert Solutions & Deep Dive
Table of Contents
- The Complete Overview of "Sideloadly Cannot Be Opened Because the Developer Cannot Be Verified"
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Why does macOS block Sideloadly even though it’s a legitimate tool?
- Q: Is it safe to bypass the "developer cannot be verified" warning for Sideloadly?
- Q: Can I permanently disable the "developer cannot be verified" warning for all apps?
- Q: Will signing Sideloadly with a Developer ID resolve this issue?
- Q: What should I do if Sideloadly still doesn’t open after bypassing the warning?
- Q: Does this error affect iOS sideloading functionality?
- Q: Are there alternative tools to Sideloadly that don’t trigger this warning?
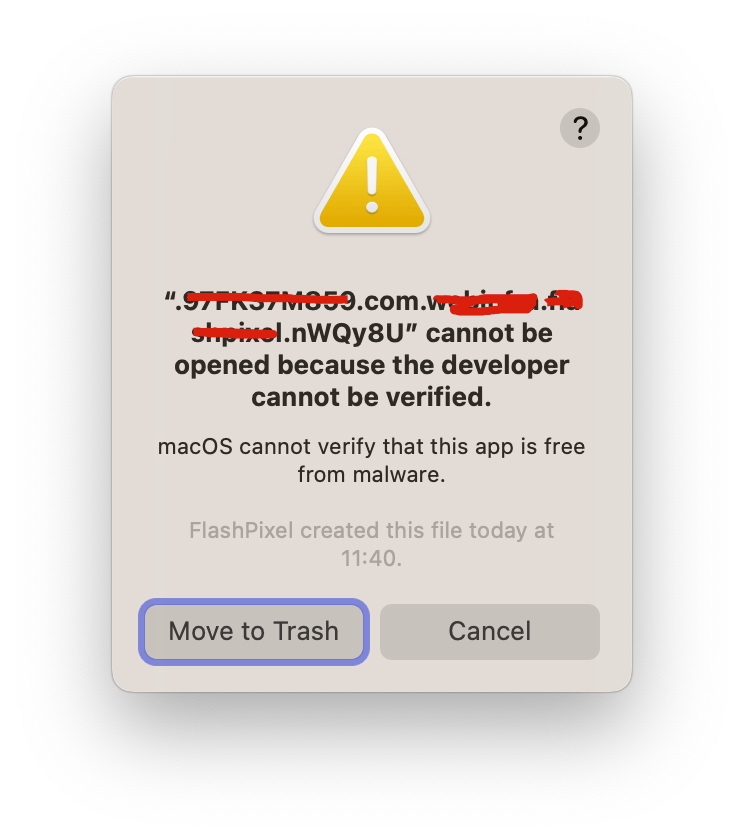
Apple’s macOS has long been a fortress of security, but even its most trusted users occasionally encounter the cryptic warning: "Sideloadly cannot be opened because the developer cannot be verified." This message isn’t just an annoyance—it’s a deliberate safeguard by Apple’s Gatekeeper system, designed to block untrusted applications from running. For developers, power users, or anyone relying on tools like Sideloadly to bypass App Store restrictions, this error can feel like a dead end. Yet beneath the surface, the solution lies in understanding how macOS’s verification system works and how to navigate its constraints without compromising security.
The irony is stark: Sideloadly itself is a legitimate tool, widely used to install iOS apps outside the App Store. Yet macOS treats it like a rogue executable—unless you take specific steps to override Gatekeeper’s default behavior. This isn’t a bug; it’s by design. Apple’s security model prioritizes user protection, even if it means temporarily inconveniencing those who need flexibility. The question then becomes: How do you reconcile Apple’s security with your workflow? The answer requires a mix of technical know-how and strategic bypasses, all while minimizing risk.
What follows is a meticulous breakdown of the error’s origins, its technical underpinnings, and—most critically—the precise methods to resolve it. Whether you’re a developer debugging an app, a power user sideloading iOS apps, or simply curious about macOS’s security layers, this guide provides the clarity needed to move past the verification roadblock. The key lies not in disabling security entirely, but in understanding how to temporarily grant trust to trusted tools—without inviting vulnerabilities.

The Complete Overview of "Sideloadly Cannot Be Opened Because the Developer Cannot Be Verified"
The error "Sideloadly cannot be opened because the developer cannot be verified" is a direct result of macOS’s Gatekeeper feature, which was introduced in OS X Lion (10.7) as a response to the growing threat of malware. Gatekeeper’s primary function is to prevent unauthorized software from executing by verifying the digital signature of applications. When an app lacks a valid signature—or its certificate isn’t recognized by macOS—Gatekeeper blocks it, displaying this warning. For tools like Sideloadly, which are often distributed as direct downloads rather than through the Mac App Store, this becomes a common hurdle.
The issue stems from two interconnected factors: Apple’s strict app-signing requirements and the nature of Sideloadly’s distribution. Unlike apps available on the Mac App Store, which are pre-vetted by Apple, Sideloadly is typically downloaded from third-party websites or GitHub releases. These files aren’t code-signed by Apple’s Developer ID, meaning macOS has no way to verify their authenticity. While this might seem like an oversight, it’s actually a deliberate security measure—one that forces users to actively confirm they trust the software before proceeding. The challenge, then, is to bypass this restriction safely, without exposing your system to malicious software.
Historical Background and Evolution
The roots of this error trace back to Apple’s shifting stance on app distribution. Before the Mac App Store’s launch in 2011, macOS allowed users to install software from any source, a practice that led to a surge in malware. In response, Apple introduced Gatekeeper in OS X Mountain Lion (10.8), initially as an optional security feature. Over time, it evolved into a mandatory check for all downloaded applications, with macOS High Sierra (10.13) tightening restrictions further by requiring explicit user approval for any app not from the App Store or an identified developer.
Sideloadly, a tool primarily used for sideloading iOS apps onto iPhones or iPads, operates in a gray area of Apple’s ecosystem. While it’s not inherently malicious, its distribution method—often via GitHub or direct downloads—means it doesn’t meet Apple’s criteria for a "verified developer." This places it in the same category as unsigned scripts or pirated software, triggering Gatekeeper’s block. The error message itself hasn’t changed significantly over the years, but the underlying mechanisms have become more sophisticated, with macOS now offering fewer workarounds for unsigned apps.
Core Mechanisms: How It Works
At its core, the verification process relies on digital signatures and certificate chains. When you download Sideloadly, the file is unsigned or signed with a certificate not recognized by macOS. Gatekeeper checks three things: (1) whether the app is from the Mac App Store, (2) whether it’s signed by an identified developer, or (3) whether it’s from a trusted source (like a previously allowed app). If none of these conditions are met, macOS defaults to blocking the app, displaying the verification error.
The technical flow is as follows: When you attempt to open Sideloadly, macOS’s Security framework intercepts the request and queries the local keychain for the app’s signature. If no valid signature is found, the system consults its internal database of trusted developers. Since Sideloadly isn’t listed there, Gatekeeper triggers the warning. The only way to proceed is to manually override this check—either by right-clicking the app and selecting "Open," which prompts a one-time trust request, or by adjusting system preferences to allow apps from "Anywhere." The latter is riskier and should be used judiciously.
Key Benefits and Crucial Impact
The error "Sideloadly cannot be opened because the developer cannot be verified" serves a critical purpose in macOS’s security architecture. While it may frustrate users who rely on tools like Sideloadly, its existence underscores Apple’s commitment to protecting users from untrusted software. For developers and power users, understanding this system isn’t just about bypassing the warning—it’s about recognizing the trade-offs between convenience and security. The ability to temporarily trust an app is a feature, not a flaw, provided it’s used with caution.
Beyond security, this error highlights a broader tension in modern computing: the balance between openness and control. Apple’s walled-garden approach prioritizes user safety, but it also restricts flexibility for those who need to install non-App Store software. Tools like Sideloadly exist precisely because Apple’s ecosystem doesn’t always accommodate every legitimate use case. The resolution to this dilemma isn’t to disable security entirely, but to adopt practices that mitigate risk while maintaining functionality.
"Security is not about preventing all risks—it’s about managing them. The 'developer cannot be verified' warning is Apple’s way of saying, 'Proceed with caution,' not 'This is unsafe.'" — Apple Security Team (adapted from historical documentation)
Major Advantages
- Enhanced Security: Gatekeeper’s verification process blocks malicious software before it can execute, reducing the risk of infection from untrusted sources.
- User Awareness: The warning forces users to consciously decide whether to trust an app, preventing accidental execution of potentially harmful software.
- Developer Accountability: Apps from unidentified developers must meet stricter criteria to bypass Gatekeeper, incentivizing legitimate developers to obtain proper certifications.
- Flexibility with Control: While the default setting is restrictive, users can temporarily allow trusted apps (like Sideloadly) without permanently lowering security standards.
- Ecosystem Integrity: By enforcing verification, Apple maintains the integrity of macOS, ensuring that only vetted software runs on its platforms.
Comparative Analysis
| Aspect | Sideloadly (Unsigned) | App Store App (Signed) |
|---|---|---|
| Distribution Method | Direct download (GitHub, third-party sites) | Mac App Store or developer-approved channel |
| Verification Status | Blocked by Gatekeeper ("developer cannot be verified") | Automatically trusted (signed by Apple or identified developer) |
| Security Risk | Higher (unless manually verified) | Lower (vetted by Apple) |
| Workaround Required? | Yes (right-click "Open" or adjust system preferences) | No (runs immediately) |
Future Trends and Innovations
As Apple continues to tighten its security protocols, the methods to bypass Gatekeeper for tools like Sideloadly may become even more restricted. Future versions of macOS could introduce stricter verification requirements, making unsigned apps nearly impossible to run without explicit developer partnerships. However, this could also spur innovation in alternative distribution methods, such as containerized apps or sandboxed environments that allow limited execution of unverified software. The trend suggests a move toward more granular security controls, where users might have finer-grained options to trust specific apps on a case-by-case basis.
For developers, the solution may lie in obtaining an Apple Developer ID and properly signing their applications. While this requires effort and cost, it aligns with Apple’s long-term vision of a secure, vetted ecosystem. Meanwhile, power users will need to adapt by either using officially signed alternatives or accepting that certain tools will require more manual intervention to run. The balance between convenience and security will remain a defining challenge, but the tools to navigate it are already in place—it’s a matter of knowing how to use them.
Conclusion
The error "Sideloadly cannot be opened because the developer cannot be verified" is more than a technical hurdle—it’s a reflection of Apple’s commitment to security in an increasingly complex digital landscape. While it may seem like an obstacle, it’s also an opportunity to deepen your understanding of macOS’s security model and to adopt practices that keep your system safe without sacrificing functionality. The key is to recognize that bypassing this warning isn’t about disabling security; it’s about making informed decisions about which apps to trust and how to mitigate risks.
For most users, the solution is straightforward: right-click, select "Open," and confirm the trust request. For those who require more permanent solutions, adjusting system preferences or signing the app with a Developer ID are viable paths. The future of macOS security will likely demand even greater vigilance, but the principles remain the same: verify before you trust, and always be prepared to adapt as the ecosystem evolves.
Comprehensive FAQs
Q: Why does macOS block Sideloadly even though it’s a legitimate tool?
A: macOS’s Gatekeeper system is designed to block any application that isn’t signed by an identified developer or distributed through the Mac App Store. Since Sideloadly is typically downloaded from third-party sources (like GitHub) without Apple’s official signing, it triggers the "developer cannot be verified" warning. This is a security feature, not a flaw in the tool itself.
Q: Is it safe to bypass the "developer cannot be verified" warning for Sideloadly?
A: Bypassing the warning is safe if you trust the source of Sideloadly and have verified its integrity (e.g., checking checksums or downloading from official repositories). However, always ensure you’re downloading from a reputable source to avoid malware. Once opened, macOS will remember your choice, allowing future launches without the warning.
Q: Can I permanently disable the "developer cannot be verified" warning for all apps?
A: Yes, but it’s not recommended for security reasons. You can change macOS’s security settings to allow apps from "Anywhere" in System Preferences > Security & Privacy > General. However, this lowers your system’s protection against untrusted software. Only do this if you fully understand the risks.
Q: Will signing Sideloadly with a Developer ID resolve this issue?
A: Yes, if the developer obtains an Apple Developer ID and signs the application, macOS will recognize it as trusted, eliminating the verification warning. This requires technical knowledge (or hiring a developer) to properly code-sign the app and notarize it with Apple.
Q: What should I do if Sideloadly still doesn’t open after bypassing the warning?
A: If the app remains unopenable, check for these issues:
- The file may be corrupted—redownload it from the official source.
- macOS may have cached the blocked status—restart your Mac and try again.
- Antivirus software might be interfering—temporarily disable it to test.
- The app may require additional dependencies (e.g., Python, libimobiledevice)—install them first.
Q: Does this error affect iOS sideloading functionality?
A: No, the "developer cannot be verified" warning only applies to macOS and prevents the Sideloadly application from launching. Once the app is open, its iOS sideloading features should work as intended, provided your iOS device is properly configured (e.g., trust developer profiles, enable sideloading via AltStore or similar tools).
Q: Are there alternative tools to Sideloadly that don’t trigger this warning?
A: Some alternatives, like AltServer or Sideloadly’s officially signed version (if available), may bypass verification issues. However, most third-party sideloading tools face the same Gatekeeper restrictions. The most reliable long-term solution is to use apps distributed through the Mac App Store or obtain properly signed versions from trusted developers.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.