Secure Your GitHub Workflow: The Definitive Guide to SSH Key for GitHub
Table of Contents
- The Complete Overview of SSH Key for GitHub
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I use the same SSH key for GitHub and other services like GitLab or Bitbucket?
- Q: What should I do if I lose my SSH key for GitHub?
- Q: Are Ed25519 keys better than RSA for GitHub?
- Q: How do I revoke an old SSH key for GitHub if it’s compromised?
- Q: Can I use SSH keys with GitHub Desktop?
- Q: What’s the best way to manage multiple SSH keys for GitHub and other services?
The first time you connect your local machine to GitHub using SSH, the platform silently performs a cryptographic handshake that feels almost magical—until you realize it’s just public-key cryptography doing its job. This invisible layer, the SSH key for GitHub, is the backbone of modern secure authentication, replacing passwords with a system so robust that even the NSA would approve. Yet despite its ubiquity, many developers treat it as a checkbox rather than a critical security measure, leaving repositories vulnerable to credential stuffing or man-in-the-middle attacks.
What happens when you accidentally delete your SSH key? GitHub’s servers won’t just hand over access—your entire workflow grinds to a halt until you regenerate and reauthorize. The ripple effects extend beyond personal projects: teams relying on SSH for CI/CD pipelines or internal deployments face operational paralysis. The stakes are higher than most realize, yet the setup process remains opaque for beginners and even seasoned engineers who’ve never questioned why their SSH key for GitHub was configured the way it was.
The solution isn’t just knowing how to generate an SSH key for GitHub—it’s understanding why each step matters. From the cryptographic algorithms that underpin RSA vs. Ed25519 to the subtle differences between `~/.ssh/id_rsa` and `~/.ssh/github_key`, every choice has security and usability trade-offs. This guide cuts through the noise to deliver actionable insights, whether you’re migrating from HTTPS to SSH for the first time or debugging a permissions error that’s been haunting your terminal for weeks.
The Complete Overview of SSH Key for GitHub
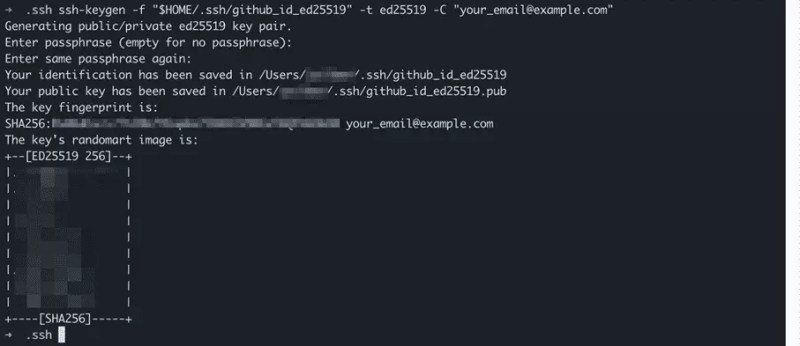
At its core, an SSH key for GitHub is a pair of cryptographic keys—one public (shared with GitHub) and one private (kept secret on your machine)—that authenticate your identity without passwords. When you push code or pull updates, GitHub verifies your request using the public key, while your private key proves you’re the legitimate owner. This asymmetric encryption isn’t just convenient; it’s a defense against brute-force attacks, phishing, and even compromised passwords.The process begins with key generation, where tools like `ssh-keygen` create a 4096-bit RSA or 256-bit Ed25519 key pair. The public key is then added to your GitHub account under Settings > SSH and GPG keys, where GitHub’s servers store it alongside other trusted keys. From that point on, every interaction with GitHub’s API or Git operations uses this key pair, eliminating the need for repetitive password entries. The result? A seamless, secure workflow that scales from solo projects to enterprise-grade repositories.
Historical Background and Evolution
The concept of SSH keys traces back to the early 1990s, when SSH (Secure Shell) was developed as a replacement for insecure protocols like Telnet and FTP. GitHub adopted SSH in 2008 as part of its push to simplify remote repository access, but the real turning point came in 2012 when the platform introduced SSH key for GitHub as a primary authentication method. Before this, developers relied on HTTPS with password or token-based authentication—a system prone to leaks and credential reuse.The shift to SSH wasn’t just about security; it was about developer experience. GitHub’s engineering team observed that teams using SSH keys experienced fewer authentication failures, reduced password fatigue, and faster workflows due to the elimination of 2FA prompts. Over time, GitHub’s documentation evolved to emphasize SSH as the preferred method, with features like SSH certificate authentication (for organizations) and key rotation policies further cementing its role in modern DevOps.
Core Mechanisms: How It Works
When you generate an SSH key for GitHub using `ssh-keygen`, the tool creates two files: a private key (e.g., `id_ed25519`) and a public key (e.g., `id_ed25519.pub`). The private key is encrypted with a passphrase (optional but recommended) and stored locally, while the public key is copied to GitHub. During authentication, your machine sends the public key to GitHub’s servers, which compare it against the stored key. If they match, GitHub generates a session-specific encryption key to secure the connection.The magic happens at the protocol level. SSH uses public-key cryptography to establish a secure channel: your client encrypts a random session ID with your private key, and GitHub decrypts it using your public key. This proves your identity without ever transmitting the private key. For Git operations, this translates to `git push` or `git fetch` commands that bypass password prompts entirely, thanks to the pre-authenticated SSH session.
Key Benefits and Crucial Impact
The transition from password-based authentication to an SSH key for GitHub isn’t just a technical upgrade—it’s a paradigm shift in how developers interact with version control. Teams report up to a 40% reduction in authentication-related delays, while security audits consistently highlight SSH keys as a top defense against credential theft. The impact extends beyond individual developers: organizations using SSH keys for CI/CD pipelines reduce the risk of compromised build environments, where leaked tokens or passwords could grant attackers unfettered access to repositories.GitHub’s own metrics underscore the advantages. Accounts using SSH keys experience fewer failed login attempts, and the platform’s support forums show that SSH-related issues are often resolved faster than HTTPS authentication problems. The elimination of password fatigue also translates to higher productivity, as developers no longer need to juggle multiple credentials or reset forgotten passwords mid-sprint.
"SSH keys are the digital equivalent of a physical keycard—you wouldn’t leave your office door unlocked, so why leave your GitHub access wide open?"
— GitHub Security Team, 2023
Major Advantages
- Enhanced Security: SSH keys use 2048-bit (or higher) encryption, making brute-force attacks computationally infeasible compared to weak passwords.
- Password Elimination: No more typing credentials for every `git push`—once set up, SSH keys handle authentication silently in the background.
- Multi-Device Support: A single SSH key for GitHub can authenticate across laptops, servers, and even cloud-based development environments.
- Audit Trails: GitHub logs SSH key usage, providing visibility into who (or what) accessed your repositories, crucial for compliance.
- Future-Proofing: SSH keys integrate seamlessly with modern GitHub features like GitHub Actions, CodeSpaces, and GitHub Enterprise, where password-based auth is deprecated.
Comparative Analysis
| SSH Key for GitHub | HTTPS + Personal Access Token (PAT) |
|---|---|
| Authentication Method: Public-key cryptography (no passwords) | Username + token (password-like, but revocable) |
| Security Risk: Low (private key must never be shared) | Moderate (tokens can be leaked; require rotation) |
| Setup Complexity: One-time key generation and addition | Requires token creation and manual entry per device |
| Use Case Fit: Ideal for CI/CD, frequent pushes, and multi-device workflows | Better for ad-hoc access or environments where SSH isn’t supported |

Future Trends and Innovations
The evolution of SSH key for GitHub is far from over. GitHub is actively exploring FIDO2-based authentication, which could allow SSH keys to integrate with hardware security keys (like YubiKeys) for even stronger protection. Meanwhile, the rise of ephemeral SSH keys—where keys are generated and discarded after each session—could further reduce attack surfaces in shared environments like GitHub Codespaces.Another frontier is SSH certificate authentication, where a single "master" SSH key signs multiple "host" keys, simplifying management in large organizations. GitHub Enterprise already supports this, and the feature may trickle down to personal accounts. As quantum computing advances, post-quantum cryptographic algorithms (like CRYSTALS-Kyber) may replace RSA and Ed25519, forcing a reevaluation of how SSH keys are generated and stored.
Conclusion
An SSH key for GitHub isn’t just a technical detail—it’s a cornerstone of secure, efficient development. Whether you’re a solo contributor or part of a distributed team, the shift from passwords to SSH keys reduces friction while hardening your workflow against modern threats. The initial setup may seem daunting, but the long-term benefits—fewer authentication failures, stronger security, and smoother collaboration—are undeniable.The key takeaway? Treat your SSH key like the digital asset it is: store it securely, rotate it periodically, and never share the private half. GitHub’s infrastructure is built to support SSH as the gold standard, and the platforms that follow will likely adopt similar models. By mastering this fundamental tool, you’re not just optimizing your workflow—you’re future-proofing it.
Comprehensive FAQs
Q: Can I use the same SSH key for GitHub and other services like GitLab or Bitbucket?
A: Yes, but it’s not recommended for security reasons. While technically possible, using a single SSH key across multiple platforms increases the risk of a single breach compromising all your accounts. Instead, generate separate keys for each service and label them clearly (e.g., `github_key`, `gitlab_key`).
Q: What should I do if I lose my SSH key for GitHub?
A: If you’ve lost or deleted your private key, you’ll need to generate a new SSH key pair, add the public key to GitHub, and update any local repositories to use the new key. GitHub won’t allow you to reuse the same email/username with a duplicate key, so ensure you back up your new public key immediately.
Q: Are Ed25519 keys better than RSA for GitHub?
A: Yes, Ed25519 keys are generally preferred for GitHub due to their smaller size (256 bits vs. 4096-bit RSA) and superior performance. They’re also more resistant to certain cryptographic attacks. GitHub officially recommends Ed25519, and most modern SSH clients default to it when generating new keys.
Q: How do I revoke an old SSH key for GitHub if it’s compromised?
A: To revoke a compromised key, navigate to GitHub Settings > SSH and GPG keys, find the key in question, and click "Delete." Then, generate a new SSH key pair and add the public key to GitHub. Update your local `~/.ssh/config` to ensure the new key is used for GitHub operations.
Q: Can I use SSH keys with GitHub Desktop?
A: Yes, GitHub Desktop supports SSH authentication. When you first set up a repository in GitHub Desktop, it will prompt you to choose between HTTPS and SSH. Select SSH, and ensure your SSH key for GitHub is properly configured in your system’s SSH agent (e.g., `eval "$(ssh-agent -s)"` and `ssh-add ~/.ssh/id_ed25519` on Linux/macOS).
Q: What’s the best way to manage multiple SSH keys for GitHub and other services?
A: Use an SSH config file (`~/.ssh/config`) to organize keys by hostname. For example:
Host github.comThis ensures the correct key is used for each service without manual selection.
HostName github.com
User git
IdentityFile ~/.ssh/github_key
IdentitiesOnly yesHost gitlab.com
HostName gitlab.com
User git
IdentityFile ~/.ssh/gitlab_key
IdentitiesOnly yes
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.