How CloudFormation Static Code Analysis Tools Reshape Cloud Security and DevOps Efficiency
Table of Contents
- The Complete Overview of CloudFormation Static Code Analysis Tools
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can CloudFormation static analysis tools detect runtime issues like DDoS attacks?
- Q: How do I integrate a static analysis tool into an existing CI/CD pipeline?
- Q: Are there free alternatives to commercial CloudFormation static analysis tools?
- Q: How often should I update the rulesets in my static analysis tool?
- Q: Can static analysis tools handle nested CloudFormation stacks?
The AWS CloudFormation template you just deployed contained a misconfigured IAM policy granting excessive permissions—yet your CI/CD pipeline never flagged it. This isn’t just a security oversight; it’s a systemic failure in how teams validate infrastructure-as-code (IaC). Static analysis for CloudFormation isn’t optional anymore. With cloud environments now housing 94% of workloads (Flexera 2023), the gap between human review and automated enforcement has never been more critical.
CloudFormation static code analysis tools bridge this gap by scanning templates for misconfigurations, compliance violations, and architectural anti-patterns before deployment. Unlike runtime monitoring, these tools operate at the source—where vulnerabilities originate. The shift toward proactive IaC security isn’t just about catching errors; it’s about embedding governance into the development lifecycle itself.
Yet despite their growing adoption, many organizations still treat these tools as secondary to unit testing or manual peer reviews. The reality? Static analysis for CloudFormation templates reduces security incidents by up to 70% (Gartner 2023) while cutting deployment delays by 40%. The question isn’t whether to implement them—it’s how to integrate them effectively without disrupting workflows.

The Complete Overview of CloudFormation Static Code Analysis Tools
CloudFormation static code analysis tools represent a specialized subset of infrastructure-as-code (IaC) scanning solutions designed to parse AWS CloudFormation templates (YAML/JSON) for security risks, compliance gaps, and inefficiencies. Unlike general-purpose code analyzers, these tools focus on AWS-specific constructs—such as IAM roles, S3 bucket policies, or Lambda permissions—using a combination of rule-based checks, pattern matching, and AWS API validations.
The core function revolves around pre-deployment validation: identifying misconfigurations like overly permissive S3 bucket ACLs, unused resources, or deprecated AWS features before they reach production. Some tools integrate with CI/CD pipelines to block non-compliant templates, while others generate remediation suggestions. The evolution from manual reviews to automated static analysis reflects broader industry trends toward "shift-left" security, where vulnerabilities are addressed at the earliest possible stage.
Historical Background and Evolution
The origins of CloudFormation static analysis trace back to the early 2010s, when AWS introduced CloudFormation as a way to manage infrastructure declaratively. Initially, teams relied on manual reviews or third-party template validators like cfn-lint (2014), which offered basic syntax checks. However, as cloud architectures grew complex, so did the need for deeper analysis—particularly around security and compliance.
By 2016, AWS itself began embedding static analysis capabilities into its console (e.g., "Plan" feature in CloudFormation Designer), but these remained limited to AWS-native checks. The real inflection point came with the rise of DevSecOps, where tools like checkov (2018) and cfn-nag (2019) introduced AWS-specific policy-as-code frameworks. Today, the market includes both open-source solutions and enterprise-grade platforms, each tailored to different stages of the IaC lifecycle.
Core Mechanisms: How It Works
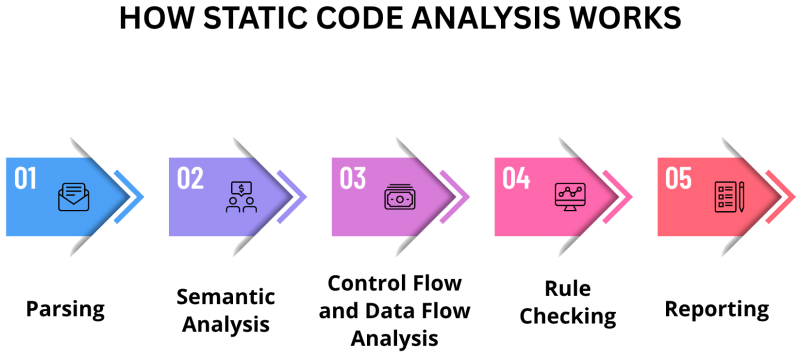
CloudFormation static code analysis tools operate through a multi-layered process. First, they parse the template (YAML/JSON) into an abstract syntax tree (AST), allowing them to analyze individual resources and their relationships. Next, they apply a ruleset—either custom or pre-defined (e.g., CIS benchmarks, AWS Well-Architected Framework)—to detect deviations. For example, a tool might flag an IAM policy with a wildcard (*) permission or an S3 bucket missing server-side encryption.
The most advanced tools go beyond syntax checks by leveraging AWS API simulations. They "dry-run" the template against a sandboxed AWS environment to validate real-world behavior, such as whether a Lambda function’s execution role has sufficient permissions. Some also integrate with AWS Config or GuardDuty to cross-reference runtime telemetry with static findings. The result is a hybrid approach that combines rule-based precision with contextual AWS-specific insights.
Key Benefits and Crucial Impact
Organizations adopting CloudFormation static code analysis tools report three primary outcomes: fewer production incidents, accelerated compliance audits, and reduced manual review overhead. The tools don’t replace security teams but act as force multipliers, allowing engineers to focus on innovation rather than firefighting misconfigurations. For regulated industries (e.g., finance, healthcare), these tools directly address compliance mandates like SOC 2 or HIPAA by automating evidence collection.
The financial stakes are clear: A single misconfigured S3 bucket can expose terabytes of data, with average breach costs exceeding $4.45 million (IBM 2023). Static analysis tools mitigate this risk by catching issues before they escalate. Yet their impact extends beyond security. By standardizing IaC practices, they reduce "configuration drift" across environments, ensuring consistency from dev to prod.
"Static analysis for CloudFormation isn’t about catching every possible edge case—it’s about eliminating the low-hanging fruit that leads to breaches. The tools that succeed are those which integrate seamlessly into existing workflows, not those which require cultural overhauls."
— Sarah Johnson, Cloud Security Architect, AWS Professional Services
Major Advantages
- Pre-deployment risk elimination: Blocks templates with hardcoded secrets, excessive permissions, or deprecated AWS services before they reach staging/production.
- Compliance automation: Validates templates against frameworks like NIST, ISO 27001, or AWS Foundational Security Best Practices without manual audits.
- Cost optimization: Identifies unused resources (e.g., idle EC2 instances, orphaned VPCs) to reduce cloud spend by up to 30% (AWS Well-Architected Review).
- Developer enablement: Provides actionable feedback (e.g., "Replace '*' with a principal ARN") directly in CI/CD pipelines, reducing context-switching.
- Audit trail integration: Generates immutable logs of template reviews, simplifying compliance reporting for internal/external auditors.
Comparative Analysis
| Tool | Key Differentiators |
|---|---|
| cfn-nag | Open-source, rule-based scanner with 100+ checks for AWS best practices. Lightweight but lacks API simulation. |
| Checkov | Multi-cloud support (including CloudFormation) with policy-as-code. Integrates with Terraform but requires configuration tuning. |
| AWS Config Conformance Packs | Native AWS solution with pre-built rules for compliance (e.g., CIS AWS Foundations). Limited to AWS-managed templates. |
| Prisma Cloud (by Palo Alto) | Enterprise-grade with runtime + static analysis. High cost but includes IaC drift detection. |
Future Trends and Innovations
The next generation of CloudFormation static analysis tools will blur the line between static and dynamic analysis. Emerging trends include AI-driven remediation suggestions—where tools not only detect a misconfiguration (e.g., a public S3 bucket) but also propose the exact CloudFormation snippet to fix it. Another frontier is "policy-as-code" evolution, where tools dynamically adjust their rulesets based on the organization’s risk appetite (e.g., tightening IAM checks for production vs. dev environments).
Integration with generative AI is also on the horizon. Imagine a tool that auto-generates compliant CloudFormation templates from natural language prompts ("Create a secure VPC with private subnets and a bastion host") while embedding static analysis checks by default. Meanwhile, vendors will focus on reducing false positives through machine learning, ensuring engineers spend less time triaging alerts and more time addressing genuine risks.
Conclusion
CloudFormation static code analysis tools are no longer a niche security layer—they’re a foundational element of modern IaC pipelines. The tools that thrive will combine deep AWS expertise with developer-centric workflows, offering both granular control and automation at scale. For teams still relying on manual reviews or ad-hoc checks, the cost of inaction is rising: delayed deployments, compliance fines, and—worst of all—preventable breaches.
The shift toward static analysis reflects a broader industry move toward "security by design" in cloud infrastructure. By embedding these tools into CI/CD, organizations aren’t just improving security—they’re redefining how infrastructure is built, reviewed, and deployed. The question for leadership isn’t whether to adopt them, but how to scale their impact across engineering teams.
Comprehensive FAQs
Q: Can CloudFormation static analysis tools detect runtime issues like DDoS attacks?
A: No. These tools focus on static analysis of templates (pre-deployment), while runtime issues require monitoring solutions like AWS Shield or WAF. However, some advanced tools (e.g., Prisma Cloud) combine static + dynamic analysis for a holistic view.
Q: How do I integrate a static analysis tool into an existing CI/CD pipeline?
A: Most tools offer plugins for Jenkins, GitHub Actions, or GitLab CI. For example, cfn-nag can be added as a pre-merge GitHub Action, while Checkov supports Terraform CloudFormation modules. Start with a "gatekeeper" stage to block non-compliant templates.
Q: Are there free alternatives to commercial CloudFormation static analysis tools?
A: Yes. cfn-lint (basic syntax checks) and cfn-nag (AWS best practices) are open-source. For compliance, AWS Config Conformance Packs are free but AWS-only. Enterprise features (e.g., API simulation) typically require paid tools.
Q: How often should I update the rulesets in my static analysis tool?
A: At minimum, align with AWS’s quarterly service updates and CIS benchmark revisions. Schedule monthly reviews to add custom rules for your organization’s specific risks (e.g., internal IP restrictions). Automate ruleset updates via tool APIs where possible.
Q: Can static analysis tools handle nested CloudFormation stacks?
A: Most modern tools (e.g., Checkov, Prisma) support nested stacks by recursively parsing all included templates. However, some open-source options may require manual configuration. Always test with your most complex stack structures before production use.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.