
How to Select the Best Static Code Analysis Tools for Modern Development
The shift toward static code analysis tools reflects broader industry demands for security-first development. High-profile breaches and compliance mandates...
Tag
The shift toward static code analysis tools reflects broader industry demands for security-first development. High-profile breaches and compliance mandates...

The stakes are higher than ever. High-profile breaches tied to misconfigured cloud resources—like the 2021 Capital One incident—often trace back to oversight...

The AWS CloudFormation template you just deployed contained a misconfigured IAM policy granting excessive permissions—yet your CI/CD pipeline never flagged it...

Software vulnerabilities don’t just emerge—they’re often baked into the code from the start. A single overlooked dependency, a misconfigured API, or a poorly...

What sets core security static analysis apart is its precision. Traditional vulnerability scanners often produce false positives, drowning security teams in...

Yet for many teams, the concept remains abstract. Static analysis tools scan for everything from syntax errors to complex logic bugs, but their true power lies...

The stakes are higher than ever. High-profile breaches in Android apps often trace back to overlooked static analysis warnings—misconfigured dependencies...

The OWASP static code analysis ecosystem has evolved from niche academic tools into a cornerstone of modern DevSecOps pipelines. Unlike dynamic analysis, which...

Yet, many organizations stumble at the first hurdle: they deploy tools without clear policies, leaving false positives to clutter dashboards or real threats...

Yet the true power of embedded static code analysis lies in its contextual awareness. Modern tools don’t just flag issues—they correlate findings with project...

Java remains the backbone of enterprise systems, powering everything from Android apps to large-scale financial platforms. Yet, beneath its robust architecture...

Swift’s rise as Apple’s flagship language has reshaped mobile and desktop development, but with its growing adoption comes heightened scrutiny over security...
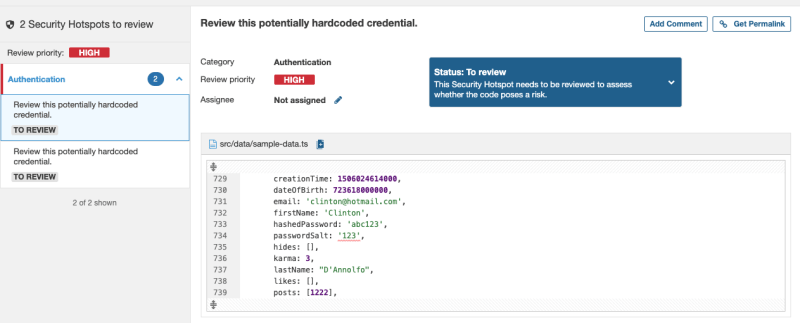
Yet adoption remains uneven. Many teams rely on ad-hoc linting or basic TypeScript checks, unaware that modern static analysis engines—like ESLint plugins...
Static analysis isn’t just another buzzword in software development—it’s the silent guardian of code integrity. While dynamic testing catches vulnerabilities...