How to Enable JavaScript in Internet Explorer: A Definitive Technical Guide
Table of Contents
- The Complete Overview of Enabling JavaScript in Internet Explorer
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Why does enabling JavaScript in Internet Explorer still matter if Microsoft is phasing it out?
- Q: How do I enable JavaScript in Internet Explorer 11 for all zones?
- Q: Can Group Policy enforce JavaScript settings across an enterprise?
- Q: What should I do if enabling JavaScript doesn’t fix a broken website?
- Q: Are there security risks to enabling JavaScript in Internet Explorer?
- Q: How can I test if JavaScript is working in Internet Explorer?
Internet Explorer’s JavaScript engine has long been a double-edged sword—powerful enough to run enterprise intranets and legacy applications but often disabled by default in modern security-conscious environments. The need to enable JavaScript in Internet Explorer persists in industries where outdated systems still dominate, from financial institutions to government portals. Without it, dynamic content fails to load, forms remain static, and interactive dashboards become useless. Even today, some corporate networks maintain IE for backward compatibility, making this a persistent technical challenge.
The irony lies in IE’s declining relevance: Microsoft’s own Edge browser has rendered it obsolete, yet the demand for activating JavaScript support in Internet Explorer hasn’t vanished. Many IT administrators still grapple with balancing security policies and legacy requirements, often resorting to manual configurations or group policy tweaks. The process isn’t just about flipping a switch—it involves understanding IE’s security zones, compatibility modes, and the subtle differences between versions. A misstep here could expose systems to vulnerabilities while failing to resolve the core issue.
For developers and sysadmins alike, the stakes are high. A single misconfigured setting can break critical workflows, while over-permissive policies invite risks. This guide cuts through the noise, offering precise steps to enable JavaScript in Internet Explorer across different environments, from standalone machines to enterprise deployments. Whether you’re troubleshooting a stubborn intranet or ensuring compliance with outdated software, the answers lie in the details.
The Complete Overview of Enabling JavaScript in Internet Explorer
Internet Explorer’s JavaScript handling is deeply tied to its security model, which evolved alongside Microsoft’s shifting priorities. Unlike modern browsers that default to enabling scripts for performance, IE historically treated JavaScript as a potential security risk—especially in public or untrusted zones. This design choice forced administrators to explicitly configure JavaScript in Internet Explorer, often through multiple layers of settings. The process varies slightly between IE versions (7 through 11), with later iterations introducing stricter security defaults under Microsoft’s "Enhanced Security Configuration" (ESC) for corporate environments.The core challenge lies in IE’s layered approach to script execution. JavaScript isn’t just a binary toggle; it’s governed by:
1. Security Zone Settings (Local Intranet, Trusted Sites, Internet)
2. ActiveX Controls (which often rely on scripting)
3. Compatibility View (which can override script permissions)
4. Group Policy Objects (GPOs) in enterprise deployments
5. Registry tweaks for granular control
Neglecting any of these can leave scripts disabled even after the primary setting is adjusted. For example, a site marked as "Restricted" in the Internet Zone will block scripts regardless of the global JavaScript setting. This complexity explains why many users report failed attempts to activate JavaScript in Internet Explorer—they’ve only addressed one part of the equation.
Historical Background and Evolution
Internet Explorer’s relationship with JavaScript began in the late 1990s, when Microsoft’s Trident engine first implemented ECMAScript compliance. Early versions (IE 4–6) were notorious for inconsistent behavior, often crashing when encountering malformed scripts—a problem exacerbated by the "browser wars" era. By IE 7, Microsoft introduced the Internet Explorer Security Zones, a framework that allowed administrators to categorize websites by trust level and apply granular permissions. This was a direct response to rising concerns about cross-site scripting (XSS) attacks, but it also created friction for developers relying on JavaScript in Internet Explorer.The real turning point came with IE 8, which bundled XSS Filtering and stricter DOM security measures. While these improvements enhanced security, they also broke legacy scripts that depended on older quirks. Enterprises, particularly those in finance or healthcare, resisted upgrading due to compatibility risks, forcing IT teams to maintain IE 7 or 8 in "Enterprise Mode" for years. Meanwhile, Microsoft’s push for IE 11 in Windows 10/11 brought Enhanced Protected Mode (EPM), which further isolated scripting execution—requiring explicit opt-ins for ActiveX and script access in certain zones.
Today, the need to enable JavaScript in Internet Explorer is largely a relic of corporate inertia. Yet, industries like aviation, manufacturing, and government still rely on IE for internal tools built decades ago. The persistence of this requirement underscores a broader truth: legacy systems don’t disappear overnight, and their dependencies often outlive the browsers designed to support them.
Core Mechanisms: How It Works
At its core, enabling JavaScript in Internet Explorer involves two primary pathways:1. User-Level Configuration (via browser UI or settings)
2. System-Level Configuration (via Group Policy or registry edits)
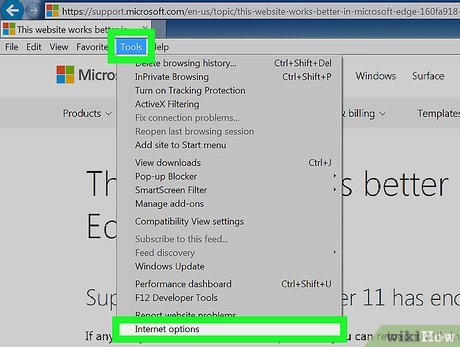
The user-level method is straightforward but limited to individual machines. It relies on the Internet Options dialog, where JavaScript can be toggled under the Security tab for each zone. However, this approach fails in enterprise environments where policies lock down settings. System-level changes, by contrast, require administrative privileges and often involve modifying the Windows Registry or deploying GPOs to enforce script permissions across domains.
The technical mechanism hinges on IE’s security zone mappings and script execution flags. When a page loads, IE checks:
For example, a site in the Internet Zone with "Scripting disabled" will block all `