How Do I Enable JavaScript in Chrome? The Definitive Solution
Table of Contents
- The Complete Overview of Enabling JavaScript in Chrome
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Why does Chrome still block JavaScript after enabling it in Site Settings?
- Q: Can I enable JavaScript for specific sites only?
- Q: How do I enable JavaScript via command line or flags?
- Q: What if JavaScript is disabled by my organization’s IT policy?
- Q: Does disabling JavaScript improve security?
- Q: How do I reset Chrome’s JavaScript settings if they’re corrupted?
JavaScript isn’t just a feature—it’s the backbone of interactive websites. Without it, dynamic content like real-time updates, form validations, or even basic animations fails to load. Yet, despite its critical role, many users accidentally disable it in Chrome, leaving them baffled when pages render as static shells. The question "how do I enable JavaScript in Chrome?" is one of the most frequent tech support queries, and the answer isn’t always straightforward. Some users report enabling it only to find scripts still blocked by extensions or site-specific policies. Others struggle with conflicting settings across Chrome profiles. The solution requires precision: knowing where to toggle the switch, verifying the change, and accounting for edge cases like enterprise policies or security software interference.
The process itself is deceptively simple—just a few clicks—but the nuances matter. For developers, JavaScript enables debugging tools that rely on console logs or DevTools. For casual users, it’s the difference between a seamless shopping cart checkout and a broken "Add to Cart" button. Even seasoned professionals occasionally overlook the JavaScript enable Chrome setting when troubleshooting, assuming the issue lies elsewhere. The key is methodical verification: confirm the setting isn’t overridden by a site’s own restrictions, check for extension conflicts, or ensure Chrome isn’t running in an incognito mode with stricter defaults. Without this, enabling JavaScript becomes a frustrating cycle of reboots and guesswork.
Chrome’s approach to JavaScript differs from other browsers, particularly in how it handles permissions and security contexts. While Firefox and Safari offer granular controls per site, Chrome consolidates settings under Site Settings, making it easier to overlook. This design choice, though efficient, can lead to confusion when users search for "how to turn on JavaScript in Chrome" and find outdated guides referencing legacy flags or extension-based toggles. The modern method—accessible via three dots in the top-right corner—isn’t always intuitive, especially for users who’ve never adjusted browser permissions before. Below, we break down the exact steps, historical context, and hidden factors that can derail even the most straightforward enablement.

The Complete Overview of Enabling JavaScript in Chrome
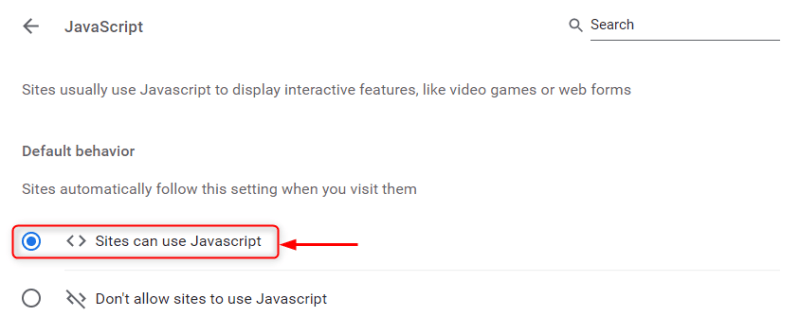
Enabling JavaScript in Chrome is a two-step process: locating the setting and confirming its activation. The primary method involves navigating to Site Settings (accessed via the three-dot menu), where Chrome groups permissions for cameras, location, and—critically—JavaScript. Here, users can toggle the switch for all sites or customize it per domain. However, this isn’t the only path. Advanced users might prefer command-line flags (e.g., `--disable-javascript` for testing), while enterprise environments may enforce policies via Group Policy Objects (GPOs) or Mobile Device Management (MDM) tools. The latter often requires IT intervention, as these settings override user preferences. For most individuals, though, the JavaScript enable Chrome toggle in Site Settings suffices—provided they’ve ruled out extensions like uBlock Origin or NoScript, which can silently block scripts regardless of Chrome’s native setting.The verification step is where many users stumble. Simply toggling the switch doesn’t guarantee functionality. Chrome caches settings aggressively, and some sites may enforce their own restrictions (e.g., via `` or CSP headers). To confirm JavaScript is active, users should visit a test page like https://www.isjavascriptenabled.com or inspect the Network tab in DevTools for dynamic requests. If the page still reports JavaScript as disabled, the issue likely lies with an extension, a corrupted Chrome profile, or a misconfigured security suite like Windows Defender SmartScreen, which sometimes intercepts script execution.
Historical Background and Evolution
JavaScript’s integration into Chrome reflects its broader evolution from a niche scripting language to an essential web technology. When Chrome launched in 2008, it inherited Mozilla’s JavaScript engine (later V8) and positioned itself as the browser of choice for developers. Early versions of Chrome bundled JavaScript with other permissions under Content Settings, a less intuitive system that required users to manually uncheck "Block scripts" for each site. This clunky approach led to widespread confusion, as users searching for "how to enable JavaScript in Chrome" would find conflicting instructions—some advising to disable extensions, others suggesting registry edits (a red flag for malware risks). By Chrome 45 (2015), Google streamlined permissions into Site Settings, consolidating JavaScript, cookies, and notifications into a single interface. This change aligned with the shift toward user-centric controls, though it also introduced new pitfalls: users might enable JavaScript globally only to later discover site-specific overrides in Incognito Mode.The modern JavaScript enable Chrome workflow is a product of Chrome’s push for performance and security. In recent years, Google has deprioritized legacy flags (like `--enable-javascript-harmony`) in favor of standardized settings, reducing the need for manual tweaks. However, this simplification hasn’t eliminated edge cases. For instance, Chrome’s Sandbox feature, designed to isolate untrusted scripts, can inadvertently block legitimate code if misconfigured. Similarly, Strict Site Isolation (enabled by default in Chrome 67+) may throttle JavaScript execution for cross-site requests, requiring developers to optimize their code. These advancements underscore why enabling JavaScript isn’t just about toggling a switch—it’s about understanding Chrome’s layered security model.
Core Mechanisms: How It Works
At its core, Chrome’s JavaScript handling relies on three layers: the V8 engine, the Content Security Policy (CSP), and the permission model. The V8 engine compiles JavaScript into machine code, but its execution depends on Chrome’s CSP headers, which dictate what scripts are allowed to run. For example, a site with `Content-Security-Policy: script-src 'self'` will only execute scripts from its own domain, regardless of Chrome’s global JavaScript setting. This is why users enabling JavaScript via Site Settings might still encounter errors: the site itself is restricting execution. The permission model adds another variable. Chrome evaluates JavaScript requests against:1. User-configured settings (Site Settings or flags).
2. Site-specific policies (CSP, `` tags).
3. Extension interference (e.g., ad blockers with script-blocking rules).
The interaction between these layers explains why a simple "how to turn on JavaScript in Chrome" guide often falls short. For instance, if an extension like Disconnect has a rule to block `*.google-analytics.com`, Chrome’s native JavaScript toggle won’t override it. The solution requires either disabling the extension or whitelisting the domain in its settings. Similarly, enterprise-managed Chrome instances may enforce JavaScript disable Chrome via GPOs, requiring IT to adjust policies in `gpedit.msc` or the Chrome Admin Template.
Key Benefits and Crucial Impact
JavaScript isn’t just a convenience—it’s a necessity for modern web functionality. Without it, features like SPAs (Single-Page Applications), real-time collaboration tools (e.g., Google Docs), and interactive maps (Google Maps, Leaflet) become unusable. Developers rely on JavaScript for client-side rendering, API calls, and debugging tools like DevTools’ console. Even basic tasks—such as auto-filling forms or validating inputs—depend on script execution. The impact of disabling JavaScript extends beyond user experience: e-commerce sites lose sales when checkout scripts fail, while developers waste hours debugging issues that trace back to a misconfigured JavaScript enable Chrome setting.The stakes are higher for security-conscious users. While JavaScript can introduce vulnerabilities (e.g., XSS attacks), disabling it entirely exposes users to malware via PDFs, images, or malicious downloads—since Chrome’s built-in protections often rely on script-based sandboxing. The balance lies in selective enabling: allowing JavaScript for trusted sites while blocking it for untrusted sources. Chrome’s Site Settings accommodates this with per-domain controls, but users must actively manage these to avoid false positives. The trade-off is clear: enabling JavaScript unlocks functionality but requires vigilance against exploits.
"JavaScript is the difference between a static brochure and a dynamic application. Disabling it is like turning off the engine of a car—you might still move, but you’re not going anywhere fast." — John Resig, Creator of jQuery
Major Advantages
Enabling JavaScript in Chrome delivers five critical advantages:- Access to Modern Web Features: Enables SPAs (React, Angular), WebSockets, and WebAssembly, which power apps like Trello, Notion, and Figma.
- Improved Developer Tools: DevTools’ console, debugger, and performance profiler require JavaScript to function. Disabling it renders these tools useless.
- Seamless User Experiences: Features like infinite scroll (Facebook, Twitter), drag-and-drop (Google Drive), and real-time updates (Slack) depend on JavaScript.
- Enhanced Security for Trusted Sites: Modern JavaScript frameworks (e.g., Next.js) include built-in protections like CSP headers and Web Crypto API, which mitigate risks when enabled selectively.
- Compatibility with Enterprise Tools: SaaS platforms (Salesforce, Zoom) and internal dashboards often require JavaScript for authentication and data processing.
Comparative Analysis
| Aspect | Chrome (JavaScript Enabled) | Chrome (JavaScript Disabled) ||--------------------------|-----------------------------------------------|--------------------------------------------|
| Dynamic Content | Full functionality (animations, SPAs) | Static pages only |
| Developer Tools | Full DevTools access | Console and debugger broken |
| Security Risk | Moderate (mitigated by CSP/sandboxing) | Higher (no script-based protections) |
| Performance Impact | Minimal (V8 optimizations) | Slower (fallback to server-side rendering) |
| Enterprise Use | Required for SaaS/internal apps | Incompatible with most modern tools |
Future Trends and Innovations
The future of JavaScript in Chrome is shaped by two competing forces: performance optimization and security hardening. Google is pushing WASM (WebAssembly) as a complement to JavaScript, allowing high-performance tasks (e.g., video encoding) to offload work from the V8 engine. Meanwhile, Privacy Sandbox initiatives aim to replace third-party cookies with JavaScript-based alternatives, reducing tracking while preserving ad functionality. These changes will force users to revisit "how to enable JavaScript in Chrome" as settings become more granular—e.g., toggling WASM support or adjusting Privacy Sandbox permissions.Another trend is AI-driven JavaScript optimization. Chrome’s Backforward Cache and Lazy Loading features already reduce script execution overhead, but future updates may use machine learning to predict which scripts to prioritize. For users, this means fewer manual adjustments to JavaScript enable Chrome settings, as Chrome automatically balances performance and security. However, enterprise environments may resist these changes, preferring explicit controls over AI-driven defaults. The result? A fragmented landscape where the answer to "how do I enable JavaScript in Chrome?" will vary by user type—consumers relying on automated optimizations, while developers and IT teams maintaining fine-grained control.
Conclusion
Enabling JavaScript in Chrome is rarely as simple as flipping a switch. The process demands an understanding of Chrome’s multi-layered permission system, from Site Settings to CSP headers, and an awareness of how extensions and enterprise policies can override user preferences. The key takeaway is verification: after enabling JavaScript, test with a tool like isjavascriptenabled.com to confirm changes took effect. For persistent issues, inspect the Network tab in DevTools to identify blocked requests, then adjust settings accordingly—whether that means whitelisting a domain in an ad blocker or consulting IT for GPO conflicts.The broader lesson is that JavaScript’s role in Chrome is evolving. As WebAssembly and Privacy Sandbox reshape the web, users will need to adapt their JavaScript enable Chrome strategies. For now, the classic method—navigating to Site Settings and toggling the switch—remains the most reliable starting point. But the future suggests that Chrome may soon handle these decisions for us, blending automation with user control in ways we’re only beginning to explore.
Comprehensive FAQs
Q: Why does Chrome still block JavaScript after enabling it in Site Settings?
A: Chrome’s JavaScript setting can be overridden by:
1. Extensions (e.g., uBlock Origin with script-blocking rules).
2. Site-specific policies (CSP headers or `` tags).
3. Incognito Mode defaults (some sites enforce stricter rules).
4. Enterprise policies (GPOs or MDM tools).
To diagnose, open DevTools (F12), check the Console for errors, and inspect the Network tab for blocked requests. If an extension is the culprit, either disable it or add an exception for the site.
Q: Can I enable JavaScript for specific sites only?
A: Yes. In Chrome, go to Settings > Site Settings > JavaScript, then toggle "Sites can use JavaScript" to "Ask" or "Allow." For granular control, use the "Add" button to whitelist individual domains. This is useful for balancing security and functionality on untrusted sites.
Q: How do I enable JavaScript via command line or flags?
A: Chrome doesn’t provide a direct flag to enable JavaScript globally, but you can test with:
Q: What if JavaScript is disabled by my organization’s IT policy?
A: Enterprise-managed Chrome instances often enforce JavaScript settings via:
Q: Does disabling JavaScript improve security?
A: Partially, but at a steep cost. Disabling JavaScript blocks:
Q: How do I reset Chrome’s JavaScript settings if they’re corrupted?
A: If Chrome’s Site Settings or flags are misconfigured:
1. Clear Chrome’s cache and cookies: Go to Settings > Privacy and Security > Clear browsing data.
2. Reset permissions: In Site Settings, click "Reset permissions" for JavaScript.
3. Re-enable via flags: Close Chrome, then launch it with `--disable-extensions` to test if an extension is causing issues.
4. Reinstall Chrome: As a last resort, back up bookmarks and reinstall Chrome to restore defaults.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.