How to Enable JavaScript in Internet Explorer (And Why It Still Matters)
Table of Contents
- The Complete Overview of Enabling JavaScript in Internet Explorer
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Why does my organization still need to enable "internet explorer allow javascript" if IE is dead?
- Q: Can I enable JavaScript in IE without affecting security?
- Q: How do I enable JavaScript in IE via Group Policy for an entire domain?
- Q: What should I do if enabling JavaScript breaks an application?
- Q: Is there a way to allow JavaScript only for specific websites in IE?
- Q: Will enabling JavaScript in IE slow down the browser?
Internet Explorer’s stubborn persistence in enterprise environments isn’t just nostalgia—it’s a calculated necessity for legacy systems that refuse to modernize. When developers or IT administrators encounter the need to enable JavaScript in Internet Explorer, they’re often dealing with internal applications, embedded systems, or third-party tools that were built for an era when IE was the default. The irony? Microsoft’s own end-of-life announcement hasn’t stopped organizations from maintaining these configurations, forcing them to navigate arcane settings like "internet explorer allow javascript" in security policies or group policies. The question isn’t why this is needed, but how to do it without triggering compatibility nightmares.
The process of enabling JavaScript in Internet Explorer isn’t just about flipping a toggle—it’s a dance between security protocols, legacy dependencies, and the occasional "works on my machine" paradox. For instance, a financial institution might still rely on an IE-based kiosk system for internal audits, where disabling scripts would break critical validation workflows. Meanwhile, a manufacturing plant’s SCADA interface, designed in the 2000s, might crash if JavaScript is blocked. These aren’t edge cases; they’re the bread-and-butter scenarios where "internet explorer allow javascript" becomes a line in a scripted deployment rather than an ad-hoc fix.
What makes this topic particularly thorny is the interplay between corporate security policies and technical debt. Many organizations have hardened their IE environments to the point where enabling scripts requires administrative privileges, often triggering IT tickets that read like cryptic manuals. The solution isn’t just a checkbox—it’s a multi-step validation process, from checking ActiveX controls to ensuring compatibility view settings aren’t overriding script execution. Even then, some applications demand specific versions of VBScript or JScript, adding another layer of complexity. The result? A scenario where "allowing JavaScript in Internet Explorer" isn’t just a setting—it’s a risk assessment.
The Complete Overview of Enabling JavaScript in Internet Explorer
Internet Explorer’s JavaScript support isn’t a monolithic feature—it’s a patchwork of technologies stitched together over two decades, each with its own quirks. At its core, enabling "internet explorer allow javascript" involves two primary pathways: user-level configuration (for individual machines) and enterprise-wide policies (via Group Policy or registry edits). The former is straightforward but limited to single instances, while the latter is the domain of IT administrators managing fleets of legacy systems. What’s often overlooked is that IE’s scripting engine—Trident—has evolved in ways that conflict with modern security models. For example, Internet Explorer 11 introduced Enhanced Security Configuration (ESC), which defaults to blocking scripts unless explicitly permitted, a relic of Microsoft’s push toward Edge while still supporting IE for compatibility.The challenge deepens when considering third-party extensions or custom plugins that rely on IE’s scripting model. Some enterprise applications, particularly those using Silverlight or legacy ActiveX controls, may fail silently if JavaScript is disabled, only revealing the issue during critical operations. This has led to a hybrid approach where "internet explorer allow javascript" is enabled selectively—perhaps only for specific domains or internal IP ranges—rather than globally. The trade-off? Balancing security with functionality in an environment where IE mode in Edge isn’t always a viable replacement. For organizations stuck in the "IE trap," this means maintaining parallel configurations: one for modern browsers, another for the scripts that refuse to die.
Historical Background and Evolution
The origins of "internet explorer allow javascript" trace back to IE4, when Microsoft introduced JScript as its proprietary implementation of ECMAScript. Unlike Netscape’s JavaScript, JScript was tightly coupled with IE’s rendering engine, creating a feedback loop where websites optimized for IE relied on its quirks. By the time IE6 dominated the market in the early 2000s, "allowing JavaScript" wasn’t just a feature—it was a de facto standard for corporate intranets. Developers built entire ecosystems around IE’s scripting model, from DHTML-based dashboards to VBScript-driven automation tools, knowing full well that disabling scripts would break critical workflows.The turning point came with IE8’s introduction of "Compatibility View" and IE11’s Enhanced Security Configuration, both of which treated JavaScript as a potential threat vector. Microsoft’s shift toward Edge (Chromium) and the eventual deprecation of IE in 2022 forced organizations to confront a harsh reality: their reliance on "internet explorer allow javascript" was no longer sustainable. Yet, the inertia of legacy systems—particularly in government, healthcare, and industrial sectors—meant that IE couldn’t be retired overnight. Today, "enabling JavaScript in Internet Explorer" is less about modern web development and more about maintaining critical infrastructure that was never designed to evolve.
Core Mechanisms: How It Works
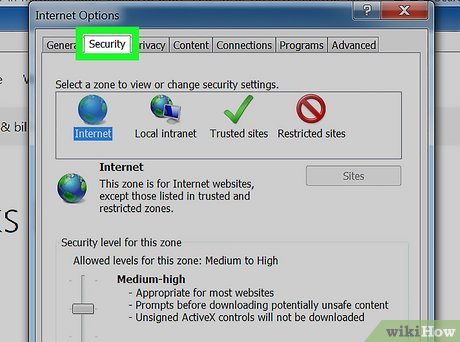
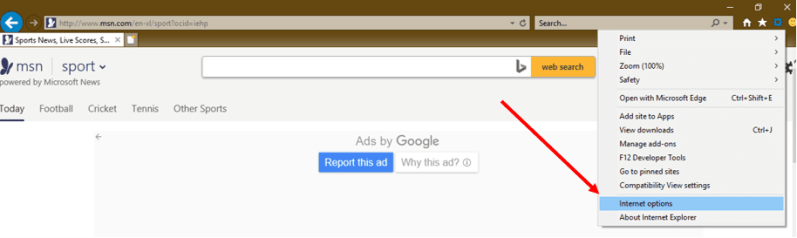
Under the hood, "internet explorer allow javascript" is controlled by a combination of registry settings, Group Policy objects (GPOs), and browser security zones. The most direct method is adjusting the Internet Options menu:1. Navigate to Tools > Internet Options > Security.
2. Select the Internet or Local Intranet zone (depending on the use case).
3. Click Custom Level, then scroll to Scripting.
4. Ensure "Allow active scripting" is selected, not "Disable" or "Prompt."
For enterprise environments, administrators typically use Group Policy Editor (`gpedit.msc`) to enforce these settings across domains. The key registry keys involved are:
What’s less obvious is that IE’s security zones (Internet, Local Intranet, Trusted Sites) can override these settings. For example, a site marked as "Local Intranet" might default to script blocking unless explicitly configured. This is why "internet explorer allow javascript" often requires zone-specific tweaks, not just a global enable.
Key Benefits and Crucial Impact
The decision to enable JavaScript in Internet Explorer isn’t arbitrary—it’s a calculated risk in industries where downtime is catastrophic. For instance, a hospital’s patient monitoring system built on IE-based dashboards might fail if scripts are disabled, leading to false alarms or data corruption. Similarly, manufacturing plants using SCADA interfaces for real-time equipment control often rely on IE’s scripting for data visualization and automation. The cost of disabling scripts in these cases isn’t just technical—it’s operational.That said, the risks are undeniable. Enabling "internet explorer allow javascript" in an unpatched IE environment is akin to leaving a server door unlocked—exploit kits like EternalBlue and drive-by downloads have historically targeted IE’s scripting engine. The balance lies in selective enabling: restricting script execution to internal IP ranges, trusted domains, or specific applications via Application Compatibility Toolkit (ACT) policies. This granular approach minimizes exposure while preserving functionality.
"Internet Explorer’s scripting model was never designed for security—it was designed for compatibility. The moment you enable JavaScript in IE, you’re inheriting two decades of technical debt, from XSS vulnerabilities to ActiveX exploits. The only way to mitigate this is to treat it as a quarantine zone, not a production environment." — Security Architect, Fortune 500 IT Department
Major Advantages
Despite its drawbacks, enabling "internet explorer allow javascript" offers critical advantages in specific scenarios:- Legacy Application Support: Many line-of-business (LOB) applications—such as SAP GUI, Oracle Forms, or legacy ERP systems—require IE’s scripting engine to function. Disabling scripts would render these tools unusable without costly migrations.
- Embedded System Compatibility: Kiosks, digital signage, and industrial HMIs often run custom IE-based applications that rely on VBScript or JScript for interactivity. Enabling scripts ensures these systems remain operational without hardware replacements.
- Internal Tooling and Automation: Corporate intranets, SharePoint 2010/2013, and legacy Outlook Web Access (OWA) may depend on IE’s scripting for form validation, dynamic content, or macro execution.
- Third-Party Plugin Dependencies: Silverlight-based applications, Java applets (via IE’s NPAPI support), and ActiveX controls often require JavaScript to initialize. Disabling scripts would break these integrations entirely.
- Regulatory and Compliance Requirements: Some government or financial systems are locked into IE due to FIPS compliance or legacy certification standards. Enabling scripts is a necessary evil to maintain audit trails and validation.
Comparative Analysis
| Aspect | Internet Explorer (Legacy) | Modern Browsers (Chrome/Edge/Firefox) ||--------------------------|-------------------------------------------------------|----------------------------------------------------|
| Scripting Engine | Trident (JScript/VBScript) – Proprietary, outdated | Blink/Gecko/WebKit – Standards-compliant, secure |
| Security Model | Zone-based, easily bypassed via misconfigurations | Sandboxed, site isolation, regular updates |
| Compatibility | High for 2000s-era LOB apps, low for modern web | High for modern web, low for legacy IE-only tools |
| Deployment Control | Requires GPO/registry edits for enterprise | Centralized via extension policies or MDM |
| Future-Proofing | End-of-life (June 2022), no updates | Actively developed, automatic security patches |
Future Trends and Innovations
The future of "internet explorer allow javascript" is, by definition, limited. Microsoft’s IE mode in Edge is the closest successor, but it’s not a drop-in replacement—some scripts fail due to engine differences, and ActiveX remains unsupported. Organizations are increasingly turning to virtualization (running IE in Azure Virtual Desktop or VMware) or containerization (using IE in Docker) to isolate legacy dependencies. However, these solutions introduce latency and management overhead, making them viable only for critical, non-replaceable systems.A more promising trend is automated migration tools, such as Microsoft’s "IE Mode Migration Guide" or third-party solutions like Browsium and ThinScale. These tools analyze script dependencies and repackage applications for modern browsers, reducing the need to "allow JavaScript in Internet Explorer" altogether. Yet, for the foreseeable future, "IE-specific scripting" will remain a niche but necessary configuration in enterprise IT.
Conclusion
The persistence of "internet explorer allow javascript" settings is a testament to the sheer inertia of legacy systems. While modern browsers have rendered IE obsolete for most use cases, the real-world constraints of enterprise IT—budget cycles, regulatory hurdles, and technical debt—ensure that IE lingers. The key takeaway isn’t whether to enable scripts, but how to do it safely. This means segmenting IE environments, restricting script execution to trusted zones, and planning for eventual migration rather than treating IE as a permanent solution.For IT professionals, the lesson is clear: "internet explorer allow javascript" is a temporary fix, not a long-term strategy. The goal should be to document dependencies, test modern alternatives, and phase out IE—but only when the business can afford the transition. Until then, the settings will remain, a relic of a digital era that refuses to fade entirely.
Comprehensive FAQs
Q: Why does my organization still need to enable "internet explorer allow javascript" if IE is dead?
Many enterprise applications, government systems, and industrial controls were built for IE and rely on its scripting engine. Disabling scripts would break validation workflows, automation tools, or third-party plugins that have no modern equivalent. Until these systems are migrated (a process that can take years), "allowing JavaScript in Internet Explorer" remains a necessity, not a choice.
Q: Can I enable JavaScript in IE without affecting security?
Not entirely. IE’s scripting model is inherently insecure by modern standards, but you can minimize risks by:
Q: How do I enable JavaScript in IE via Group Policy for an entire domain?
1. Open Group Policy Management Console (`gpmc.msc`).
2. Navigate to Computer Configuration > Administrative Templates > Windows Components > Internet Explorer > Security Features > Turn off Active Scripting.
3. Set it to Disabled (this enables scripting by default).
4. For zone-specific controls, edit:
Note: Some settings may require registry edits if GPO options are limited.
Q: What should I do if enabling JavaScript breaks an application?
If an application fails after enabling "internet explorer allow javascript", the issue is likely one of:
Q: Is there a way to allow JavaScript only for specific websites in IE?
Yes, but it requires manual zone management:
1. Open Internet Options > Security > Custom Level.
2. For each zone (Internet, Local Intranet, Trusted Sites), adjust:
Limitation: IE doesn’t support per-site script toggling like modern browsers—you must group sites by zone.
For finer control, consider third-party tools like Browsium or IE Virtualization.
Q: Will enabling JavaScript in IE slow down the browser?
Yes, but the impact varies:
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.