Mastering Software Software Integration Testing: The Hidden Key to Seamless System Harmony
Table of Contents
- The Complete Overview of Software Software Integration Testing
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does software software integration testing differ from API testing?
- Q: What are the most common pitfalls in software software integration testing?
- Q: Can software software integration testing be fully automated?
- Q: How do microservices change the approach to software software integration testing?
- Q: What metrics should we track to measure integration testing effectiveness?
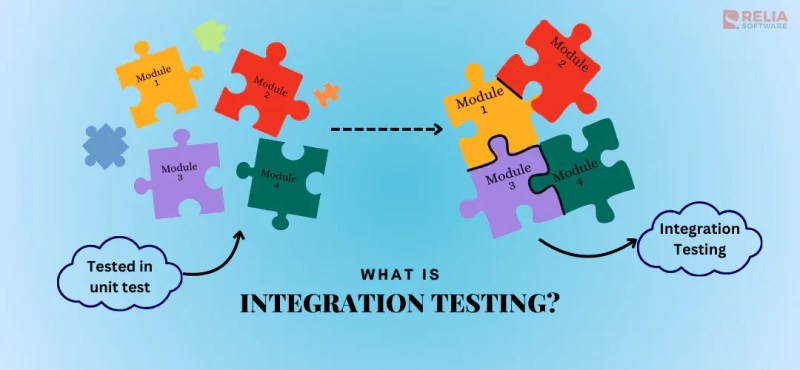
Integration failures cost businesses an estimated $1.4 trillion annually—not just in lost revenue, but in reputational damage and operational paralysis. The root cause? Neglecting the critical phase where disparate software components must communicate without friction. This is where software software integration testing becomes non-negotiable. Unlike unit testing, which isolates individual modules, integration testing exposes the brittle seams between systems—whether it’s a legacy ERP talking to a cloud-based CRM or microservices exchanging data in real-time.
The challenge lies in its complexity. Modern architectures—with their hybrid clouds, third-party APIs, and event-driven workflows—demand more than ad-hoc validation. A misconfigured webhook can cascade into a data breach; a timing mismatch between services can trigger system-wide outages. The stakes are higher when integrating software software (i.e., applications designed to work together but often built by different vendors), where proprietary protocols and undocumented dependencies lurk beneath the surface.
Yet, despite its critical role, integration testing remains an afterthought in many organizations. Development teams rush to deploy features, QA focuses on isolated components, and operations teams scramble to patch failures post-launch. The result? A feedback loop where integration issues become a fire drill rather than a preventative discipline. This article dismantles the myths and outlines a structured approach to software integration testing—one that aligns with Agile, DevOps, and zero-trust security principles.
The Complete Overview of Software Software Integration Testing
Software software integration testing is the systematic validation of interactions between two or more software systems to ensure they function as a unified whole. It bridges the gap between component-level testing (unit/integration) and end-to-end system validation, addressing three core challenges: data consistency, functional compatibility, and performance under load. The term "software software" emphasizes the focus on applications interacting with other applications, as opposed to hardware-software interactions or user-facing UX testing.
This discipline is not monolithic. It spans API integration testing (validating REST/gRPC endpoints), database integration testing (ensuring CRUD operations sync across systems), and event-driven integration testing (verifying message queues like Kafka or RabbitMQ). The scope expands further when factoring in third-party integrations (e.g., payment gateways, SaaS tools) or hybrid environments (on-premise + cloud). Unlike traditional integration testing, which often assumes controlled environments, software software integration testing must account for real-world variability—latency, rate limits, and vendor-specific behaviors.
Historical Background and Evolution
The origins of integration testing trace back to the 1960s, when mainframe systems required manual "smoke tests" to verify peripheral device compatibility. However, the term software integration testing gained traction in the 1980s with the rise of structured programming and COBOL-based enterprise systems. Early methodologies relied on pairwise testing (checking combinations of inputs) and boundary-value analysis, but these were limited to monolithic architectures.
The turning point came with the adoption of object-oriented design in the 1990s, which introduced the concept of module integration testing. Teams began using tools like Rational TestManager to stitch together components, but the real paradigm shift occurred in the 2000s with the advent of service-oriented architecture (SOA). SOAP and later REST APIs forced developers to treat integration as a first-class concern. The rise of cloud computing in the 2010s accelerated this trend, as software software integration testing became essential for microservices—where services are loosely coupled but must still maintain data integrity across transactions. Today, the discipline has fragmented into specialized niches, from contract testing (e.g., Pact) to chaos engineering (e.g., Gremlin), each addressing a unique facet of system interdependence.
Core Mechanisms: How It Works
At its core, software software integration testing follows a three-phase lifecycle: pre-integration, active integration, and post-integration validation. The pre-integration phase involves defining contracts (e.g., OpenAPI specs, Avro schemas) and setting up mock environments to simulate dependencies. Active integration employs techniques like stubbing (replacing real services with controlled responses) and driver testing (using test harnesses to invoke components). The final phase shifts to end-to-end flows, where automated scripts mimic user journeys—e.g., a customer placing an order that triggers inventory updates, billing, and shipping notifications.
Modern approaches leverage continuous integration/continuous delivery (CI/CD) pipelines to automate these phases. Tools like Postman, SoapUI, and Karate handle API-level validation, while infrastructure-as-code (IaC) platforms (Terraform, Ansible) manage test environments. For complex software software ecosystems, teams adopt hybrid strategies: static analysis (e.g., checking for deprecated API versions) alongside dynamic testing (e.g., load-testing API gateways). The key innovation here is shift-left integration testing—integrating validation earlier in the SDLC to catch issues before they reach production. This requires cultural changes, such as embedding integration specialists in Agile squads or adopting feature flags to isolate risky integrations.
Key Benefits and Crucial Impact
The ROI of robust software software integration testing extends beyond bug prevention. It directly impacts business agility, security, and customer trust. Organizations that treat integration as an afterthought often face cascading failures during mergers, scalability spikes, or regulatory audits. For example, a 2022 study by Capgemini found that 68% of digital transformation projects stalled due to integration bottlenecks—costing companies an average of $2.3 million per delayed release. Conversely, firms like Netflix and Uber achieve 99.99% uptime by treating integration testing as a competitive differentiator, not a compliance checkbox.
Yet, the benefits are not just quantitative. Poorly integrated systems create technical debt that compounds over time. A single undetected schema mismatch in a database integration can require months of refactoring. Meanwhile, security vulnerabilities—such as exposed API endpoints or misconfigured OAuth flows—often originate from integration gaps. The software software integration testing process acts as a force multiplier for DevSecOps, ensuring that security controls (e.g., API gateways, service meshes) are tested alongside functional requirements.
"Integration testing is the canary in the coal mine of software development. If the canary dies, it’s not because the mine is safe—it’s because the system is already failing."
— Martin Fowler, Chief Scientist at ThoughtWorks
Major Advantages
- Early Detection of Incompatibilities: Identifies schema mismatches, protocol conflicts (e.g., HTTP vs. gRPC), or unsupported data types before deployment, reducing mean time to resolution (MTTR) by up to 70%.
- Enhanced Data Integrity: Validates ACID compliance across distributed transactions, preventing partial updates or orphaned records in critical workflows (e.g., financial settlements).
- Vendor and Third-Party Risk Mitigation: Tests integrations with external APIs (e.g., Stripe, Twilio) under edge cases like rate limiting or deprecated endpoints, avoiding vendor lock-in surprises.
- Performance Optimization: Exposes latency bottlenecks in inter-service communication, enabling optimizations like caching (Redis) or batch processing (SQS).
- Regulatory and Compliance Assurance: Ensures adherence to standards like GDPR (data residency), PCI-DSS (payment security), or HIPAA (healthcare interoperability) by validating cross-system data flows.
Comparative Analysis
| Aspect | Traditional Integration Testing | Modern Software Software Integration Testing |
|---|---|---|
| Scope | Limited to internal system boundaries (e.g., modules in a monolith). | Spans multi-vendor ecosystems, cloud providers, and third-party APIs. |
| Automation Level | Manual or scripted tests with high maintenance overhead. | CI/CD-native with self-healing test suites (e.g., TestContainers for ephemeral environments). |
| Security Focus | Reactive (patching vulnerabilities post-incident). | Proactive (integrating DAST/SAST in test pipelines, e.g., OWASP ZAP + SonarQube). |
| Environment Complexity | Static test beds (e.g., local VMs). | Dynamic, multi-cloud, and hybrid environments with infrastructure-as-code. |
Future Trends and Innovations
The next frontier for software software integration testing lies in AI-driven test generation and observability-first validation. Tools like Diffblue and Testim are already using ML to auto-generate integration test cases from API specs, while platforms like Lightstep and OpenTelemetry enable real-time distributed tracing to pinpoint integration failures in production. The rise of serverless architectures will further complicate testing, as ephemeral functions and event sources (e.g., AWS Lambda + EventBridge) require new validation paradigms—likely involving chaos testing to simulate cold starts or throttling.
Another critical shift is toward contract-first integration testing, where APIs are treated as legal agreements between services. Frameworks like Pact and WireMock enforce "consumer-driven contracts," ensuring that producers and consumers of data align on schemas and behaviors before implementation. As organizations adopt platform engineering, integration testing will evolve into a shared responsibility between Dev, QA, and SRE teams, with metrics like integration maturity scores (IMS) quantifying risk exposure. The goal? Moving from reactive debugging to predictive validation—where integration health is monitored in real-time, not just during release cycles.
Conclusion
Software software integration testing is no longer a niche concern but the linchpin of modern software delivery. The organizations that thrive in the next decade will be those that treat integration as a first-class citizen—embedded in design, automated in pipelines, and continuously validated in production. The tools exist; the challenge is cultural. Teams must shift from viewing integration testing as a gatekeeper to a collaborative practice, where developers, testers, and operations engineers co-own the health of interconnected systems.
For leaders, the message is clear: underinvesting in integration is a gamble with predictable outcomes—failed deployments, security breaches, and lost market share. The alternative? A proactive strategy that leverages software software integration testing to turn complexity into a competitive advantage. The question is no longer if you’ll encounter integration issues, but when you’ll catch them—and how severely they’ll impact your business.
Comprehensive FAQs
Q: How does software software integration testing differ from API testing?
A: While API testing focuses on validating individual endpoints (e.g., HTTP status codes, response payloads), software software integration testing examines the end-to-end flow between systems. For example, API testing might verify that a `/checkout` endpoint returns a 200 status, but integration testing ensures that the checkout triggers inventory deductions, sends a confirmation email, and logs the transaction—across multiple services. API testing is a subset of integration testing when dealing with software software ecosystems.
Q: What are the most common pitfalls in software software integration testing?
A: The top three pitfalls are:
1. Over-reliance on manual testing: Without automation, integration validation becomes a bottleneck in CI/CD pipelines.
2. Ignoring edge cases: Teams often test happy paths but miss scenarios like network partitions, timeouts, or malformed data from third-party APIs.
3. Lack of environment parity: Testing in staging doesn’t replicate production’s latency, rate limits, or vendor-specific behaviors (e.g., a payment gateway’s fraud detection rules).
Q: Can software software integration testing be fully automated?
A: No, but it can achieve >90% automation with the right strategy. Fully automated scenarios include:
Q: How do microservices change the approach to software software integration testing?
A: Microservices introduce three key challenges:
1. Distributed complexity: Each service may have its own database, requiring tests for eventual consistency (e.g., using the Saga pattern).
2. Dynamic dependencies: Services are often replaced or scaled independently, necessitating contract testing (e.g., Pact) to ensure backward compatibility.
3. Observability gaps: Without centralized logging (e.g., ELK stack) or tracing (e.g., Jaeger), debugging integration failures becomes akin to solving a jigsaw puzzle with missing pieces.
Tools like TestContainers help by spinning up ephemeral instances of dependent services for isolated testing.
Q: What metrics should we track to measure integration testing effectiveness?
A: Critical metrics include:
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.