How Source Code Scanning Tools Reshape Security and Efficiency in Software Development
Table of Contents
- The Complete Overview of Source Code Scanning Tools
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do source code scanning tools differ from traditional penetration testing?
- Q: Can source code scanning tools replace manual code reviews?
- Q: What are the most common false positives in source code scanning?
- Q: How do open-source source code scanning tools compare to proprietary solutions?
- Q: What metrics should organizations track to measure the effectiveness of source code scanning?
The rise of source code scanning tools marks a pivotal shift in how organizations approach security, compliance, and efficiency. These tools no longer operate as mere add-ons but as critical components embedded within the software development lifecycle (SDLC). From identifying hardcoded secrets to flagging outdated dependencies, their capabilities have evolved into a non-negotiable layer of defense against increasingly sophisticated cyber threats. The stakes are higher than ever: a single overlooked vulnerability can lead to data breaches, regulatory fines, or reputational damage—all of which can cripple even the most established enterprises.
Yet, the adoption of these tools remains uneven. Some teams treat them as a checkbox exercise, running scans sporadically without integrating findings into their workflows. Others deploy them reactively, only after a breach or audit reveals gaps. The most forward-thinking organizations, however, recognize that source code scanning tools are not just about finding flaws—they’re about embedding security into the DNA of development. This requires a strategic approach: selecting the right tools, configuring them for precision, and fostering a culture where developers treat security as a shared responsibility.
The landscape of source code scanning tools is fragmented, with solutions catering to static analysis, dynamic testing, container scanning, and even AI-driven anomaly detection. Each serves a distinct purpose, yet their collective impact is transforming how code is written, reviewed, and deployed. Below, we dissect their mechanisms, compare their strengths, and examine the innovations that will define their next decade.
The Complete Overview of Source Code Scanning Tools
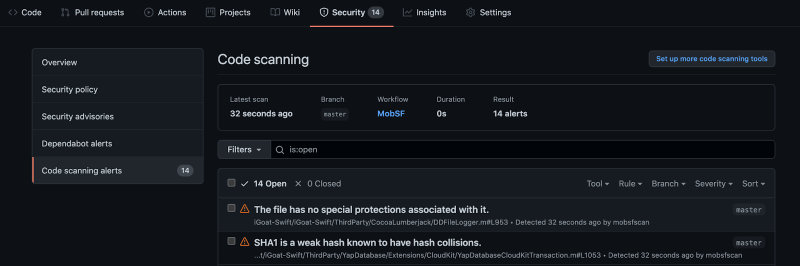
Source code scanning tools represent a fusion of automation and expertise, designed to parse, analyze, and interpret code with the precision of a seasoned auditor. At their core, these tools act as digital sentinels, scanning repositories, build artifacts, and runtime environments for vulnerabilities, compliance violations, and inefficiencies. They operate across multiple dimensions: static analysis (SAST) examines code without execution, dynamic analysis (DAST) tests running applications, and interactive analysis (IAST) bridges the gap by monitoring interactions between code and external systems. This multi-layered approach ensures that threats—whether logical flaws, misconfigurations, or supply chain risks—are identified at every stage of development.The effectiveness of source code scanning tools hinges on their ability to adapt to the complexity of modern software stacks. With the proliferation of microservices, serverless architectures, and third-party libraries, traditional scanning methods often fall short. Modern tools now leverage machine learning to detect patterns in codebases, integrate with CI/CD pipelines for real-time feedback, and even prioritize findings based on risk severity. This shift from reactive to proactive security is not just a technological upgrade—it’s a fundamental rethinking of how development teams collaborate with security teams.
Historical Background and Evolution
The origins of source code scanning tools can be traced back to the 1980s and 1990s, when early static analyzers emerged as academic research projects aimed at improving code quality. Tools like Lint (developed at Bell Labs) focused on syntax errors and style inconsistencies, laying the groundwork for more sophisticated analysis. The turn of the millennium brought commercial SAST solutions, such as Fortify and Checkmarx, which expanded their scope to include security vulnerabilities. These tools were initially criticized for high false-positive rates and steep learning curves, but they paved the way for broader adoption as security became a boardroom priority.The 2010s witnessed a paradigm shift with the rise of DevOps and the integration of security into continuous integration/continuous deployment (CI/CD) pipelines. Source code scanning tools evolved to support agile workflows, offering APIs, plugins for platforms like Jenkins and GitHub Actions, and seamless integration with version control systems. The introduction of Software Composition Analysis (SCA) tools, such as Black Duck and Snyk, further expanded their capabilities by scanning dependencies for known vulnerabilities in open-source libraries. Today, these tools are no longer optional—they’re embedded in the fabric of modern software development, with enterprises investing heavily in tools that can keep pace with the velocity of cloud-native and containerized environments.
Core Mechanisms: How It Works
The inner workings of source code scanning tools are a blend of pattern matching, abstract syntax tree (AST) analysis, and runtime instrumentation. Static analysis tools, for example, parse source code into an AST—a hierarchical representation of the code’s structure—to identify vulnerabilities like SQL injection, buffer overflows, or hardcoded credentials. These tools rely on a database of known patterns (signatures) and heuristics to flag potential issues, often supplemented by custom rules tailored to an organization’s specific risks. Dynamic analysis, on the other hand, executes the code in a controlled environment, monitoring behavior for anomalies such as memory leaks or unexpected network calls.More advanced source code scanning tools incorporate hybrid approaches, combining static and dynamic techniques with machine learning models trained on vast datasets of vulnerabilities. For instance, tools like CodeQL (by GitHub) use semantic code analysis to detect vulnerabilities that traditional pattern matching might miss. Meanwhile, interactive application security testing (IAST) tools inject probes into running applications to observe how inputs are processed, providing deeper insights into runtime behaviors. The result is a multi-faceted defense mechanism that adapts to the evolving tactics of attackers and the increasing complexity of software ecosystems.
Key Benefits and Crucial Impact
The adoption of source code scanning tools is driven by a convergence of security imperatives, regulatory demands, and operational efficiencies. Organizations that integrate these tools into their SDLC reduce the likelihood of costly vulnerabilities slipping into production, while also accelerating time-to-market by catching issues early. The financial stakes are undeniable: according to IBM’s Cost of a Data Breach Report, the average cost per breach in 2023 exceeded $4.45 million, with a significant portion attributable to preventable coding errors. Source code scanning tools mitigate this risk by shifting security left—identifying and remediating vulnerabilities before they reach end users.Beyond risk reduction, these tools enhance compliance with frameworks like ISO 27001, NIST, and PCI DSS, which mandate regular security assessments. They also foster a culture of accountability, where developers receive immediate feedback on security flaws, reducing the reliance on post-mortem audits. The ripple effects extend to supply chain security, as tools like Dependency-Track and FOSSA help organizations track the provenance of open-source components, mitigating risks from malicious or outdated libraries.
> "Security is no longer a gatekeeper—it’s a collaborator. The most effective source code scanning tools don’t just find vulnerabilities; they empower teams to build them out of the system entirely."
Major Advantages
- Early Detection of Vulnerabilities: Identifies flaws in the development phase, reducing remediation costs by up to 90% compared to post-deployment fixes.
- Compliance Automation: Streamlines adherence to regulatory standards with automated reporting and remediation workflows.
- Integration with DevOps: Seamless CI/CD integration enables real-time scanning, reducing the "shift-left" security gap.
- Open-Source Risk Management: SCA tools assess third-party dependencies for vulnerabilities, licensing issues, and supply chain risks.
- Customizable and Extensible: Supports organization-specific rules, allowing teams to tailor scans to unique threat models.
Comparative Analysis
| Tool Category | Key Differentiators |
|---|---|
| Static Analysis (SAST)(e.g., SonarQube, Checkmarx) | Deep code inspection without execution; ideal for early-stage vulnerability detection. Best for languages like Java, C++, and Python. |
| Dynamic Analysis (DAST)(e.g., OWASP ZAP, Burp Suite) | Tests running applications for runtime vulnerabilities; effective for web apps but limited to executable code. |
| Software Composition Analysis (SCA)(e.g., Snyk, Dependabot) | Focuses on open-source dependencies; scans for CVEs, license conflicts, and supply chain risks. |
| Hybrid/IAST(e.g., Contrast Security, Hdiv) | Combines static and dynamic analysis with runtime instrumentation; provides real-time vulnerability detection. |
Future Trends and Innovations
The next generation of source code scanning tools will be defined by AI-driven predictive analysis, where machine learning models anticipate vulnerabilities based on code patterns and historical attack data. Tools like GitHub’s CodeQL are already pioneering this approach, using symbolic execution to explore potential attack paths. Additionally, the rise of policy-as-code frameworks will enable organizations to enforce security rules programmatically, ensuring consistency across distributed teams. Another emerging trend is quantum-resistant cryptography scanning, as tools begin to assess code for vulnerabilities that could exploit future quantum computing threats.Beyond technical advancements, the adoption of source code scanning tools will be shaped by cultural shifts within development teams. As security becomes a shared responsibility, tools will evolve to provide more actionable insights—such as suggesting secure coding alternatives or integrating directly with IDEs for real-time feedback. The lines between security, development, and operations will blur further, with DevSecOps maturing into a seamless, automated process where scanning is as routine as writing unit tests.
Conclusion
Source code scanning tools have transitioned from niche security utilities to indispensable components of modern software development. Their ability to detect vulnerabilities, enforce compliance, and integrate with agile workflows makes them a cornerstone of DevSecOps strategies. However, their success depends on more than just tool selection—it requires organizational buy-in, continuous refinement of scanning policies, and a commitment to treating security as a collaborative effort.As the software landscape grows more complex, the role of these tools will only expand. Organizations that fail to adopt them risk falling behind in both security posture and operational efficiency. For those that embrace them strategically, source code scanning tools will not only protect their applications but also drive innovation by reducing technical debt and accelerating secure deployments.
Comprehensive FAQs
Q: How do source code scanning tools differ from traditional penetration testing?
A: Traditional penetration testing involves manual or automated attacks on running systems to identify vulnerabilities. In contrast, source code scanning tools analyze code statically or dynamically during development, catching issues before they reach production. While pen testing validates real-world exploitability, scanning tools provide broader coverage and earlier detection.
Q: Can source code scanning tools replace manual code reviews?
A: No. While source code scanning tools automate the detection of common vulnerabilities and coding standards violations, they lack the contextual judgment of human reviewers. Manual reviews are essential for assessing business logic flaws, architectural risks, and nuanced security decisions that tools cannot yet interpret.
Q: What are the most common false positives in source code scanning?
A: False positives often arise from overly broad rules (e.g., flagging harmless string concatenation as SQL injection), outdated vulnerability databases, or misconfigured tool settings. Mitigation strategies include tuning rule severity, leveraging custom exclusions, and validating findings through manual review or additional testing.
Q: How do open-source source code scanning tools compare to proprietary solutions?
A: Open-source tools like Semgrep or Bandit offer transparency, customization, and cost savings but may lack enterprise-grade support or advanced features. Proprietary solutions (e.g., Veracode, Checkmarx) provide polished UIs, dedicated support, and integrated compliance reporting, making them ideal for regulated industries. The choice depends on budget, team expertise, and specific security needs.
Q: What metrics should organizations track to measure the effectiveness of source code scanning?
A: Key metrics include:
- Vulnerability Detection Rate: Percentage of critical flaws identified before deployment.
- Mean Time to Remediation (MTTR): Average time taken to fix identified issues.
- False Positive Rate: Reduction in noise to improve developer trust.
- Compliance Pass Rate: Success in meeting regulatory or internal security policies.
- Cost Savings: Reduction in breach-related expenses or audit failures.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.