
How CloudFormation Static Code Analysis Security Hardens AWS Infrastructure
The stakes are higher than ever. High-profile breaches tied to misconfigured cloud resources—like the 2021 Capital One incident—often trace back to oversight...
Tag
The stakes are higher than ever. High-profile breaches tied to misconfigured cloud resources—like the 2021 Capital One incident—often trace back to oversight...

Yet the evolution of these tools isn’t just about catching SQL injections or hardcoded passwords. Modern code scanning tools now parse context—analyzing not...

The first line of defense in modern software development isn’t firewalls or encryption—it’s the code security scan tools embedded in every CI/CD pipeline...

Yet the transition isn’t seamless. Legacy compliance programs, built on spreadsheets and manual reviews, clash with the velocity of cloud-native environments...

Software vulnerabilities don’t wait for scheduled audits. They exploit flaws the moment code executes—whether in production or staging. This is where dynamic...
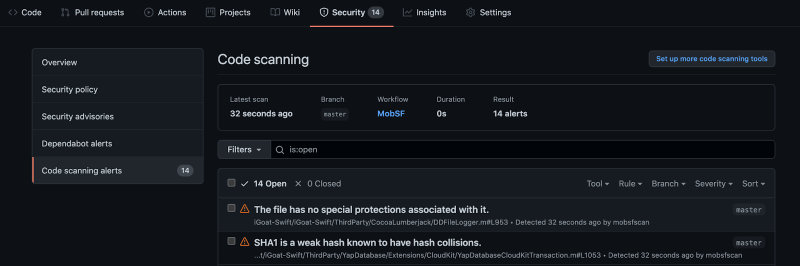
The race to secure software begins long before deployment—it starts in the codebase itself. Open source code scanning tools have emerged as the unsung heroes...

The OWASP static code analysis ecosystem has evolved from niche academic tools into a cornerstone of modern DevSecOps pipelines. Unlike dynamic analysis, which...

Modern software development is a high-stakes game where a single overlooked vulnerability can expose millions of users to exploitation. Traditional security...
Yet, the adoption of these tools remains uneven. Some teams treat them as a checkbox exercise, running scans sporadically without integrating findings into...