What Is Docker Image? The Hidden Engine Behind Modern Software Deployment
Table of Contents
- The Complete Overview of What Is Docker Image
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does a Docker image differ from a virtual machine (VM)?
- Q: Can I modify a Docker image after it’s been created?
- Q: What’s the difference between a Docker image and a container?
- Q: How do I optimize Docker images for security?
- Q: What happens if I delete a Docker image?
- Q: Can Docker images be used outside of Docker?
- Q: How do I share a Docker image with others?
- Q: What’s the best way to debug issues with a Docker image?
- Q: Are Docker images suitable for stateful applications?
- Q: How do I reduce the size of a Docker image?
Containers have reshaped how software is built, shipped, and run. At their foundation lies the Docker image—a self-contained, portable blueprint that encapsulates an application’s runtime environment, dependencies, and configurations. Unlike traditional virtual machines, which bundle an entire operating system, a Docker image distills the essentials: the code, libraries, and system tools needed to execute an application consistently across any infrastructure. This precision is why enterprises from startups to Fortune 500 companies rely on what is Docker image technology to eliminate the "works on my machine" problem.
The power of a Docker image isn’t just in its isolation—it’s in its reproducibility. A single command (`docker build`) can transform a developer’s local setup into an identical runtime anywhere, from a developer’s laptop to a production server in the cloud. This consistency is the backbone of modern CI/CD pipelines, where images serve as the immutable artifacts that flow seamlessly from development to deployment. Yet, despite its ubiquity, the mechanics of how a Docker image functions—its layers, its union file system, its relationship with containers—remain misunderstood by many practitioners.
To grasp why Docker images are the linchpin of containerization, consider this: without them, containers would be empty shells. The image is the template that defines the container’s identity—its operating system, user permissions, network ports, and even the environment variables that shape its behavior. Whether you’re orchestrating microservices with Kubernetes or deploying legacy monoliths, understanding what is Docker image isn’t optional; it’s foundational. Below, we dissect its architecture, trace its evolution, and explore why it remains the gold standard for software packaging in 2024.
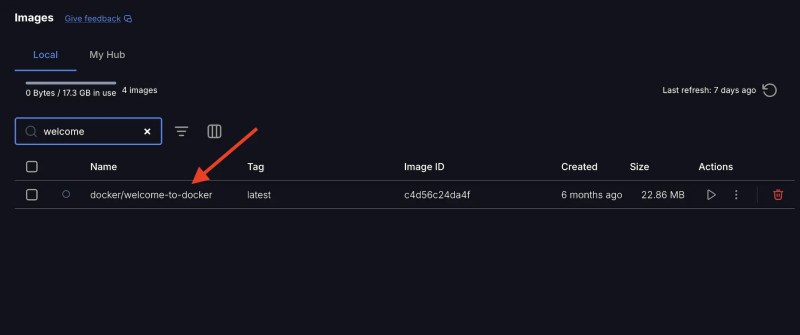
The Complete Overview of What Is Docker Image
A Docker image is a read-only template used to create Docker containers. It packages an application and all its dependencies—including the operating system libraries, configuration files, and runtime binaries—into a single, portable unit. This encapsulation ensures that an application runs identically in any environment, from a developer’s workstation to a scalable cloud deployment. The image itself is built from a Dockerfile, a script that defines each layer of the application’s environment, from the base OS to the final executable.
The magic of a Docker image lies in its layering system. Each instruction in the Dockerfile—such as installing a package or copying a file—creates a new layer. These layers are stacked and shared efficiently, reducing redundancy. For example, if multiple images use the same base OS (like Ubuntu 22.04), Docker reuses the underlying layers, saving storage and bandwidth. This efficiency is critical for large-scale deployments, where hundreds of images might coexist in a single registry. Understanding this structure is key to optimizing storage, security, and performance when working with what is Docker image architectures.
Historical Background and Evolution
The concept of containerization predates Docker, with early implementations like Linux containers (LXC) emerging in the 2000s. However, Docker—founded in 2010 by Solomon Hykes—popularized the technology by introducing a user-friendly API, a standardized format, and a vibrant ecosystem. Before Docker, deploying applications was a logistical nightmare: developers had to manually configure servers, reconcile dependency conflicts, and pray for consistency across environments. Docker’s introduction of the what is Docker image model changed that by automating the packaging process and enforcing consistency through immutable artifacts.
The evolution of Docker images reflects broader trends in software development. Early versions relied on large, monolithic images (often exceeding 1GB) that included full OS installations. Over time, best practices shifted toward minimalist images—using distroless base images or Alpine Linux—to reduce attack surfaces and improve performance. Today, Docker images are optimized for security, speed, and scalability, with features like multi-stage builds (introduced in Docker 17.05) allowing developers to separate build-time dependencies from runtime artifacts. This progression underscores how what is Docker image technology has matured from a niche tool to an industry standard.
Core Mechanisms: How It Works
At its core, a Docker image is a series of layered files stored in a content-addressable storage system. Each layer represents a step in the build process, from the base OS to the final application code. When a container is created from an image, Docker uses a union file system (like OverlayFS or AUFS) to combine these layers into a single, writable filesystem. This design ensures that changes made to a running container (e.g., modifying a config file) don’t affect the underlying image, preserving its immutability.
The relationship between images and containers is one of creation and execution. An image is the blueprint; a container is the running instance. When you run `docker run`, Docker fetches the specified image (if not local), creates a writable layer on top of it, and starts the container. The image’s metadata—including environment variables, exposed ports, and volume mounts—defines the container’s behavior. For example, an image tagged with `nginx:latest` will always pull the same set of configurations and binaries, ensuring that every container spun from it behaves predictably. This predictability is the cornerstone of what is Docker image reliability.
Key Benefits and Crucial Impact
Docker images have become the de facto standard for software deployment because they solve three critical problems: inconsistency, complexity, and scalability. Traditional deployment methods—such as manually installing dependencies or relying on virtual machines—often led to environment drift, where development and production setups diverged. Docker images eliminate this drift by encapsulating everything an application needs to run. They also reduce complexity by abstracting away infrastructure details, allowing developers to focus on code rather than server configurations.
The impact of Docker images extends beyond technical efficiency. They’ve democratized deployment, enabling small teams to compete with enterprises by leveraging cloud-native architectures. Startups can spin up production-grade environments in minutes, while large organizations use images to standardize deployments across thousands of servers. This standardization is particularly valuable in regulated industries, where compliance and auditability are paramount. As one Docker engineer noted, "A Docker image isn’t just a file—it’s a contract between developers and operations teams, ensuring that what’s built is what’s run."
— Solomon Hykes, Founder of Docker
"The goal of Docker was to make it as easy to deploy an application as it is to run a script. Images were the key to achieving that goal by turning deployment into a repeatable, automated process."
Major Advantages
- Consistency Across Environments: A Docker image ensures that an application runs the same way in development, testing, and production, eliminating the "it works on my machine" syndrome.
- Portability: Images can be deployed anywhere—on-premises, in the cloud, or on edge devices—without modification, thanks to Docker’s cross-platform compatibility.
- Isolation and Security: Each container runs in its own isolated environment, reducing the risk of conflicts between applications and limiting the blast radius of security vulnerabilities.
- Efficient Resource Usage: Unlike virtual machines, containers share the host OS kernel, leading to lower overhead and faster startup times.
- Version Control and Rollbacks: Docker images are versioned and can be rolled back to previous states, simplifying troubleshooting and updates.
Comparative Analysis
While Docker images dominate the container ecosystem, other technologies offer alternative approaches to packaging and deployment. Understanding these differences is crucial for selecting the right tool for your use case.
| Docker Image | Alternative (e.g., Podman, LXC) |
|---|---|
| Uses a client-server architecture (Docker daemon required). | Podman is daemonless, using libpod for direct container management. |
| Optimized for portability and ease of use, with a vast ecosystem (Docker Hub, Kubernetes integration). | LXC focuses on system containerization without higher-level orchestration tools. |
| Supports multi-stage builds for optimized final images. | Podman supports rootless containers, improving security in shared environments. |
| Widely adopted in cloud-native and microservices architectures. | LXC is often preferred for traditional server virtualization tasks. |

Future Trends and Innovations
The Docker image model continues to evolve, driven by demands for speed, security, and sustainability. One emerging trend is the rise of distroless images, which strip down images to only the essential runtime components, reducing attack surfaces and compliance overhead. Another innovation is the integration of eBPF (extended Berkeley Packet Filter) into container runtimes, enabling more granular security policies and performance optimizations at the kernel level. Additionally, the shift toward serverless architectures is pushing Docker images to become lighter and more ephemeral, with frameworks like Knative abstracting away the need for long-running containers.
Looking ahead, the next frontier for Docker images may lie in confidential computing, where images are encrypted in-use to protect sensitive workloads. Projects like Intel SGX and AMD SEV are already exploring how to combine containerization with hardware-based isolation. Meanwhile, the adoption of WebAssembly (Wasm) could further blur the lines between containers and serverless functions, creating a new class of portable, lightweight runtimes. For practitioners, staying ahead means mastering not just what is Docker image today, but anticipating how these trends will reshape deployment strategies tomorrow.
Conclusion
A Docker image is more than a technical artifact—it’s the cornerstone of a paradigm shift in how software is built and deployed. By encapsulating an application’s entire runtime environment, it eliminates guesswork, reduces friction, and enables scalability at unprecedented levels. The principles behind what is Docker image technology—immutability, portability, and consistency—are now table stakes in modern software engineering. Whether you’re a developer, DevOps engineer, or IT architect, understanding Docker images isn’t just about using a tool; it’s about embracing a mindset that prioritizes reproducibility and efficiency.
The future of Docker images will likely be defined by two forces: the need for even greater security and the push for sustainability. As cloud-native architectures mature, images will become smaller, faster, and more secure, while also aligning with green computing initiatives (e.g., reducing carbon footprints through optimized builds). For organizations, the lesson is clear: investing in Docker images today is an investment in agility, security, and resilience tomorrow. The question isn’t whether to adopt them—it’s how to leverage them most effectively.
Comprehensive FAQs
Q: How does a Docker image differ from a virtual machine (VM)?
A Docker image shares the host OS kernel with containers, leading to lower overhead and faster startup times compared to VMs, which require a full guest OS. Images are also more portable and lightweight, making them ideal for microservices and cloud-native deployments.
Q: Can I modify a Docker image after it’s been created?
A Docker image itself is immutable—once built, it cannot be altered. However, you can create a new image based on an existing one using `docker commit` or by extending it in a Dockerfile. Changes to a running container (e.g., file modifications) are stored in a writable layer and don’t affect the underlying image.
Q: What’s the difference between a Docker image and a container?
A Docker image is a static template used to create containers, while a container is a running instance of that image with a writable layer. Think of an image as a class and a container as an object instantiated from that class. Containers are ephemeral; images are persistent and versioned.
Q: How do I optimize Docker images for security?
Optimize images by using minimal base OSes (e.g., Alpine Linux), running as a non-root user, removing unnecessary packages, and leveraging multi-stage builds. Regularly scan images for vulnerabilities using tools like Trivy or Docker Scout, and avoid pulling images with the `latest` tag in production.
Q: What happens if I delete a Docker image?
Deleting a Docker image removes it from your local storage and registry, but containers created from that image will continue running until stopped. To safely remove an image, first stop and remove any associated containers. Use `docker system prune` to clean up unused images, networks, and build cache.
Q: Can Docker images be used outside of Docker?
Yes. Docker images follow the Open Container Initiative (OCI) specification, making them compatible with other container runtimes like Podman, containerd, or Kubernetes. Tools like `skopeo` allow you to copy images between registries without requiring Docker itself.
Q: How do I share a Docker image with others?
Push your image to a container registry (e.g., Docker Hub, GitHub Container Registry, or AWS ECR) using `docker push`. Ensure the image is tagged with a meaningful version (e.g., `myapp:v1.0`) and include a `README` with build instructions. Private registries often require authentication.
Q: What’s the best way to debug issues with a Docker image?
Start by inspecting the image with `docker inspect
Q: Are Docker images suitable for stateful applications?
Docker images are stateless by design, but you can persist data using volumes or bind mounts. For stateful applications, consider orchestration tools like Kubernetes with StatefulSets or databases that support external storage backends. Avoid storing application data directly in containers.
Q: How do I reduce the size of a Docker image?
Minimize image size by using multi-stage builds to discard build-time dependencies, choosing smaller base images (e.g., `gcr.io/distroless`), and cleaning up caches with `.dockerignore`. Tools like `docker-slim` can further optimize images by removing unused files.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.