How Open Source Code Scanning Tools Are Redefining Security and Efficiency
Table of Contents
- The Complete Overview of Open Source Code Scanning Tools
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do open source code scanning tools compare to proprietary alternatives?
- Q: Can open source scanning tools replace manual code reviews?
- Q: Are there any performance overheads associated with open source scanning?
- Q: How do I choose the right open source scanning tool for my team?
- Q: Can open source scanning tools handle multi-language projects?
- Q: What’s the most common mistake teams make when implementing these tools?
- Q: Are there any legal or compliance risks with open source scanning tools?
- Q: How can I reduce false positives in open source scanning?
The race to secure software begins long before deployment—it starts in the codebase itself. Open source code scanning tools have emerged as the unsung heroes of modern development, embedding security deep into the pipeline. These tools don’t just flag vulnerabilities; they reshape how teams think about risk, compliance, and efficiency. From identifying hardcoded secrets to detecting logic flaws, their capabilities are expanding faster than ever, yet their adoption remains uneven. Why? Because the landscape is fragmented, and not all solutions deliver equal value.
What sets apart the most effective open source code scanning tools isn’t just their ability to scan—it’s their integration with workflows, their adaptability to evolving threats, and their capacity to reduce alert fatigue. Developers and security teams now face a critical choice: rely on proprietary solutions with locked-in dependencies or leverage open source alternatives that offer transparency, customization, and community-driven improvements. The decision isn’t just technical; it’s strategic.
The stakes are higher than ever. A single oversight in early-stage code review can lead to breaches costing millions, reputational damage, or regulatory penalties. Yet many organizations still treat security scanning as an afterthought, bolting it on at the end of the development cycle. The most forward-thinking teams are embedding open source code scanning tools directly into their CI/CD pipelines, treating them as essential infrastructure—not optional add-ons.
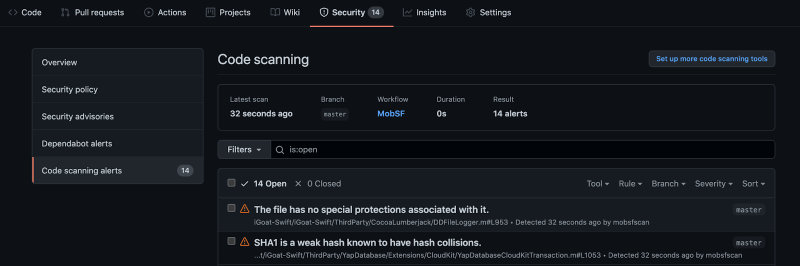
The Complete Overview of Open Source Code Scanning Tools
Open source code scanning tools represent a paradigm shift in how software security is approached. Unlike traditional vulnerability scanners that operate in isolation, these tools are designed to integrate seamlessly with modern development practices. They operate across multiple layers—static analysis for source code, dynamic analysis for runtime behavior, and even secret detection for credentials or API keys. What makes them particularly powerful is their ability to adapt. Open source projects like SonarQube, Semgrep, and Trivy are continuously updated by global communities, ensuring they stay ahead of emerging threats without vendor lock-in.
The core value proposition lies in their dual role: they serve as both a preventive measure and a compliance enabler. For developers, they provide immediate feedback during coding, reducing the need for costly rework. For security teams, they offer granular insights into potential risks, often before they materialize into incidents. The best open source code scanning solutions don’t just generate reports—they contextualize findings, prioritize critical issues, and even suggest remediation paths. This shift from reactive to proactive security is what’s driving their adoption in enterprises of all sizes.
Historical Background and Evolution
The origins of code scanning trace back to the early 2000s, when static analysis tools like Fortify and Coverity emerged as proprietary solutions for enterprise security. These tools were expensive, complex, and often required specialized expertise to deploy. The open source movement changed that. Projects like SonarQube, launched in 2008, democratized code quality analysis by making it accessible to small teams and startups. Meanwhile, the rise of GitHub in 2008 and later GitLab accelerated the need for lightweight, scalable scanning tools that could operate at the repository level.
Today, the evolution of open source code scanning tools is being shaped by three key factors: the growth of DevSecOps, the proliferation of cloud-native applications, and the increasing complexity of supply chains. Tools like Trivy (by Aqua Security) and Semgrep (by Ruxit) have gained traction by addressing specific pain points—Trivy for container security, Semgrep for rule-based static analysis. Meanwhile, frameworks like OWASP Dependency-Check have become industry standards for managing third-party risks. The result? A tooling ecosystem that’s more specialized, more integrated, and more responsive to real-world threats than ever before.
Core Mechanisms: How It Works
At their core, open source code scanning tools rely on a combination of pattern matching, abstract syntax tree (AST) analysis, and machine learning (in some advanced cases). Static analysis tools like SonarQube parse code without executing it, looking for known vulnerabilities, coding standards violations, and architectural flaws. Dynamic analysis tools, such as those used in OWASP Amass, monitor applications in runtime to detect issues like memory leaks or injection flaws. Secret scanning tools, such as GitLeaks, use regular expressions and entropy analysis to identify hardcoded secrets in repositories.
The most sophisticated tools go beyond basic scanning. For example, Semgrep uses a rule-based engine that allows developers to define custom patterns for detecting vulnerabilities specific to their tech stack. Trivy, on the other hand, combines static analysis with vulnerability databases (like NVD) to provide real-time risk assessments for containers and infrastructure-as-code (IaC) files. The key innovation here is context-aware scanning—tools that understand not just the code, but the environment in which it operates, enabling more accurate and actionable results.
Key Benefits and Crucial Impact
The adoption of open source code scanning tools isn’t just about finding bugs—it’s about transforming security into a collaborative, scalable process. By integrating scanning into the development lifecycle, teams can shift left, addressing vulnerabilities early when they’re cheapest to fix. This reduces the time and cost associated with remediation while improving overall software quality. For organizations with compliance requirements (such as GDPR, HIPAA, or PCI DSS), these tools provide the audit trails and reporting needed to demonstrate due diligence.
Yet the impact extends beyond technical outcomes. Open source scanning fosters a culture of security ownership, where developers take responsibility for writing secure code rather than relying solely on security teams. This cultural shift is critical in an era where security breaches are often attributed to human error—whether it’s a misconfigured dependency or an overlooked vulnerability in open source libraries. The right open source code scanning solution doesn’t just find problems; it educates the team on how to prevent them.
"Security isn’t a product; it’s a process. The best open source scanning tools don’t just scan—they enable the process of continuous improvement."
— Mark Curphey, Founder of OWASP
Major Advantages
- Cost Efficiency: Eliminates licensing fees associated with proprietary tools, making advanced security accessible to startups and enterprises alike.
- Customization and Extensibility: Open source tools allow teams to tailor scanning rules, integrations, and workflows to their specific needs, reducing false positives and improving relevance.
- Transparency and Trust: With full access to the source code, organizations can verify how vulnerabilities are detected and how data is handled, addressing concerns around proprietary "black boxes."
- Community-Driven Updates: Rapid iteration based on real-world threat intelligence ensures tools stay current with emerging vulnerabilities (e.g., log4j, Heartbleed).
- Seamless Integration: Most open source scanning tools offer plugins for CI/CD pipelines (Jenkins, GitHub Actions, GitLab CI), enabling automated security checks without disrupting workflows.
Comparative Analysis
Not all open source code scanning tools are created equal. The choice depends on specific use cases—whether it’s static analysis, container security, or secret detection. Below is a comparison of four leading tools based on key criteria:
| Tool | Primary Use Case | Strengths | Limitations |
|---|---|---|---|
| SonarQube | Static code analysis (SAST) | Comprehensive quality metrics, strong language support, enterprise-grade reporting. | Resource-intensive; requires setup for optimal performance. |
| Semgrep | Rule-based static analysis | Lightweight, fast, and highly customizable with YAML-based rules. | Limited dynamic analysis capabilities; relies on community rules. |
| Trivy | Container and IaC security | Fast scanning for vulnerabilities in containers, Kubernetes, and cloud configs. | Less suited for deep static analysis of application code. |
| GitLeaks | Secret detection | Highly effective at identifying exposed credentials in repositories. | Narrow focus; not a replacement for broader SAST tools. |
Future Trends and Innovations
The next generation of open source code scanning tools will be defined by three major trends: AI-driven analysis, supply chain security, and real-time threat intelligence. Tools like GoSec are already experimenting with machine learning to improve vulnerability detection accuracy. Meanwhile, the rise of SLSA (Supply-chain Levels for Software Artifacts) is pushing scanning tools to verify not just code, but the entire build and deployment process. Expect to see more integration with SPDX for automated license compliance and Syft for artifact inventory management.
Another critical evolution will be the convergence of scanning with cloud-native security. As organizations adopt serverless architectures and multi-cloud deployments, tools will need to adapt to scan functions-as-a-service (FaaS), serverless containers, and edge computing environments. Open source projects like kube-bench are already leading the way in Kubernetes security, but the future lies in tools that can provide a unified view across hybrid and multi-cloud landscapes. The goal? A single pane of glass for security, where scanning isn’t just a step in the pipeline—but a continuous, context-aware process.
Conclusion
The adoption of open source code scanning tools is no longer optional; it’s a necessity for organizations serious about security and efficiency. These tools bridge the gap between development speed and risk mitigation, offering a scalable, transparent, and collaborative approach to software security. The key to success lies in selecting the right tools for specific needs—whether it’s static analysis, container security, or secret detection—and integrating them early in the development lifecycle.
As the threat landscape evolves, so too will the capabilities of these tools. The most resilient organizations will be those that treat open source scanning not as a one-time audit, but as an ongoing dialogue between developers, security teams, and the tools themselves. The future of secure software isn’t just about finding vulnerabilities—it’s about building a culture where security is everyone’s responsibility, and the right open source code scanning solutions are the foundation of that culture.
Comprehensive FAQs
Q: How do open source code scanning tools compare to proprietary alternatives?
A: Open source tools offer transparency, customization, and cost savings, but may require more setup and maintenance. Proprietary tools often provide polished UIs and dedicated support, but can be restrictive in terms of rule customization and licensing costs. The choice depends on whether your team prioritizes flexibility or ease of use.
Q: Can open source scanning tools replace manual code reviews?
A: No, they complement manual reviews. While tools excel at detecting known patterns and vulnerabilities, human judgment is still essential for contextual analysis, business logic flaws, and creative attack vectors. The best approach is to use automation for repetitive checks and reserve human expertise for high-risk areas.
Q: Are there any performance overheads associated with open source scanning?
A: Yes, but it varies by tool. Heavy static analyzers like SonarQube can slow down CI pipelines if not optimized. Lightweight tools like Semgrep or Trivy are designed for speed, often completing scans in seconds. Performance depends on the tool’s architecture, the complexity of the codebase, and how it’s integrated into the workflow.
Q: How do I choose the right open source scanning tool for my team?
A: Start by identifying your primary security goals (e.g., SAST, container security, secret detection). Then evaluate tools based on language support, ease of integration, customization options, and community activity. For example, if you work with Kubernetes, Trivy may be ideal; if you need deep static analysis, SonarQube or Semgrep could be better.
Q: Can open source scanning tools handle multi-language projects?
A: Many modern tools support multiple languages. SonarQube, for instance, covers Java, Python, JavaScript, and more. Semgrep also supports a wide range of languages via its rule engine. However, coverage depth varies—some tools may offer basic checks for niche languages but lack advanced analysis capabilities.
Q: What’s the most common mistake teams make when implementing these tools?
A: Treating scanning as a checkbox rather than a continuous process. Many teams run scans once and ignore results, leading to alert fatigue. The best practice is to integrate scanning into every commit, enforce remediation policies, and treat findings as actionable feedback—not just reports.
Q: Are there any legal or compliance risks with open source scanning tools?
A: Generally no, but it’s important to ensure the tool’s licensing aligns with your organization’s policies (e.g., Apache 2.0 is widely compatible). Additionally, some tools may collect anonymized data for improvement—review their privacy policies if handling sensitive code. For regulated industries, verify that the tool’s output meets audit requirements (e.g., generating exportable reports).
Q: How can I reduce false positives in open source scanning?
A: Start by tuning the tool’s default rules to match your codebase’s patterns. Many tools (like SonarQube) allow rule customization or suppression for known-safe issues. Collaborate with your security team to define thresholds for critical vs. low-severity findings. Finally, use a phased rollout—start with a subset of repositories to refine rules before scaling.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.