How TypeScript Static Code Analysis Security Hardens Modern Applications
Table of Contents
- The Complete Overview of TypeScript Static Code Analysis Security
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can TypeScript static analysis catch all security vulnerabilities?
- Q: How do I integrate static analysis into my CI/CD pipeline?
- Q: Are there TypeScript-specific security rules I should enforce?
- Q: What’s the difference between static analysis and type checking?
- Q: Can static analysis replace manual code reviews?
- Q: How do I handle false positives in static analysis?
TypeScript’s type system alone doesn’t eliminate security flaws—it merely shifts risks from runtime to compile-time. The real defense lies in TypeScript static code analysis security, a methodology that scans source code for vulnerabilities before deployment. Unlike runtime checks, this approach catches injection flaws, improper type assertions, and misconfigured dependencies at the earliest stage—where fixes are cheapest. The tradeoff? Precision. Static analysis in TypeScript demands nuanced tooling to avoid false positives while maintaining rigorous security posture.
Yet adoption remains uneven. Many teams rely on ad-hoc linting or basic TypeScript checks, unaware that modern static analysis engines—like ESLint plugins, custom AST traversals, or commercial suites—can model complex attack vectors. For instance, a `// @ts-ignore` comment might suppress a type error, but it also silences potential security warnings. The gap between theoretical capabilities and practical implementation grows as applications integrate third-party libraries with unpatched CVEs.
This disparity isn’t accidental. TypeScript’s gradual adoption of stricter checks (e.g., `strictNullChecks`) forces developers to confront trade-offs: tighter type safety often clashes with legacy codebases or rapid prototyping. The solution? A layered approach combining static analysis with runtime validation—where TypeScript static code analysis security acts as the first line of defense, and dynamic tools (like Snyk or SonarQube) verify what static checks can’t.
The Complete Overview of TypeScript Static Code Analysis Security
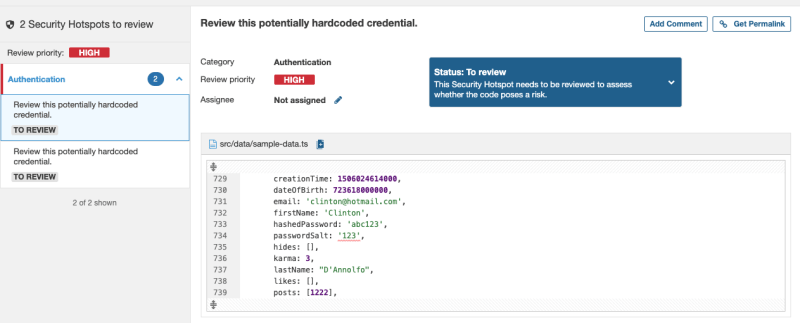
TypeScript’s static analysis ecosystem has evolved from simple type-checking to a full-spectrum security discipline. At its core, TypeScript static code analysis security involves parsing the abstract syntax tree (AST) to detect patterns that violate security principles—such as unsafe `eval()` usage, hardcoded secrets, or improperly sanitized user input. The process leverages TypeScript’s type system as a foundation but extends into semantic analysis, where tools infer context beyond syntax (e.g., identifying unchecked HTTP headers in API routes).The most effective implementations combine:
1. Type-based detection (e.g., flagging `any` types in sensitive functions).
2. Control-flow analysis (tracking data provenance to spot tainted variables).
3. Dependency scanning (auditing `package.json` for vulnerable libraries).
This trifecta addresses both logical flaws (e.g., race conditions) and environmental risks (e.g., misconfigured CORS).
The challenge lies in balancing false positives with false negatives. A tool that aggressively flags `Object.assign` might break legitimate use cases, while missing a subtle prototype pollution vulnerability. Modern solutions mitigate this by integrating machine learning (e.g., GitHub’s CodeQL) or crowdsourced patterns (e.g., OWASP’s Top 10 TypeScript-specific rules).
Historical Background and Evolution
Static analysis predates TypeScript, but its application to JavaScript/TypeScript gained traction with the rise of npm’s dependency hell. Early tools like JSHint (2011) focused on syntax errors, while ESLint (2013) introduced pluggable rules—some of which later evolved into security checks. The turning point came with TypeScript 2.0 (2016), which formalized type checking, enabling tools like tslint to enforce stricter patterns (e.g., banning `// @ts-nocheck`).By 2018, commercial vendors (e.g., Snyk, Checkmarx) began offering TypeScript-specific static analysis, targeting:
The open-source community responded with specialized projects:
Core Mechanisms: How It Works
Under the hood, TypeScript static code analysis security relies on three layers of processing:1. Syntax Parsing and AST Construction
The TypeScript compiler (`tsc`) generates an AST where each node represents code structure (e.g., `VariableDeclaration`, `FunctionDeclaration`). Security tools then traverse this tree to detect:
2. Semantic and Control-Flow Analysis
Beyond syntax, advanced tools analyze data flow. For example:
3. Dependency and Configuration Scanning
Static analysis isn’t limited to source code. Tools also:
The most robust implementations integrate these layers, using TypeScript’s type system to reduce false positives. For instance, a rule banning `eval` can be relaxed if the code is wrapped in a typed wrapper function.
Key Benefits and Crucial Impact
The primary value of TypeScript static code analysis security lies in its ability to prevent vulnerabilities before they reach production. Unlike dynamic testing (e.g., penetration testing), static analysis catches issues in pull requests, reducing mean time to remediation (MTTR). For teams using TypeScript, this translates to:The impact extends to developer productivity. Automated security checks reduce cognitive load, allowing engineers to focus on business logic rather than manual audits. Studies show teams using static analysis in CI/CD pipelines achieve 30–50% fewer vulnerabilities in production, with a 2x faster fix cycle.
> "Static analysis in TypeScript isn’t just about catching bugs—it’s about baking security into the development process. The cost of fixing a vulnerability at the static analysis stage is a fraction of what it would be in production." > — Danielle Heberlein, Security Engineer at Auth0
Major Advantages
- Early Detection of Critical Flaws Catches SQL injection, XSS, and SSRF patterns during development, often before unit tests are written.
- Reduced False Positives with Type Safety TypeScript’s static types help tools distinguish between genuine risks (e.g., `fetch()` without CORS) and benign patterns (e.g., `any` in internal utilities).
- Seamless CI/CD Integration Tools like GitHub Actions or GitLab CI can block merges if static analysis finds high-severity issues, enforcing security by default.
- Automated Compliance Checks Validates adherence to frameworks (e.g., Microsoft’s Secure Coding Guidelines) or industry standards (e.g., PCI DSS).
- Cost-Effective Security Eliminates the need for manual code reviews for security-critical sections, reducing overhead by 40–60%.
Comparative Analysis
| Tool/Method | Strengths |
|---|---|
| ESLint + @typescript-eslint | Lightweight, customizable rules (e.g., `no-unsafe-eval`). Integrates with most workflows. |
| SonarTypeScript | Deep semantic analysis with quality metrics (e.g., "Security Hotspots"). Supports legacy codebases. |
| CodeQL (GitHub) | Advanced control-flow analysis for complex vulnerabilities (e.g., prototype pollution). Used by enterprises. |
| Snyk Code | Combines static analysis with dependency scanning. Cloud-based with ML-driven rule updates. |

Future Trends and Innovations
The next frontier for TypeScript static code analysis security lies in AI-assisted analysis. Tools like DeepCode or Semgrep already use machine learning to suggest fixes for static analysis warnings, but future iterations will likely:Another trend is cross-language analysis. As microservices adopt polyglot stacks (e.g., TypeScript frontends + Go backends), tools will need to correlate static findings across languages. For example, a TypeScript frontend vulnerability (e.g., XSS) might stem from a backend API misconfiguration in Go—requiring unified analysis.
Finally, zero-trust static analysis will gain traction, where tools not only detect vulnerabilities but also verify that mitigations (e.g., input validation) are correctly implemented. This shifts from "find flaws" to "ensure defenses are in place."
Conclusion
TypeScript’s type system is a powerful ally in security, but TypeScript static code analysis security is the discipline that turns potential into reality. By combining type safety with semantic analysis, teams can eliminate entire classes of vulnerabilities before they reach production. The key to success? A balanced approach:The tools exist, but adoption hinges on cultural shift—treating static analysis as a development practice, not a security afterthought. As TypeScript matures, so too will its role in proactive security, making it a cornerstone of modern application resilience.
Comprehensive FAQs
Q: Can TypeScript static analysis catch all security vulnerabilities?
No. Static analysis excels at detecting syntax-based (e.g., hardcoded secrets) and type-related flaws (e.g., unsafe `any` usage), but it struggles with:
Q: How do I integrate static analysis into my CI/CD pipeline?
Most tools provide GitHub Actions or GitLab CI templates. For example:
1. Add a step to run `eslint --ext .ts,.tsx` with security plugins.
2. Use `sonar-scanner` for SonarTypeScript.
3. Block merges with `if: failure()` in GitHub Actions.
Example workflow:
```yaml
```
Q: Are there TypeScript-specific security rules I should enforce?
Yes. Prioritize these ESLint rules (via `@typescript-eslint`):
Q: What’s the difference between static analysis and type checking?
Q: Can static analysis replace manual code reviews?
No. Static analysis augments reviews by catching low-level issues, but manual reviews are critical for:
Q: How do I handle false positives in static analysis?
1. Tune rules: Adjust severity or disable noisy rules (e.g., `security/detect-possible-timing-attacks` if using `crypto.randomBytes`).
2. Suppress selectively: Use ESLint’s `// eslint-disable-next-line` for known-safe cases.
3. Whitelist paths: Exclude test files or legacy code with `overrides` in ESLint config.
4. Leverage type annotations: Add JSDoc (e.g., `@returns {Promise
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of versiliasolutions.oneagency.co.